 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs

Quick Overview: Security testing helps uncover weaknesses before they become serious security risks. This guide explains the different types and methods of security testing, including SAST, DAST, IAST, SCA, RASP, manual, and automated testing. It also covers security testing best practices, when testing should be performed, how to choose the right approach, and how these methods differ from penetration testing.
A single security test cannot keep up with an application that changes every day. In 2025, 48,185 new CVEs were published, averaging about 133 vulnerabilities every day.
That growing attack surface makes knowing how to test just as important as testing itself. Different methods uncover different weaknesses, from insecure code and vulnerable dependencies to exploitable attack paths.
Manual testing can uncover logic flaws that automated tools miss. Automated testing, meanwhile, provides the speed and coverage needed for modern development cycles. The right approach often combines both.
This guide breaks down the different types and methods of security testing, when to use each, and how to choose the right approach. It also explains when you should perform application security testing to make sure you detect each vulnerability and eliminate them before they turn into threat.
Security testing shouldn't wait for your next release cycle. Set up continuous coverage in minutes. Launch My Free Trial
On This Page
- What is Security Testing?
- What are the Different Types of Security Testing?
- What are the Different Types of Security Testing Methods?
- How to Choose the Right Security Testing Approach?
- How Security Testing Process Works: Step-by-Step
- Security Testing Best Practices for Software
- When Should Security Testing Be Performed?
- Summing Up
What is Security Testing?
Security testing is the process of evaluating an application, system, network, or infrastructure to identify security vulnerabilities and weaknesses. It helps determine whether security controls can protect sensitive data and prevent unauthorized access.
The testing process examines areas such as authentication, authorization, access controls, encryption, input validation, configurations, and session management. Depending on the scope, teams may test web applications, APIs, mobile apps, cloud environments, networks, or connected systems.
Security testing can be performed manually, automatically, or through a combination of both approaches. Automated tools can identify common vulnerabilities at scale, while manual testing can uncover complex attack paths, business logic flaws, and weaknesses that automated scans may miss.
The goal is not simply to find vulnerabilities. Effective security testing validates their real-world impact, assesses the risk they create, and provides actionable findings that security and development teams can prioritize for remediation.
What are the Different Types of Security Testing?
Security testing includes several approaches that help organizations identify vulnerabilities, validate security controls, assess risk, and uncover exploitable weaknesses across applications, systems, networks, and infrastructure.
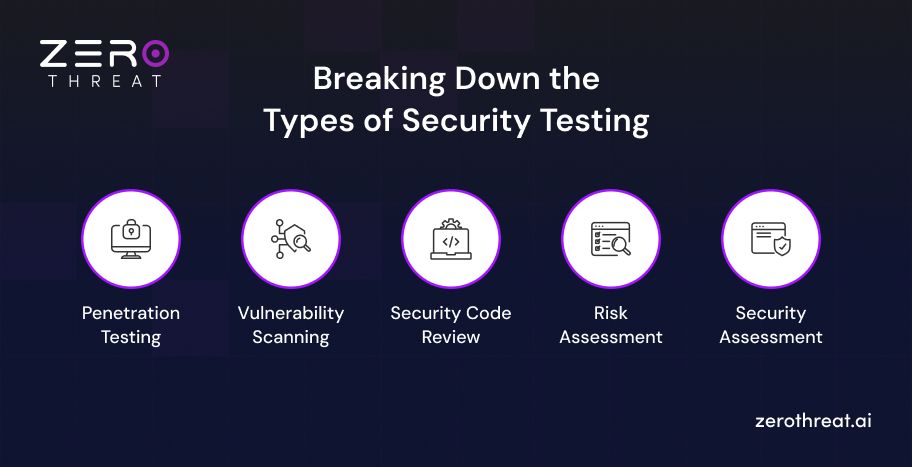
Penetration Testing
Penetration testing, or pen testing, simulates a real cyberattack against your application, network, or infrastructure. Testers use the same tactics as threat actors, probing for exploitable weaknesses in authentication, APIs, and business logic. The goal is to prove whether a vulnerability can actually be exploited.
This approach goes beyond scanning. It shows the exact attack path an intruder would take, along with the business impact if that path stays open. Most compliance frameworks like PCI DSS and SOC 2 require periodic penetration tests to validate real-world security posture.
Vulnerability Scanning
Vulnerability scanning uses automated tools to scan systems, networks, and applications for known security flaws. It checks against databases like CVE to flag outdated software, missing patches, and misconfigurations, making it a strong first line of defense across large environments.
But scanning only identifies potential issues, it doesn't confirm exploitability. False positives are common, and results still need manual validation. Regular scans, ideally weekly or after every deployment, keep your attack surface visible and catch new vulnerabilities before attackers find them.
Security Code Review
Security code review examines source code line by line to catch vulnerabilities before an application ever goes live. Reviewers look for insecure coding patterns, hardcoded credentials, injection flaws, and broken access control logic. It can be manual, automated through SAST tools, or both.
This type of testing catches root-cause issues that dynamic testing often misses entirely. Since it happens early in development, fixing flaws here costs far less than patching them after release. Pairing manual review with automated static analysis gives you the most complete coverage.
Risk Assessment
Risk assessment evaluates the likelihood and impact of potential threats against your assets, rather than just listing vulnerabilities. It factors in asset value, threat probability, and existing controls to calculate an actual risk score. This helps prioritize what to fix first.
Not every vulnerability deserves the same urgency. Risk assessment gives security teams a clear, data-backed way to allocate limited time and budget toward the threats that matter most. Frameworks like NIST SP 800-30 and ISO 27005 standardize this process across industries.
Security Assessment
Security assessment takes a step back and evaluates your organization's overall security readiness, not just one system or application. It reviews policies, access controls, incident response plans, and existing security tools together, exposing gaps individual tests can't reveal alone.
This assessment gives leadership a benchmark, showing where the organization stands against frameworks like NIST CSF or ISO 27001. It's less about finding a single flaw and more about understanding your organization's overall resilience against evolving threats.
Automated testing catches what manual reviews miss and do it continuously, without slowing your team down. Test My Application
What are the Different Types of Security Testing Methods?
Security testing methods use different techniques to identify vulnerabilities across the software development lifecycle. The right approach depends on when testing occurs, what is being tested, and how deeply security risks must be validated.
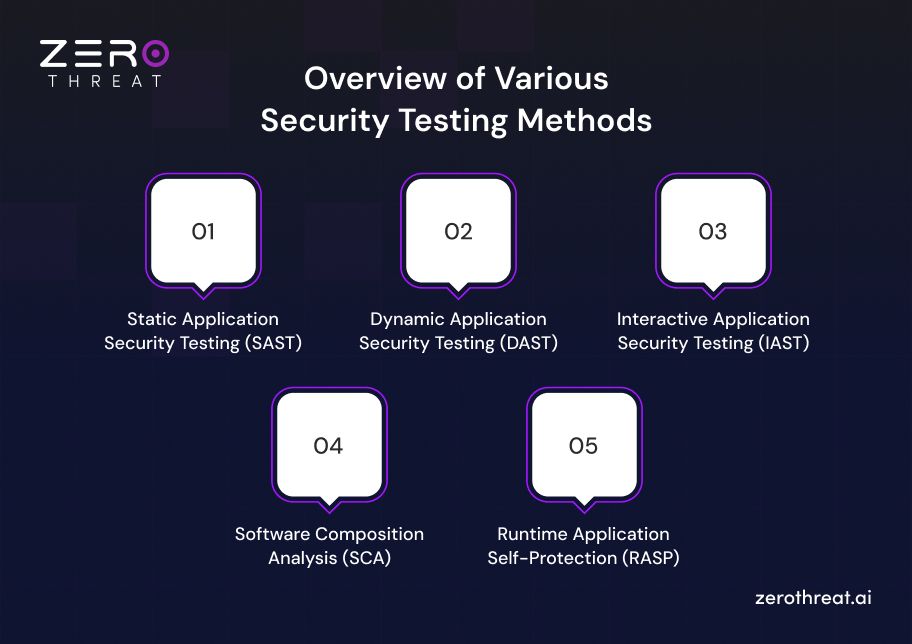
1. Static Application Security Testing (SAST)
SAST analyzes an application's source code, bytecode, or binaries without executing the application. It identifies coding-level vulnerabilities such as SQL injection, hardcoded secrets, insecure functions, and improper input validation early in development.
Key Features:
- Source code analysis
- Early vulnerability detection
- CI/CD integration
- Coding flaw identification
- Developer-focused findings
Strengths of SAST:
- Finds vulnerabilities early
- Supports secure coding practices
- Integrates into development workflows
- Helps reduce remediation costs
2. Dynamic Application Security Testing (DAST)
DAST tests running applications from an external perspective to identify vulnerabilities that appear during execution. It analyzes application behavior, HTTP responses, authentication flows, and exposed endpoints without requiring access to source code.
Key Features:
- Black-box testing
- Runtime vulnerability detection
- Web application scanning
- API endpoint testing
- Authentication testing
Strengths of DAST:
- Tests real application behavior
- Does not require source code
- Detects runtime security issues
- Helps assess externally exposed attack surfaces
3. Interactive Application Security Testing (IAST)
IAST combines aspects of static and dynamic analysis by monitoring an application while it runs. It uses agents or sensors inside the application to analyze execution paths and identify vulnerabilities with contextual information.
Key Features:
- Runtime code analysis
- Application instrumentation
- Execution-path monitoring
- Real-time vulnerability detection
- Context-rich findings
Strengths of IAST:
- Combines static and dynamic analysis
- Provides deeper vulnerability context
- Reduces unnecessary findings
- Identifies vulnerabilities during application execution
- Supports continuous security testing
4. Software Composition Analysis (SCA)
Software Composition Analysis (SCA) examines third-party and open-source components used within an application. It identifies known vulnerabilities, outdated dependencies, license risks, and software supply chain weaknesses that could expose applications to security threats.
Key Features:
- Open-source dependency analysis
- CVE identification
- License compliance checks
- Software bill of materials (SBOM)
- Dependency monitoring
Strengths of SCA:
- Identifies vulnerable dependencies
- Improves software supply chain security
- Supports license compliance
- Helps prioritize dependency updates
5. Runtime Application Self-Protection (RASP)
Runtime Application Self-Protection (RASP) monitors application behavior during execution and detects potentially malicious activity. It can analyze application requests, execution flows, and runtime events to identify and block attacks before they cause damage.
Key Features:
- Runtime threat detection
- Application-level monitoring
- Attack prevention
- Context-aware analysis
- Runtime protection
Strengths of RASP:
- Protects applications during execution
- Detects attacks in real time
- Provides application-level visibility
- Can block malicious activity
How to Choose the Right Security Testing Approach?
The right security testing approach depends on your assets, security objectives, risk exposure, development stage, testing scope, and available resources. A combination of methods often provides broader security coverage.
Step 1: Define Your Security Objectives
Start by identifying what you need the testing to accomplish. Determine whether the goal is to discover vulnerabilities, validate security controls, assess compliance, verify remediation, or understand real-world attack paths. Clear objectives help narrow down the appropriate testing methods.
Step 2: Identify the Assets
Determine which assets require assessment, such as web applications, APIs, mobile applications, networks, cloud infrastructure, source code, or third-party dependencies. Prioritize critical systems and sensitive data based on their business importance and potential impact.
Step 3: Assess Your Risk
Consider the threats, vulnerabilities, attack surface, and potential business impact associated with each asset. A risk-based approach helps focus testing resources on areas where exploitation could cause the greatest damage rather than applying the same testing depth everywhere.
Step 4: Consider the Development Stage
Choose testing methods based on where the application is in the software development lifecycle. SAST and code review can identify weaknesses during development, while DAST, penetration testing, and runtime testing can evaluate deployed applications and their behavior.
Step 5: Choose the Testing Depth
Decide whether you need broad vulnerability discovery or deeper validation of specific security weaknesses. Automated scanning can provide scalable coverage, while manual testing and penetration testing can investigate complex vulnerabilities, business logic flaws, and attack paths.
Step 6: Account for Compliance Needs
Identify the security standards, regulations, contractual requirements, and internal policies that apply to the environment. Your testing approach should produce the evidence and documentation needed to demonstrate that relevant security controls and requirements have been assessed.
Step 7: Combine Multiple Methods
Avoid relying on a single testing technique when your risk profile requires broader coverage. Combining automated and manual testing, vulnerability assessment, code analysis, and penetration testing can reveal different categories of weaknesses and provide a more complete view of application security. NIST specifically presents multiple testing techniques and notes that organizations can combine approaches based on their needs.
Step 8: Plan for Continuous Testing
Security testing should not end after a single assessment. Reassess applications as code, dependencies, configurations, and attack surfaces change. Integrating appropriate automated security testing into development and deployment workflows can help maintain security visibility throughout the application lifecycle.
Enterprise-grade security testing shouldn't come with an enterprise-only price tag attached to it. See Plans & Pricing
How Security Testing Process Works: Step-by-Step
There are several steps in a typical security testing process. It offers a structured approach to identify and address security vulnerabilities. Let’s check out all the steps in security testing.
Step 1: Plan and Gather Information
Firstly, you need to define the scope of security testing. For this, start by identifying the systems, applications, or components that need to be tested. Further, define the kinds of testing you need to perform, such as pen testing or automated vulnerability scanning. Finally, define the objectives of the test.
Step 2: Identify the Potential Risks
You need to identify the potential risks as well as understand your attack surface, possible threat vectors, and vulnerable areas. Here, you need threat modeling to discover potential risks to your organization and make a prudent cybersecurity strategy.
Step 3: Create Test Cases
The next step is to create test cases for performing simulated attacks. These test cases are designed considering the information collected about the potential risks and attack surface. Every test case should have a clear objective, expected outcome, success criteria, and other information.
Step 4: Execute Security Tests
Once the test cases have been designed, the next steps involve executing the tests accordingly. Perform security testing like penetration testing or vulnerability scanning with tools like DAST or SAST. Document and report any security weaknesses detected.
Step 5: Analyze the Security Weaknesses
Next, you need to analyze the test results to evaluate the impact and severity of each vulnerability. All vulnerabilities must be documented and prioritized based on their severity and impact. The document will be a reference to address and mitigate the security risks.
Step 6: Fix Vulnerabilities
After the findings, the security team and developers work together to address the identified vulnerabilities. There could be various methods to fix vulnerabilities, including adding new security controls, patching software, and reconfiguring systems.
Step 7: Perform Re-tests for Validation
After all the vulnerabilities have been addressed, you need to perform re-tests to validate them. The re-testing ensures that the vulnerabilities have been eliminated effectively, and it also finds any issues that persist.
Step 8: Continuous Testing
Security testing isn’t a one-time task; it is a continuous process. Since cyber threats keep evolving and increasing, continuous testing helps identify and address them before they pose a critical challenge for organizations.
Security Testing Best Practices for Software
Strong security testing depends on more than picking the right tools. These best practices help teams build a consistent, scalable process that catches vulnerabilities early and reduces overall risk exposure.
Shift Security Left
Shifting security left means testing code as early as possible, starting at the commit stage rather than after deployment. Integrating SAST and SCA into your IDE and CI/CD pipeline catches vulnerabilities before they reach production, cutting remediation costs and reducing the attack surface significantly.
Automate Testing Workflows
Automated testing workflows run consistently across every build, without relying on manual triggers. Integrating DAST and vulnerability scanning into your CI/CD pipeline ensures every deployment gets checked. This keeps security testing scalable, reduces human error, and maintains coverage even as release cycles speed up.
Prioritize Vulnerabilities by Risk
Not every vulnerability deserves equal urgency. Prioritizing by risk means factoring in exploitability, asset value, and business impact before assigning remediation timelines. Frameworks like CVSS help score severity, letting security teams focus limited resources on flaws that pose the greatest actual threat first.
Secure Third-Party Dependencies
Most applications run on open-source components, making dependency risk unavoidable. Running regular SCA scans identifies outdated packages, known CVEs, and license conflicts hiding in your software supply chain. Generating a software bill of materials keeps visibility high across every dependency your application relies on.
Train Development Teams
Developers who understand secure coding practices introduce fewer vulnerabilities in the first place. Regular training on injection flaws, authentication weaknesses, and the OWASP Top 10 builds security awareness directly into daily workflows, reducing the volume of issues security testing has to catch later.
Establish Remediation Workflows
Finding vulnerabilities means little without a clear process to fix them. Establishing remediation workflows assigns ownership, sets deadlines based on severity, and tracks fixes through resolution. This turns security testing results into measurable action instead of a growing, unaddressed backlog of open findings.
When Should Security Testing Be Performed?
Security testing should be performed throughout the software development lifecycle, not only before release. Testing at key stages helps teams catch vulnerabilities early and maintain security as applications evolve.
- During Development: Use SAST and code reviews to identify insecure coding practices before vulnerabilities move into later development stages.
- Before Deployment: Run DAST, vulnerability scans, and configuration checks to uncover security weaknesses before releasing applications into production.
- After Major Changes: Perform security testing after significant code, architecture, API, dependency, or infrastructure changes that could introduce new vulnerabilities.
- After Security Incidents: Retest affected systems after an incident to identify remaining weaknesses, validate fixes, and prevent similar attacks.
- Continuously: Integrate automated security testing into CI/CD pipelines to monitor changing attack surfaces and detect vulnerabilities throughout the application lifecycle.
Not sure which testing method fits your application best? Our security team can help. Contact Us
Summing Up
Security is never the result of one test or one tool. Different methods address different security concerns, from vulnerable source code and dependencies to runtime weaknesses, exposed attack surfaces, and exploitable application flaws.
SAST, DAST, IAST, SCA, RASP, manual testing, and automated testing each provide distinct visibility. Choosing the right combination depends on the application, development stage, risk exposure, testing goals, and available resources.
Effective security testing also requires consistent practices. Shifting security left, automating recurring checks, validating findings, prioritizing vulnerabilities by risk, and maintaining clear remediation workflows can strengthen application security throughout the development lifecycle.
The strongest approach is continuous and risk-based. Combining automated coverage with expert analysis helps organizations identify weaknesses earlier, validate their real impact, and build applications that are more resilient against evolving cyber threats.
Frequently Asked Questions
What are the different security testing best practices?
The core best practices include shifting security left, automating testing workflows, combining automated and manual testing, prioritizing vulnerabilities by risk, securing third-party dependencies, training development teams on secure coding, and establishing clear remediation workflows for every finding.
What are the key benefits of security testing?
Is security testing performed automatically or manually?
Can automated testing replace a manual penetration test?
What is the difference between SAST vs DAST vs IAST?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.