 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs
What is Multi-Factor Authentication? Understanding Its Importance in Cyber Security

Quick Overview: Multi-factor authentication has become essential for protecting modern accounts against credential theft. This guide covers what MFA is, how it works, the different authentication factors, and common MFA methods. It explains why MFA matters, how attackers attempt to bypass it, and the practical best practices for implementing stronger MFA security.
A password alone is no longer enough to keep critical accounts safe. Attackers can steal credentials through phishing, password spraying, and data breaches, then use them to move directly into protected systems.
The numbers make the risk clear. Microsoft research found that MFA reduced account compromise risk by 99.22% across its study population.
But MFA is not automatically foolproof. Attackers increasingly target weak authentication methods, users, sessions, and recovery processes. The FIDO Alliance also reports that 36% of surveyed consumers had experienced an account compromise caused by weak or stolen passwords.
This guide explains what MFA is, how it works, its authentication factors and methods, why it matters, common MFA bypass techniques, and the best practices for implementing it. It also explores how ZeroThreat helps security teams test and validate MFA applications through AI-powered automated pentesting.
See exactly where your login and MFA setup can be exploited before hackers do. Test My App Free
Table of Contents
- TL;DR: Key Takeaways on Multi-Factor Authentication
- What is Multi-Factor Authentication (MFA)?
- What are the Different Factors of Authentication?
- How Does Multi-Factor Authentication Work?
- MFA vs. 2FA vs. SSO: What's the Difference?
- Common Multi-Factor Authentication Methods
- Why is Multi-Factor Authentication Important?
- 7 MFA Bypass Attack Techniques Used by Hackers
- Best Practices for Implementing Multi-Factor Authentication
- ZeroThreat for Scanning Application with Multi-Factor Authentication
- Wrapping Up
TL;DR: Key Takeaways on Multi-Factor Authentication
- MFA requires two or more independent factors to verify identity, making it far stronger than a password alone.
- Authentication factors fall into five categories: knowledge, possession, inherence, location, and behavior.
- MFA works by challenging users with a second verification step after their initial login credentials pass.
- MFA differs from 2FA and SSO. 2FA is a fixed two-step form of MFA, while SSO reduces login friction rather than strengthening verification.
- MFA blocks the vast majority of automated account takeover attempts, making it a baseline security control.
- Compliance frameworks like GDPR, PCI DSS, HIPAA, and ISO 27001 increasingly require or recommend MFA.
- MFA is not unbreakable. Attackers use techniques like push bombing, AiTM phishing, and SIM swapping to bypass it.
- Phishing-resistant methods like FIDO2 security keys and passkeys offer the strongest protection against modern bypass techniques.
- Best practices include avoiding SMS-only verification, securing account recovery, and monitoring authentication activity continuously.
- Automated testing tools like ZeroThreat validate that MFA-protected applications hold up under real authentication and authorization testing.
What is Multi-Factor Authentication (MFA)?
Multi-Factor Authentication (MFA) is a security mechanism that requires users to provide multiple forms of verification before accessing an account, application, system, or sensitive resource.
Unlike password-only authentication, MFA adds additional verification steps to reduce the risk of unauthorized access. Even if an attacker obtains a user's password, they may still be unable to complete the authentication process.
MFA is widely used to strengthen identity and access management across cloud applications, enterprise systems, VPNs, email accounts, and other digital services. It provides an additional security layer around user accounts.
Modern MFA can also support stronger authentication methods designed to resist phishing and credential theft. When implemented correctly, it significantly reduces the impact of compromised credentials and helps prevent account takeover.
What are the Different Factors of Authentication?
Authentication factors are the types of evidence a user can provide to verify their identity. MFA can combine different factors to strengthen access control and reduce the risk of unauthorized account access.
Knowledge
Something You Know: PIN, Password, or Security Question
The knowledge factor uses information that only the user should know to verify their identity. Common examples include passwords, PINs, passphrases, and security question answers. This factor is simple to implement, but credentials can be exposed through phishing, credential stuffing, brute-force attacks, or social engineering.
Possession
Something You Have: OTP, Token, Trusted Device, Smart Card or Badge, or Device-Bound Passkey
The possession factor verifies something the user has access to, such as a registered smartphone, hardware token, smart card, badge, or trusted device. One-time passwords (OTPs), authentication tokens, and device-bound passkeys can provide stronger protection against stolen credentials and unauthorized access.
Inherence
Something You Are: Fingerprint, Facial Recognition, Iris Scan, or Voice Recognition
The inherence factor verifies a user's identity through unique biological characteristics. Common methods include fingerprint scanning, facial recognition, iris scanning, and voice recognition. Because these characteristics are difficult to replicate, biometric authentication can strengthen identity verification when supported by secure sensors and anti-spoofing controls.
Location
Somewhere You Are: GPS Location, IP Address, Trusted Network, or Geolocation
The location factor considers where an authentication request originates to assess whether access is expected. Systems may evaluate GPS location, IP address, network information, or geolocation data. This factor can support risk-based authentication by identifying login attempts from unusual or unexpected geographic locations.
Behavioral
Something You Do: Typing Pattern, Mouse Movement, Device Usage, or User Behavior
The behavioral factor analyzes how a user normally interacts with an application or device. Typing patterns, mouse movements, navigation habits, device usage, and other behavioral signals can help identify anomalies. Organizations can use these signals for continuous authentication and adaptive access control.
Don't assume your login is secure. Let automated pentesting prove it against real attack techniques. Prove My Security
How Does Multi-Factor Authentication Work?
Multi-Factor Authentication (MFA) works by requiring users to complete multiple identity verification steps before access is granted. Each step adds another security layer beyond the initial login credentials.
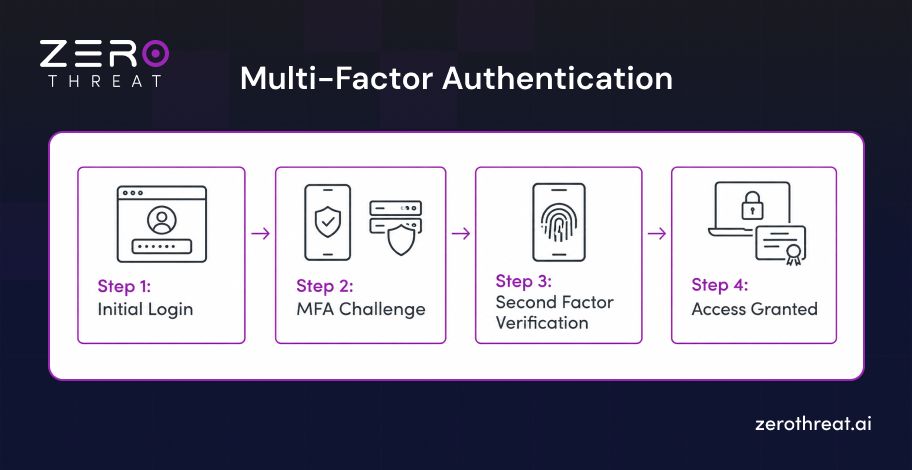
Step 1: Initial Login
The user begins by entering their primary login credentials, such as a username and password. The authentication system verifies these credentials against the account information. If they are valid, the system initiates the configured MFA challenge instead of immediately granting access.
Step 2: MFA Challenge
After the initial credentials are accepted, the authentication system requests an additional verification step. Depending on the MFA method, this may involve entering an OTP, approving a push notification, using a security key, or providing biometric verification.
Step 3: Second Factor Verification
The user completes the requested MFA challenge using their registered authenticator or device. The authentication service verifies the submitted response and confirms that the required authenticator is under the user's control. Secure authentication protocols help protect this exchange from interception and replay attacks.
Step 4: Access Granted
If the additional verification succeeds, the identity provider or authentication service considers the authentication successful and grants access to the requested application or resource. If verification fails, access is denied or another authentication attempt may be required.
MFA vs. 2FA vs. SSO: What's the Difference?
MFA and 2FA strengthen authentication by requiring multiple verification factors, while SSO simplifies access by letting users authenticate once and access multiple applications. Although these technologies can work together, they address different identity and access management requirements.
| Aspect | MFA | 2FA | SSO |
|---|---|---|---|
| Meaning | Multi-Factor Authentication | Two-Factor Authentication | Single Sign-On |
| Primary Purpose | Strengthen account security | Add a second authentication factor | Simplify access to multiple applications |
| Authentication | Uses two or more distinct factors | Uses exactly two distinct factors | Uses one authentication process for multiple applications |
| Example | Password + security key + biometric | Password + OTP | One corporate login to access email, CRM, and other applications |
| Security Focus | Stronger identity verification | Protection beyond password-only login | Centralized identity and access management |
| Relationship | 2FA is a subset of MFA | A specific, minimum form of MFA | Often paired with MFA to secure the single login point |
Common Multi-Factor Authentication Methods
The digital space features various methods for multi-factor authentication. Here are some of the most commonly used approaches.
1. SMS or Email Codes
How it Works: Once the user enters the password, the user will receive a one-time code via SMS or email. Then, he must enter this code to complete the login process.
Example: Logging into a net banking application and receiving a text message with a verification code.
2. Authentication Apps
How it Works: An application creates a time-based one-time password (TOTP) or a code that refreshes within several seconds. You enter this code after your password.
Example: Use Google Authenticator or Microsoft Authenticator to get a code to log into your email.
3. Hardware Tokens
How it Works: A physical device creates a one-time passcode (OTP) or uses USB/NFC for verification. Once the password is entered, the user can use the hardware token to provide the second factor.
Example: Using a YubiKey USB device or a key fob that presents a rotating OTP.
4. Smartcards
How it Works: A physical card is inserted into a card reader or scanned to authenticate. This is often combined with a PIN.
Example: Use of a government-issued smartcard to access secure systems.
5. Biometric Authentication
How it Works: The system uses physical characteristics unique to the user to authenticate identity. This can be done before or after entering a password.
Example: Users can unlock a smartphone or log into a system by placing their finger on a fingerprint scanner.
6. Voice Identification
How it Works: The voice detection system validates the user's identity on the basis of their voice. This is used in combination with other authentication factors.
Example: Voice authentication for net banking services or secure voice recognition systems.
7. Email Links
How it Works: Once the user enters their password, an email with a link will be sent to confirm their login attempt. Users have to click the link to complete the verification process.
Example: Confirming users' login attempts by clicking a link sent to their email address.
Get authenticated security testing that fits your team, without the cost of manual pentests. Check Out Pricing
Why is Multi-Factor Authentication Important?
Multi-Factor Authentication is important because it adds additional identity verification beyond passwords. It helps organizations protect accounts, reduce unauthorized access, limit credential-based attacks, and strengthen overall identity and access management.
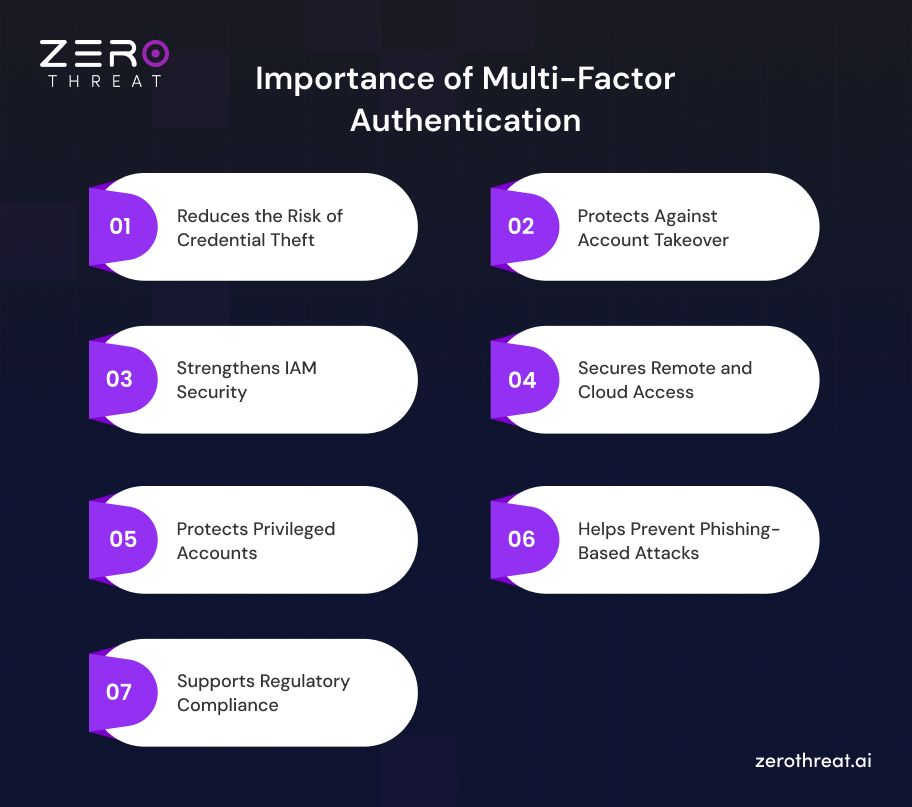
Reduces the Risk of Credential Theft
Passwords can be exposed through phishing, credential stuffing, data breaches, and social engineering attacks. MFA adds another verification requirement, making a stolen password alone insufficient for accessing a protected account or application.
Protects Against Account Takeover
Account takeover attacks often begin with compromised login credentials. MFA adds an additional security layer that can prevent attackers from accessing accounts even when they obtain valid usernames and passwords.
Strengthens IAM Security
MFA strengthens identity and access management by requiring additional proof of user identity before granting access. Organizations can apply MFA to employees, administrators, customers, and other users based on their access privileges and security requirements.
Secures Remote and Cloud Access
Remote work and cloud applications allow users to access business resources from different devices and locations. MFA helps verify legitimate users before granting access to cloud services, VPNs, enterprise applications, and other remote resources.
Protects Privileged Accounts
Privileged accounts have elevated permissions and can provide access to sensitive systems and data. Enforcing MFA for administrators and other high-privilege users reduces the likelihood that compromised credentials can be used to gain unauthorized administrative access.
Helps Prevent Phishing-Based Attacks
MFA can reduce the impact of stolen credentials obtained through phishing. However, not every MFA method provides the same level of protection. Phishing-resistant methods such as FIDO2 security keys and passkeys offer stronger protection against credential interception.
Supports Regulatory Compliance
Many security frameworks, regulations, and organizational policies recommend or require stronger authentication for sensitive systems and data. Implementing MFA can help organizations meet authentication and access control requirements while improving their overall security posture.
7 MFA Bypass Attack Techniques Used by Hackers
MFA bypass attacks target weaknesses in authentication workflows rather than simply breaking MFA itself. Attackers may exploit user behavior, communication protocols, stolen sessions, third-party authorization, or recovery processes to gain unauthorized account access.
MFA Fatigue (Push Bombing)
In an MFA fatigue attack, attackers repeatedly send authentication push notifications to a targeted user after obtaining valid credentials. The goal is to overwhelm or confuse the user into approving a fraudulent request, allowing the attacker to complete the login process.
Adversary-in-the-Middle Phishing
Adversary-in-the-Middle (AiTM) phishing attacks place an attacker between the victim and legitimate authentication service. A phishing proxy can capture credentials and session information during authentication, potentially allowing attackers to steal an authenticated session even when MFA is successfully completed.
SIM Swapping Attacks
SIM swapping occurs when an attacker convinces a mobile carrier to transfer a victim's phone number to a SIM card under the attacker's control. If SMS is used for MFA, the attacker may receive verification codes and use them to access protected accounts.
SS7 Protocol Exploits
SS7 protocol vulnerabilities can be abused to intercept or redirect SMS messages and calls associated with mobile authentication. Attackers who exploit weaknesses in telecommunications signaling may obtain SMS-based MFA codes, making SMS authentication less suitable for protecting high-value or sensitive accounts.
Session Token Hijacking
Session token hijacking involves stealing an authenticated session token or cookie after the user completes MFA. An attacker can potentially reuse the valid session to access an application without repeating the authentication process, particularly when session management or token protection is weak.
OAuth Account Takeover
Attackers can abuse compromised OAuth credentials, malicious applications, or improperly configured authorization flows to gain access to connected accounts and resources. If an attacker obtains valid OAuth tokens, they may access authorized services without triggering the normal MFA process again.
Helpdesk Social Engineering
Attackers may impersonate legitimate users and manipulate helpdesk personnel into resetting MFA settings, registering a new authenticator, or disabling authentication controls. Weak identity verification during account recovery can therefore create an alternative path around otherwise strong MFA protections.
Best Practices for Implementing Multi-Factor Authentication
Effective MFA implementation requires more than simply adding another login step. Organizations should choose secure authentication methods, protect high-risk accounts, strengthen recovery processes, and continuously monitor authentication activity.
Use Phishing-Resistant MFA
Choose authentication methods designed to resist phishing and credential interception. FIDO2 security keys, WebAuthn authenticators, and device-bound passkeys provide stronger protection than methods that rely on codes or approval prompts that attackers can potentially manipulate.
Protect Privileged Accounts
Enforce MFA for administrator accounts, developers, security teams, and other users with elevated privileges. Protecting privileged identities reduces the risk of attackers using compromised credentials to access critical systems, modify configurations, or reach sensitive organizational data.
Avoid SMS-Based MFA
Avoid relying on SMS as the primary MFA method when stronger options are available. SMS codes can be targeted through SIM swapping, social engineering, and interception. Prefer authenticator apps, hardware security keys, or phishing-resistant passkeys for sensitive accounts.
Enforce Adaptive Authentication
Use adaptive or risk-based authentication to evaluate signals such as device, location, IP address, and unusual login behavior. Organizations can require stronger verification when authentication attempts appear risky while reducing unnecessary friction for trusted access.
Secure Account Recovery
Treat account recovery as part of the authentication security model. Weak recovery processes can allow attackers to bypass MFA. Require strong identity verification, protect recovery codes, restrict recovery channels, and monitor account recovery attempts for suspicious activity.
Maintain Backup Methods
Provide secure backup authentication methods for users who lose access to their primary authenticator. Recovery codes, secondary hardware security keys, or approved backup authenticators can prevent lockouts without creating weak authentication paths that attackers could exploit.
Monitor Authentication Activity
Continuously monitor authentication events, failed MFA attempts, unusual login patterns, and repeated push requests. Centralized logging and security monitoring can help security teams detect MFA fatigue attacks, suspicious account activity, and potential attempts to bypass authentication controls.
ZeroThreat for Scanning Application with Multi-Factor Authentication
Testing an MFA-protected application is not the same as testing a standard login. Scanners need to authenticate through the extra verification step before they can reach the pages and workflows behind it.
ZeroThreat supports authenticated scanning behind MFA-protected login pages. Its AI Recorder extension captures the full login flow, including MFA steps, so scans can move past authentication and test the application journey as a real logged-in user.
Beyond getting past the login screen, ZeroThreat validates what happens after. It checks authorization rules, role permissions, and session behavior, surfacing issues like broken access control or session handling flaws that MFA alone cannot prevent.
Findings are backed by proof-of-exploit evidence with near-zero false positives, so security teams spend less time chasing noise. This helps validate that authentication and authorization controls hold up under real testing conditions, not just in theory.
Not sure where your authentication risks lie? Talk to our team and find out. Connect With Us
Wrapping Up
Strong authentication is no longer optional. Passwords alone cannot withstand today's threat landscape, and layering identity verification through multiple factors remains one of the most effective defenses available to individuals and organizations alike.
Still, no control is foolproof. Attackers have adapted their tactics, targeting sessions, help desks, and trust relationships rather than the factors themselves, which means strong authentication design and vigilance must go hand in hand.
Validating that these defenses actually hold up matters just as much as deploying them. Using ZeroThreat's web app penetration testing tool, you can test authenticated workflows and authorization behavior directly, helping your team confirm that the protections work as intended.
Building resilient authentication is an ongoing effort, not a one-time setup. Choosing the right factors, following proven practices, and validating them regularly gives organizations a real, lasting advantage against evolving identity-based threats.
Frequently Asked Questions
Is MFA the same as 2FA?
No, MFA (Multi Factor Authentication) and 2FA (Two-Factor Authentication) are not exactly the same. 2FA is a subset of MFA. At the same time, two-factor authentication involves exactly two different authentication factors (something you know and something you have, for example). Multi factor authentication can involve two or more other factors for stronger security.
What are the key multi factor authentication challenges?
What is FIDO2?
What is phishing-resistant MFA?
Does MFA prevent account takeover?
Why is implementing MFA better than changing the password frequently?
What is the strongest MFA method?
What are the pros and cons of MFA?
Related Articles

Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.