 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs
Quick Overview: Cybersecurity risk assessment turns scattered vulnerabilities into a clear, prioritized view of business risk. This blog explains the difference between risk and vulnerability assessment, breaks down key components and methodologies, and walks through a practical 9-step process covering scope, asset identification, threat mapping, likelihood and impact scoring, and continuous reassessment.
A vulnerability can be more than a technical finding. When it affects a critical application, exposed API, or sensitive data, it can become a serious business risk.
The 2026 Verizon DBIR found that vulnerability exploitation accounted for 31% of breaches, making it the leading initial access vector. IBM’s 2026 report also puts the global average cost of a data breach at $4.99 million.
This is why cybersecurity risk assessment matters. It helps organizations understand which assets are exposed, which threats are relevant, how likely an attack is, and what the potential business impact could be.
In this guide, you will learn how to perform a cybersecurity risk assessment in nine practical steps, calculate and prioritize risk, evaluate security controls, and continuously reassess your organization’s changing risk exposure.
Ready to prioritize real security risks over noise? Create your free account today. Claim Free Access
On This Page
- TL;DR: Cybersecurity Risk Assessment Checklist
- What is a Cybersecurity Risk Assessment?
- Why is Cybersecurity Risk Assessment Important?
- Cybersecurity Risk Assessment vs Vulnerability Assessment
- Key Components of a Cybersecurity Risk Assessment
- Core Cybersecurity Risk Assessment Methodologies
- How to Perform a Cybersecurity Risk Assessment in 9 Steps
- Summing Up
TL;DR: Cybersecurity Risk Assessment Checklist
- Define the assessment scope, objectives, stakeholders, systems, and business processes.
- Identify and classify critical assets based on business value and data sensitivity.
- Identify relevant threats, threat actors, and realistic attack scenarios.
- Discover vulnerabilities and security gaps using testing, audits, and configuration reviews.
- Evaluate existing security controls and their effectiveness in reducing risk.
- Determine the likelihood of each risk event using a consistent scoring scale.
- Assess potential financial, operational, regulatory, customer, and reputational impact.
- Calculate risk using Risk Score = Likelihood × Impact and prioritize accordingly.
- Assign risk owners and select appropriate treatment: mitigate, avoid, transfer, or accept.
- Continuously monitor changes, validate remediation, and reassess risk as the attack surface evolves.
What is a Cybersecurity Risk Assessment?
A cybersecurity risk assessment is a structured process for identifying, analyzing, and prioritizing risks that could affect an organization’s systems, data, applications, and business operations. It helps security teams understand where exposure matters most.
The assessment considers critical assets, potential threats, existing vulnerabilities, security controls, likelihood, and business impact. By evaluating these factors together, organizations can determine which risks require immediate attention, and which can be monitored or accepted.
A risk assessment goes beyond finding technical weaknesses. A vulnerability may have high severity but pose limited business risk if the affected system has strong controls or limited exposure. Risk assessment adds business context to security findings.
The outcome is a prioritized view of cybersecurity risk that supports informed decisions. Security teams can use it to allocate resources, strengthen controls, reduce potential losses, meet compliance requirements, and continuously manage changing risks across the attack surface.
Why is Cybersecurity Risk Assessment Important?
A cybersecurity risk assessment helps organizations identify their most important security risks, prioritize remediation, strengthen controls, protect critical assets, and make informed decisions based on business impact and risk exposure.
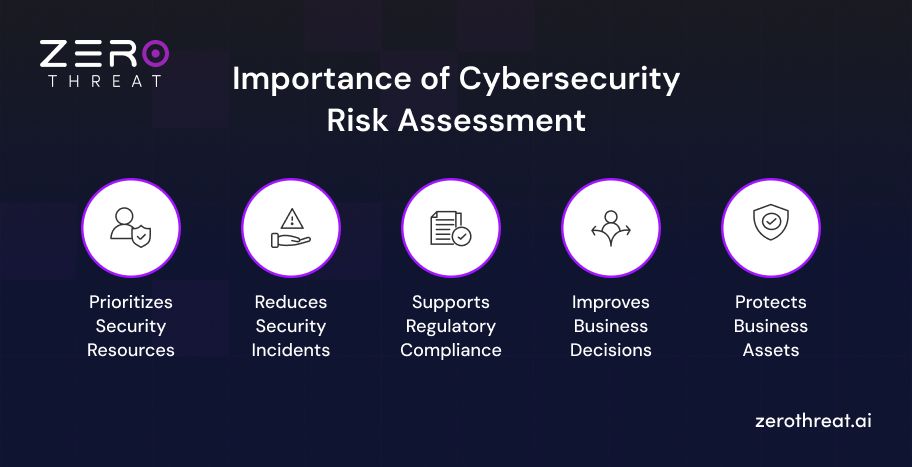
Prioritizes Security Resources
Not every security weakness creates the same level of business risk. Risk assessment helps security teams prioritize vulnerabilities and threats based on likelihood, impact, asset criticality, and existing controls. This allows organizations to direct security resources toward risks that could cause the greatest operational or financial damage.
Reduces Security Incidents
Identifying cybersecurity risks early gives organizations an opportunity to address weaknesses before attackers can exploit them. Risk assessments reveal gaps in security controls, access management, monitoring, and system configurations, helping teams implement preventive measures that reduce the likelihood and potential impact of security incidents.
Supports Regulatory Compliance
Many security and privacy frameworks require organizations to identify, evaluate, and manage information security risks. A structured risk assessment can support compliance with requirements and controls associated with ISO 27001, NIST, PCI DSS, HIPAA, and GDPR while providing evidence of a risk-based security approach.
Improves Business Decision-Making
Cybersecurity risk assessment connects technical security findings with business consequences. Security leaders can use risk scores, financial exposure, operational impact, and compliance considerations to justify security investments, allocate budgets, prioritize remediation, and make informed decisions about risk treatment and acceptable risk levels.
Protects Critical Business Assets
Risk assessments help organizations identify and protect assets that are essential to business operations. These may include web applications, APIs, cloud infrastructure, customer data, intellectual property, credentials, and internal systems. Understanding their risk exposure helps teams strengthen controls around the assets that matter most.
Confirmed exploits, not scan noise. Discover how automated pentesting sharpens your risk assessment. Automate Your Pentest
Cybersecurity Risk Assessment vs Vulnerability Assessment
Cybersecurity risk assessment and vulnerability assessment serve different purposes within a security program. A vulnerability assessment identifies weaknesses in systems, applications, and infrastructure, while a risk assessment evaluates the likelihood and business impact of those weaknesses and other potential threats.
| Factor | Cybersecurity Risk Assessment | Vulnerability Assessment |
|---|---|---|
| Primary Objective | Understand and prioritize overall cybersecurity risk | Identify security weaknesses |
| Focus | Assets, threats, vulnerabilities, likelihood, impact, and controls | Vulnerabilities, misconfigurations, and security flaws |
| Business Context | Directly considers financial, operational, regulatory, and reputational impact | Usually focuses on technical severity |
| Prioritization | Prioritizes risks based on likelihood and business impact | Prioritizes findings based mainly on vulnerability severity |
| Typical Question | “What security risks could have the greatest impact on our business?” | “What vulnerabilities exist in our systems?” |
| Common Output | Risk scores, risk levels, treatment plans, and risk register | Vulnerability findings, severity ratings, and remediation recommendations |
Key Components of a Cybersecurity Risk Assessment
A cybersecurity risk assessment combines asset, threat, vulnerability, and control analysis to determine risk exposure. These components help organizations evaluate potential threats, prioritize risks, and define appropriate risk treatment actions.
Scope and Objectives
Defining the scope establishes what the assessment will cover, such as applications, APIs, cloud environments, networks, data, or business units. Clear objectives also identify the assessment goals, stakeholders, assumptions, and constraints, ensuring the cybersecurity risk assessment remains focused and aligned with business requirements.
Asset Identification
Asset identification involves discovering and classifying systems, applications, APIs, databases, cloud resources, sensitive information, and other business-critical assets. Security teams assess each asset based on its business value, data sensitivity, operational importance, and exposure to determine which assets require greater protection.
Threat Identification
Threat identification focuses on events and threat actors that could compromise organizational assets. These may include ransomware, phishing, malware, insider threats, account takeover, API abuse, supply-chain attacks, and data breaches. Understanding relevant threats provides context for evaluating potential attack scenarios and risk exposure.
Vulnerability Analysis
Vulnerability analysis identifies weaknesses that could be exploited by threats. Organizations can use vulnerability scanning, penetration testing, DAST, configuration reviews, security audits, and threat intelligence to identify weaknesses. The assessment should consider exploitability, exposure, affected assets, and existing controls rather than relying only on severity ratings.
Risk Analysis and Scoring
Risk analysis evaluates the likelihood and potential impact of identified risk events. Organizations may use qualitative or quantitative methods to assign risk scores based on factors such as exploitability, asset criticality, financial impact, operational disruption, and regulatory exposure. This supports consistent risk prioritization.
Mitigation and Reporting
Mitigation involves selecting appropriate risk treatment actions, such as reducing, transferring, avoiding, or accepting risk. Assessment results should be documented through risk reports and risk registers that identify findings, risk levels, owners, remediation actions, and timelines for tracking and continuous risk management.
Core Cybersecurity Risk Assessment Methodologies
Cybersecurity risk assessment methodologies provide structured approaches for identifying, analyzing, and prioritizing security risks. Organizations typically use qualitative, quantitative, or semi-quantitative methods based on their risk management objectives.
Qualitative Risk Assessment
Qualitative risk assessment evaluates cybersecurity risks using descriptive categories such as Low, Medium, High, and Critical. Security teams assess factors including threat likelihood, asset criticality, vulnerability exposure, and potential business impact.
This approach is useful when precise financial or probability data is unavailable. It provides a practical way to prioritize risks, communicate security concerns to stakeholders, and determine appropriate risk treatment without complex calculations.
Quantitative Risk Assessment
Quantitative risk assessment assigns numerical values to cybersecurity risks and estimates their potential financial impact. Organizations may use probability, expected loss, asset value, and historical data to calculate measurable risk exposure.
This methodology supports financial decision-making by translating security risks into monetary terms. It can help security leaders compare potential losses with the cost of security controls and justify investments based on expected risk reduction.
Semi-Quantitative Assessment
Semi-quantitative risk assessment combines the simplicity of qualitative analysis with numerical scoring. Security teams typically assign values such as 1 to 5 to factors including likelihood and business impact.
The scores can then be multiplied or combined to calculate an overall risk rating. This approach provides more consistency than purely descriptive assessments while remaining easier to implement than detailed quantitative risk analysis.
Find the right plan to match your risk assessment and testing needs today. Check Out Pricing
How to Perform a Cybersecurity Risk Assessment in 9 Steps
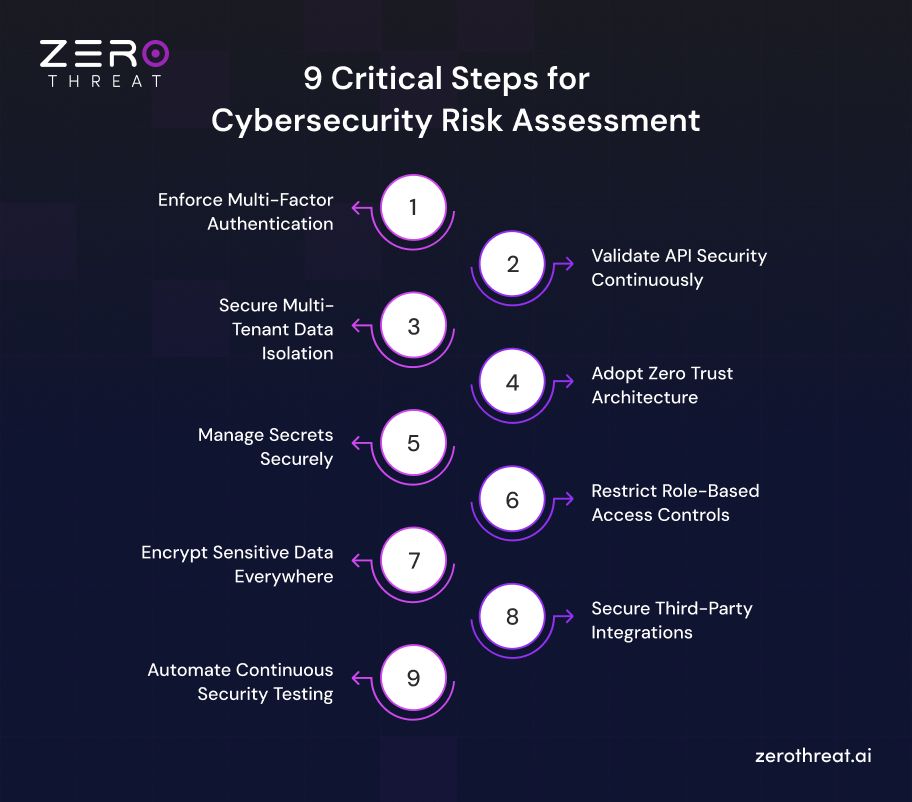
A cybersecurity risk assessment follows a structured process to identify assets, threats, vulnerabilities, security controls, likelihood, and business impact. These steps help organizations prioritize risks and make informed security decisions.
Step 1: Define the Scope and Context
Start by defining what the assessment needs to cover and what decisions it should support. Identify the relevant applications, APIs, cloud environments, networks, data, business processes, and organizational units.
Also document key stakeholders, objectives, assumptions, constraints, regulatory requirements, and the assessment timeframe. A clearly defined scope helps prevent blind spots and keeps the assessment aligned with business priorities.
Step 2: Identify Your Critical Assets
Create an inventory of assets that support critical business functions. Include web applications, APIs, databases, cloud infrastructure, endpoints, sensitive data, intellectual property, and third-party services.
Classify each asset according to factors such as:
- Business criticality
- Data sensitivity
- Operational importance
- Internet exposure
This classification helps security teams focus risk analysis on assets where a security incident could have significant business consequences.
Step 3: Identify Potential Threats
Identify threat sources and events that could affect the assets within scope. Consider ransomware, phishing, account takeover, DDoS, API abuse, insider threats, malware, and supply-chain attacks.
Use threat intelligence, previous incidents, industry-specific threats, and the organization’s exposure to develop realistic attack scenarios. NIST recommends considering relevant threat sources and threat events when determining cybersecurity risk.
Step 4: Identify Vulnerabilities and Security Gaps
Identify weaknesses that could allow a threat event to compromise an asset. Use vulnerability assessments, DAST, penetration testing, configuration reviews, security audits, code analysis, and threat intelligence as inputs.
Look beyond vulnerability severity. Consider exploitability, asset exposure, affected business functions, and existing security controls. A critical vulnerability does not automatically represent the highest business risk without this context.
Step 5: Evaluate Existing Security Controls
Review the controls already protecting each asset and determine how effectively they reduce risk. Assess authentication, authorization, MFA, encryption, network security, endpoint protection, logging, monitoring, patch management, and incident response capabilities.
For each control, determine whether it reduces the likelihood of successful exploitation, limits potential impact, or improves detection and response. This helps establish the organization’s remaining or residual risk.
Step 6: Determine the Likelihood of Exploitation
Assess how likely each identified threat event is to exploit a vulnerability or compromise an asset. Consider factors such as threat actor capability, attack complexity, internet exposure, exploit availability, vulnerability severity, and effectiveness of existing controls.
A simple 1 to 5 scale can help maintain consistency:
| Score | Likelihood | Description |
|---|---|---|
| 1 | Rare | Exploitation requires significant resources and is unlikely |
| 2 | Unlikely | Exploitation is possible but uncommon |
| 3 | Possible | Exploitation could occur under the right conditions |
| 4 | Likely | Exploitation is expected given known exposure |
| 5 | Almost Certain | Active exploitation is already occurring in the wild |
Step 7: Determine the Business Impact
Evaluate the consequences if the risk event occurs. Consider financial losses, operational disruption, data exposure, regulatory penalties, customer impact, and reputational damage. The impact assessment should reflect the importance of the affected asset and business process.
| Score | Impact | Description |
|---|---|---|
| 1 | Minimal | Negligible disruption, no data or financial loss |
| 2 | Minor | Limited disruption, low financial impact |
| 3 | Moderate | Noticeable disruption, moderate financial and reputational impact |
| 4 | Major | Significant disruption, substantial financial and regulatory impact |
| 5 | Severe | Critical disruption, major financial, legal, and reputational damage |
Step 8: Calculate and Prioritize Risk
Combine likelihood and impact to determine the overall risk level. A commonly used scoring approach is:
Risk Score = Likelihood × Impact
For example, a likelihood score of 4 and an impact score of 5 produces a risk score of 20, indicating a high-priority risk under a typical 1 to 5 model. Compare the results with the organization’s risk appetite and treatment thresholds.
Step 9: Treat, Monitor, and Reassess Risk
Select an appropriate risk treatment based on its severity, business context, and risk tolerance. Organizations can mitigate, avoid, transfer, or accept risks. Assign an owner, define remediation actions, and establish timelines for tracking progress.
Risk assessment should continue as the environment changes. New vulnerabilities, application releases, APIs, infrastructure changes, security incidents, and major business changes can alter risk exposure. NIST recommends continuous monitoring to maintain awareness of threats, vulnerabilities, and control effectiveness.
Not sure where to start? Let's map out your risk assessment approach together. Connect With Us
Summing Up
Cybersecurity risk assessment is not a one-time checklist. It's a continuous practice of identifying assets, weighing threats against real business impact, and prioritizing what actually deserves attention first.
The organizations that manage risk well are the ones that treat likelihood and impact as connected, not separate exercises. Scoring, documenting, and reassessing regularly keeps that connection accurate as systems evolve.
Manual assessments alone can't keep pace with how fast modern applications change. ZeroThreat helps close that gap with continuous, validated testing across web apps and APIs, so your risk data stays current, not just accurate on the day you ran it.
Frequently Asked Questions
How often should cybersecurity risk assessment be performed?
Cybersecurity risk assessments should be performed at least annually and whenever significant changes affect the organization’s risk exposure. Reassess after major application releases, new APIs, infrastructure changes, security incidents, or critical vulnerabilities. Continuous monitoring can also help identify when an assessment needs to be updated.
What are the key challenges while performing cybersecurity risk assessment?
What is a cybersecurity risk register?
What is the difference between inherent and residual risk?
Which frameworks are used for cybersecurity risk assessment?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.