 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs

Quick Overview: Security can't wait until testing or deployment. This guide breaks down Secure SDLC from the ground up: what it means, how it differs from DevSecOps, and why it matters. You'll find the seven lifecycle phases, security activities mapped to each stage, an implementation roadmap, and best practices to ensure security right into SLCD.
In a typical software development lifecycle, security testing is considered an afterthought as it is performed at the end. However, with the rising frequency and sophistication of cyberattacks, this approach fails to produce secure software applications.
Therefore, organizations must redefine their approach to build quality and secure software applications. They need secure SDLC to win the battle against evolving cyber threats and build risk-free applications. It is an extension of an SDLC, with security becoming a key component.
But what is secure SDLC and how does it help in developing more risk-resistant applications? Let’s learn about secure SDLC in detail, how you can implement it easily with automated penetration testing solution, and best practices you can follow.
Put your secure SDLC into action with automated security testing built for modern applications. Start Free Testing
Table of Contents
- What is Secure SDLC (SSDLC)?
- Secure SDLC vs DevSecOps: What's the Difference?
- Why is Secure SDLC Important?
- What are the Different Phases of Secure SDLC?
- Security Activities by SDLC Phase
- How to Implement a Secure SDLC
- Best Practices to Follow for a Secure SDLC
- Summing Up
What is Secure SDLC (SSDLC)?
Secure SDLC (SSDLC) is a software development approach that integrates security into every stage of the Software Development Life Cycle. It brings security requirements, risk assessment, secure design, coding, testing, deployment, and monitoring into the development process.
Unlike traditional SDLC models where security may be addressed near the end, SSDLC introduces security considerations early. Teams can identify vulnerabilities, design weaknesses, compliance requirements, and potential attack paths before they become expensive to fix.
A secure SDLC typically includes activities such as threat modeling, secure coding, code review, SAST, software composition analysis (SCA), API security testing, DAST, penetration testing, and security monitoring. The specific controls depend on the application's risk and architecture.
The goal is not to make an application completely risk-free. Instead, SSDLC helps teams identify and manage security risks throughout development, reduce security debt, improve release confidence, and build more resilient software from the start.
Secure SDLC vs DevSecOps: What's the Difference?
| Aspect | Secure SDLC | DevSecOps |
|---|---|---|
| Primary Focus | Integrates security across the software development lifecycle. | Integrates security into development, operations, and delivery workflows. |
| Approach | Lifecycle and security process-oriented. | Culture, collaboration, and automation-oriented. |
| Scope | Covers planning, requirements, design, development, testing, deployment, and operations. | Focuses on continuous security across CI/CD, development, deployment, and operations. |
| Security Activities | Threat modeling, secure coding, security testing, risk assessment, and security reviews. | Automated security testing, continuous monitoring, security gates, and security feedback loops. |
| Automation | Can include automation, but it is not its defining characteristic. | Relies heavily on automation and integration within DevOps pipelines. |
| Team Responsibility | Security responsibilities are integrated into each SDLC phase. | Security becomes a shared responsibility across development, security, and operations teams. |
| Key Goal | Build security into the software lifecycle from the beginning. | Make security a continuous and collaborative part of fast software delivery. |
Why is Secure SDLC Important?
Modern users are more concerned about their data privacy and security. Hence, organizations must ensure stringent security measures to protect their data. SSDLC can help mitigate the risks by involving security testing early in the development process. The following are the key advantages of this process.
Building Secure Applications
Until now, organizations have followed a systematic approach to developing, testing, and releasing software applications. Often, testing was shifted further, even after the launch of applications. Consequently, they met with unwarranted bugs that resulted in security flaws.
So, this isn’t an efficient approach from a security point of view. A possible solution to the problem of unwarranted security loopholes is security testing with each development step or every code commit to ensure the final product is secure.
Reduced Costs
Fixing vulnerabilities in a software application takes a lot of time and resources. It can be even more challenging if vulnerabilities have been found after an application is released in production. Hence, early detection of vulnerabilities can reduce the costs of fixing them.
When you catch vulnerabilities as early as possible, it reduces the potential timeframe and the number of resources needed to fix them. The following graph from IBM’s research shows the relative cost of fixing security defects as an application moves through the development cycle.

Compliance Requirements
A secure software development process not only helps in creating secure software applications but also allows organizations to adhere to regulatory compliances. Regulations and compliances dictate organizations to follow specific practices for development.
Ensure User Trust
Today, users are highly concerned about their data security and privacy. The rising incidents of cybercrimes add to their fears. However, organizations can follow secure SDLC best practices to gain their trust by providing applications that protect their data. Secure SDLC ensures that applications are free of bugs or loopholes that could lead to successful cyberattacks.
Threat modeling tells you what could go wrong. Automated pentesting proves what actually will. Test Your Attack Surface
What are the Different Phases of Secure SDLC?
Secure SDLC integrates security activities throughout the software development lifecycle, from defining requirements and designing architecture to testing, deployment, monitoring, and continuous improvement.
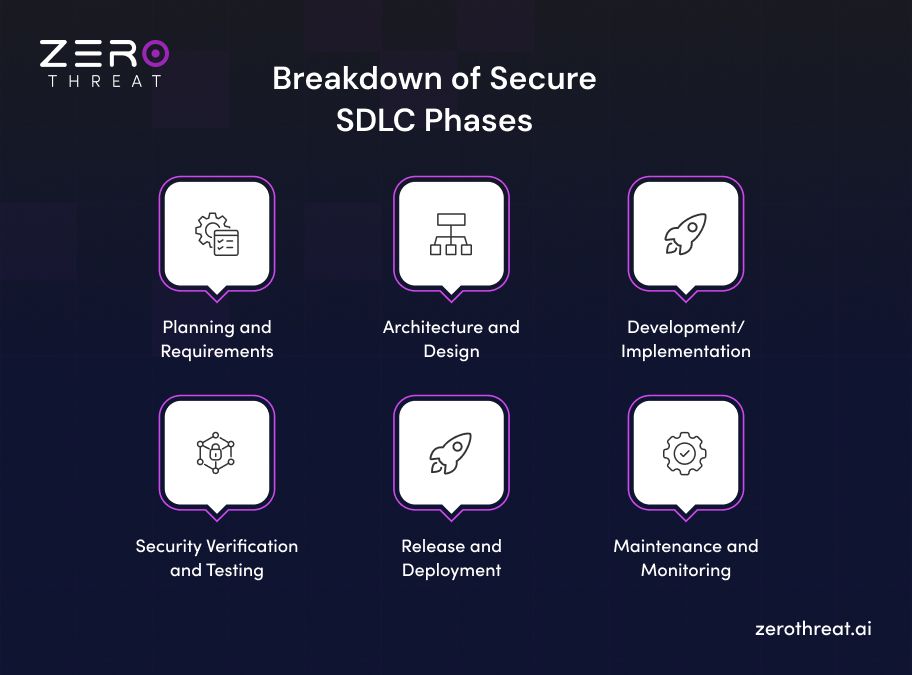
1. Planning and Requirements
This phase defines security requirements alongside functional requirements. Teams assess risks, classify sensitive data, identify regulatory obligations, define security acceptance criteria, and document abuse cases. These inputs establish the security expectations that the application must meet throughout development.
2. Architecture and Design
Security is incorporated into the application's architecture before implementation begins. Teams perform threat modeling, analyze attack surfaces and trust boundaries, and design controls for authentication, authorization, encryption, privacy, and secure data flows. This helps address architectural weaknesses before they reach production.
3. Development/Implementation
Developers apply secure coding standards and security controls while building the application. Common activities include peer code review, SAST, software composition analysis (SCA), secrets detection, dependency checks, and secure developer training. These practices help identify weaknesses directly within development workflows.
4. Security Verification and Testing
Security testing validates whether implemented controls work as expected and identifies vulnerabilities that remain after development. Depending on risk, teams may use SAST, DAST, API security testing, SCA, fuzz testing, manual testing, and penetration testing.
5. Release and Deployment
Before release, teams evaluate whether the application meets defined security requirements and release criteria. CI/CD security gates, artifact integrity checks, secrets management, environment separation, configuration validation, and remediation of high-risk findings help reduce security risks during deployment.
6. Maintenance and Monitoring
Security continues after the application reaches production. Teams monitor vulnerabilities, logs, configurations, dependencies, and suspicious activity while applying patches and responding to newly discovered risks. Lessons from incidents and vulnerability remediation can also improve future development and security practices.
Note: Secure SDLC is iterative rather than strictly linear. Security activities can be revisited as requirements, architecture, code, threats, and production conditions change. This aligns with OWASP's guidance that security actions should be built into the development lifecycle rather than treated as separate activities.
Security Activities by SDLC Phase
| SDLC Phase | Security Activity | Key Practice | Deliverable/Evidence |
|---|---|---|---|
| Planning and Requirements | Security requirements definition, risk assessment | Data classification and abuse case documentation | Security requirements document, risk register |
| Architecture and Design | Threat modeling, secure architecture review | Trust boundary mapping and attack surface analysis | Threat model diagram, design review sign-off |
| Development/Implementation | Secure coding, static analysis, secrets detection | SAST and SCA integrated into commit workflow | Code scan reports, dependency audit log |
| Security Verification and Testing | DAST, API testing, penetration testing | Authenticated testing of critical workflows | Vulnerability report, remediation validation record |
| Release and Deployment | CI/CD security gates, artifact verification | Risk-based release criteria for high-severity findings | Release gate approval, deployment audit trail |
| Maintenance and Monitoring | Runtime monitoring, patch management | Continuous vulnerability tracking and metrics review | Incident log, patch and remediation timeline |
How to Implement a Secure SDLC?
Implementing a Secure SDLC requires security to become part of everyday development practices. Organizations can start with clear ownership and requirements, then integrate threat modeling, secure coding, automated checks, and risk-based security controls.
Step 1: Establish Security Ownership
Define who is responsible for security across product, engineering, security, QA, DevOps, and leadership teams. Establish clear responsibilities for security decisions, risk acceptance, vulnerability remediation, and escalation. This prevents security gaps caused by unclear ownership and makes security a shared development responsibility.
Step 2: Define Security Requirements
Document security requirements before development begins and keep them linked to business and technical requirements. Include data protection, authentication, authorization, privacy, compliance, and security acceptance criteria. Requirements should reflect the application's risks and remain updated as the software evolves.
Step 3: Threat Model Critical Features
Perform threat modeling for features that could introduce significant security risk, such as authentication, authorization, payments, sensitive data flows, and trust-boundary changes. Identify threats, attack paths, and potential mitigations early, then carry the resulting security decisions into architecture and development.
Step 4: Apply Secure Coding
Establish secure coding standards and integrate them into everyday development workflows. Developers should use peer review, input validation, safe authentication practices, secure error handling, and protected secrets. Regular security training also helps developers recognize common vulnerabilities and apply secure development patterns consistently.
Step 5: Automate Security Checks
Integrate automated security checks into developer workflows and CI/CD pipelines. Depending on the application, use SAST, software composition analysis (SCA), secrets scanning, dependency checks, and infrastructure-as-code or container scanning. Automation provides faster feedback and makes repeatable security checks practical at development scale.
Step 6: Test Running Applications
Test applications in environments that closely reflect production to identify vulnerabilities that code-level checks may miss. Use DAST, authenticated testing, API security testing, business logic testing, and penetration testing based on application risk. Validate that identified vulnerabilities can be effectively remediated.
Step 7: Establish Security Gates
Define risk-based security gates within the CI/CD pipeline to prevent unacceptable risks from moving forward. Set release criteria based on factors such as severity, exploitability, exposure, and business impact. Avoid blocking releases for every finding without considering its actual risk.
Step 8: Monitor Production
Continue security monitoring after deployment because new vulnerabilities and threats can emerge over time. Monitor application logs, exposed assets, dependencies, configurations, and suspicious activity. Establish processes for vulnerability management, patching, security alerts, and incident response to address risks discovered in production.
Step 9: Measure and Improve
Measure the effectiveness of the Secure SDLC using practical security metrics. Track remediation time, recurring vulnerabilities, security test coverage, critical findings reaching production, dependency risk age, and exception age. Use these insights to identify root causes and continuously improve security processes.
Best Practices to Follow for a Secure SDLC
Building secure software requires more than good intentions. These best practices give development and security teams a practical, repeatable framework for reducing vulnerabilities at every stage of the software development lifecycle.
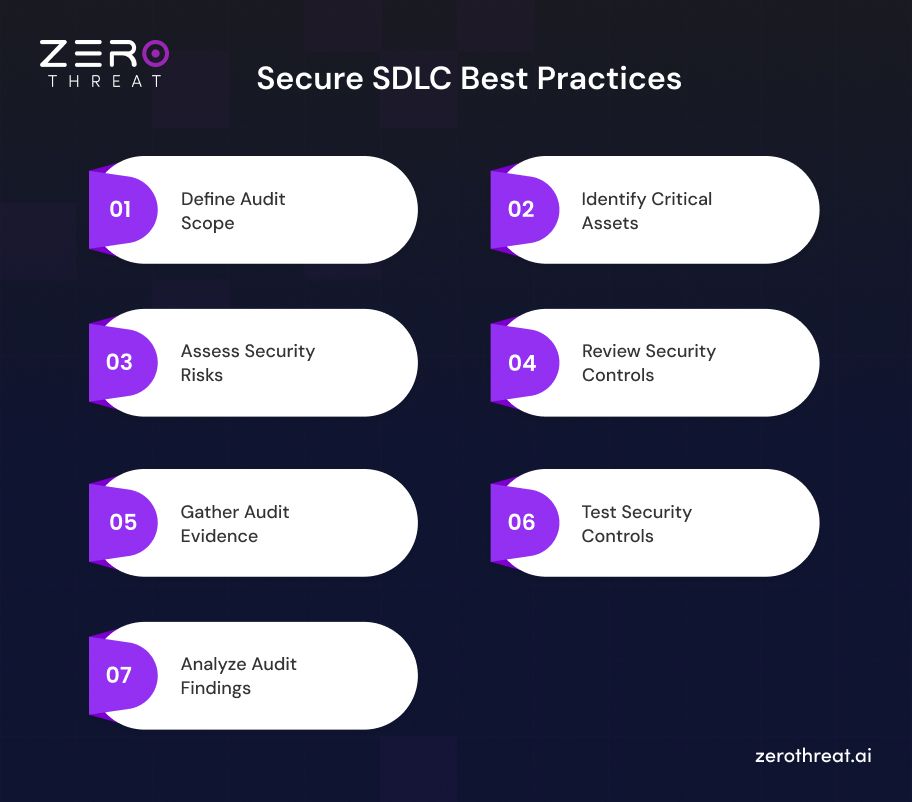
Threat Model Early
Threat modeling before development begins identifies attack paths, trust boundaries, and high-risk features like authentication and payment flows. This helps teams define security requirements upfront instead of reacting to vulnerabilities discovered later. Prioritize threat modeling for any feature touching sensitive data or external inputs.
Follow Secure Coding Standards
Secure coding standards give developers clear rules for handling input validation, output encoding, and error handling consistently. Referencing frameworks like OWASP ASVS ensures coding practices align with recognized industry benchmarks. Combined with peer review, this reduces the number of vulnerabilities introduced during implementation.
Secure Your Dependencies
Modern applications rely heavily on open-source libraries and third-party packages, making software composition analysis essential. Maintaining a software bill of materials, pinning dependency versions, and remediating known vulnerabilities keeps your supply chain trustworthy. Provenance verification and signing add another layer of protection against tampered packages.
Protect Secrets Properly
Hardcoded credentials and exposed API keys remain a common cause of breaches. Using dedicated secret managers, enforcing rotation policies, and running automated secrets detection in CI/CD pipelines prevents sensitive data from leaking into source code or version control history, where it becomes far harder to fully remove.
Secure APIs and Authentication
APIs are a primary attack surface for modern applications, so maintaining a complete API inventory matters as much as securing individual endpoints. Strong authentication, proper authorization checks, rate limiting, and input validation help prevent common flaws like broken object level authorization and insecure direct object references.
Prioritize Exploitable Risks
Not every vulnerability carries the same business impact, so raw scanner output alone is not enough to guide remediation. Validating exploitability and considering business context helps teams focus limited resources on risks that actually matter, rather than chasing every finding a scanner flags regardless of severity.
Maintain Security in Production
Security work does not end at deployment. Continuous monitoring, timely patching, configuration reviews, and ongoing vulnerability management catch issues that emerge after release. Regular security testing in production environments ensures that new threats and configuration drift get addressed before they turn into incidents.
Have questions about fitting automated pentesting into your existing Secure SDLC process? Let's talk. Get in Touch
Summing Up
Secure SDLC makes security a continuous part of software development, covering requirements, design, coding, testing, deployment, and production. Its goal is to identify and manage risks before they become harder to address.
Implementing it starts with clear security ownership and requirements, followed by threat modeling, secure coding, automated security checks, application testing, risk-based security gates, and production monitoring.
The strongest SSDLC programs also keep improving. Teams should prioritize exploitable risks, secure dependencies and secrets, protect APIs, measure security outcomes, and use lessons from incidents to strengthen future development practices.
Frequently Asked Questions
What is the role of incident response in secure SDLC?
Incident response is an essential part of a secure SDLC. It is a strategic method to detect, triage, and prevent cyber security risks in ways that minimize costs, time, and damage.
How secure SDLC and DevSecOps are different?
How does secure SDLC work at each stage of the development process?

Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.