 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs
Essential Features of a Vulnerability Scanner: What to Look For
Quick Overview: A reliable vulnerability scanner separates real security risk from noise, and choosing one comes down to specific, measurable features. This blog breaks down what actually matters: comprehensive coverage, low false positives, authenticated scanning, CI/CD integration, and risk-based prioritization. It also covers common vulnerabilities every scanner should catch, along with a quick-reference table to compare features before making a decision.
Vulnerability detection and remediation aren’t merely tasks; they are necessary to safeguard your data and assets. It becomes even more crucial when there is a constant rise in cyberattacks and simultaneously the increase in average cost of data breach reaching around USD 4.99 million. But there is a catch – finding and choosing the right vulnerability detection tool can be tricky.
It’s like finding a needle in a haystack. In that scenario, you must be careful about which tool you choose. Remember, vulnerabilities are the primary cause of cyberattacks, and a mediocre tool may fail to discover all weaknesses that increase your chances of being a victim.
There are multiple factors to consider before choosing a vulnerability detection tool, such as accuracy, compatibility, scalability, performance, and more. We have curated a list of the most essential expert-guided considerations that you should keep in mind to make the best choice.
Let’s check them out without further ado!
Vulnerabilities don't wait for your next audit. Find yours before attackers do. Start Free Security Scan
On This Page
- Top Features to Look for in a Vulnerability Scanner: Quick Glance
- What is a Vulnerability Scanner?
- Key Features to Look for in a Vulnerability Scanning Tool
- Types of Vulnerabilities a Scanner Should Detect
- Best Vulnerability Scanning Tools for Organizations
- How to Choose the Right Vulnerability Scanner: Decision Making
- Final Thoughts
Top Features to Look for in a Vulnerability Scanner: Quick Glance
Choosing the right vulnerability scanner comes down to a handful of capabilities that directly affect accuracy, speed, and coverage. Use this quick glance to compare the essentials before diving into the full breakdown below.
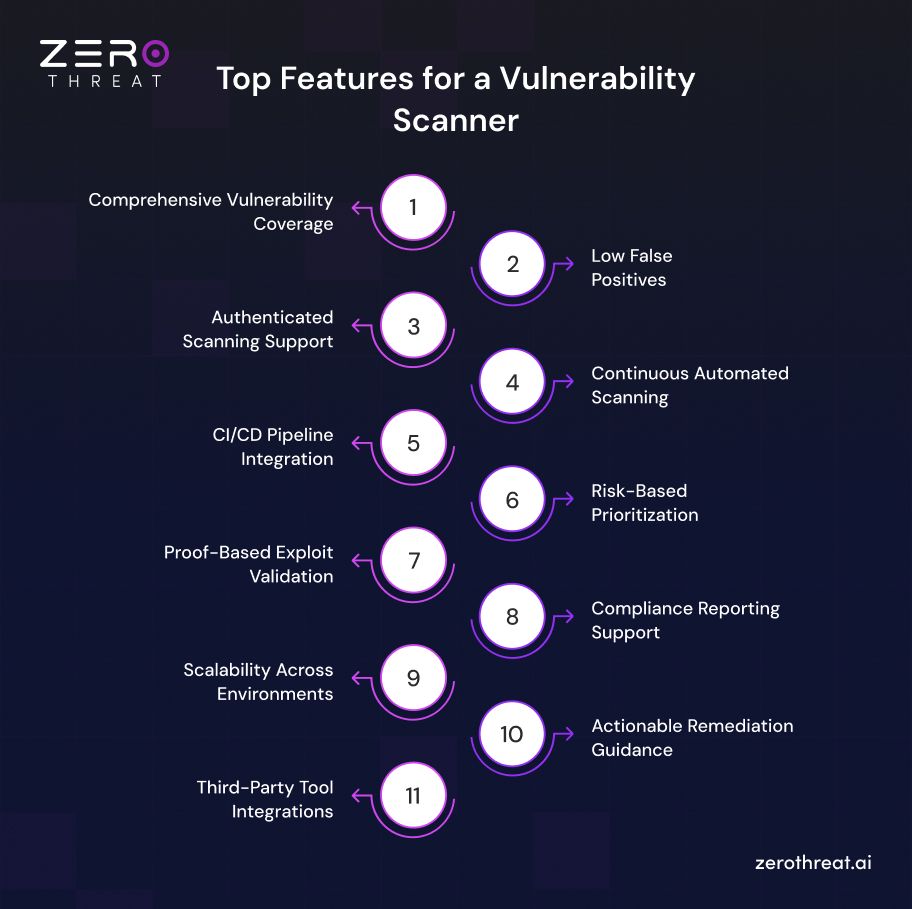
| Feature | Why It's Important |
|---|---|
| Comprehensive Vulnerability Coverage | Detects diverse security weaknesses across applications, infrastructure, APIs, cloud assets, and other attack surfaces. |
| Low False Positives | Reduces alert fatigue and helps security teams focus on genuine vulnerabilities requiring remediation. |
| Authenticated Scanning Support | Provides deeper visibility into vulnerabilities that require authorized access to systems and applications. |
| Continuous Automated Scanning | Identifies newly introduced vulnerabilities as assets, applications, configurations, and dependencies change. |
| CI/CD Pipeline Integration | Brings automated security checks into development workflows and helps identify vulnerabilities before deployment. |
| Risk-Based Prioritization | Helps teams prioritize vulnerabilities based on severity, exploitability, asset exposure, and business context. |
| Proof-Based Exploit Validation | Provides evidence that helps security teams verify whether reported vulnerabilities are actually exploitable. |
| Compliance Reporting Support | Simplifies security assessments by mapping vulnerability findings to relevant compliance and regulatory requirements. |
| Scalability Across Environments | Maintains effective vulnerability coverage as organizations expand across cloud, on-premises, hybrid, and multi-environment infrastructure. |
| Actionable Remediation Guidance | Gives security and development teams clear information to understand and fix identified vulnerabilities. |
| Third-Party Tool Integrations | Connects vulnerability findings with existing security, development, ticketing, and operational workflows. |
What is a Vulnerability Scanner?
A vulnerability scanner is a security tool that automatically examines systems, applications, networks, or APIs for known security weaknesses. It compares discovered assets and configurations against vulnerability databases, security checks, and predefined rules to identify potential attack paths.
Modern vulnerability scanners can detect issues such as outdated software, missing security patches, misconfigurations, exposed services, weak authentication controls, and known CVEs. Depending on the scanner, testing may be authenticated or unauthenticated, allowing security teams to assess both external exposure and deeper system weaknesses.
The scanner then analyzes detected vulnerabilities and typically assigns severity based on factors such as exploitability, affected assets, and potential impact. This helps security teams prioritize remediation instead of treating every finding with the same urgency.
However, vulnerability scanning is not the same as penetration testing. A scanner primarily identifies potential weaknesses through automated checks, while penetration testing validates whether vulnerabilities can actually be exploited. Using both approaches provides broader visibility into an organization's security posture.
Key Features to Look for in a Vulnerability Scanning Tool
The right vulnerability scanning tool should provide broad vulnerability coverage, accurate findings, authenticated testing, and continuous scanning to help security teams identify, prioritize, and address weaknesses effectively.
Comprehensive Vulnerability Coverage
A vulnerability scanner should identify a wide range of security weaknesses across the environments your organization actually uses. This includes networks, hosts, web applications, APIs, cloud assets, containers, databases, and exposed services.
Strong vulnerability coverage should extend beyond basic CVE detection. The scanner should identify outdated software, missing patches, insecure configurations, exposed ports, weak security controls, and vulnerabilities mapped to frameworks such as CWE and OWASP.
Coverage also depends on how frequently the scanner updates its vulnerability intelligence. New vulnerabilities emerge constantly, so a scanner that relies on outdated signatures can leave known attack paths undetected. Regular updates help security teams detect newly disclosed vulnerabilities.
For organizations with diverse attack surfaces, broad coverage reduces blind spots and gives security teams a more complete view of their vulnerability landscape. The scanner should also allow teams to expand coverage as new applications, APIs, infrastructure, and cloud resources are introduced.
Low False Positives
A vulnerability scanner should produce findings that security teams can investigate with confidence. Excessive false positives can overwhelm analysts, increase triage time, and make it harder to identify vulnerabilities that require immediate attention.
Low false-positive rates depend on accurate detection logic, contextual analysis, and effective vulnerability validation. Instead of flagging an issue solely because a vulnerable component appears to exist, the scanner should examine relevant application behavior, configurations, versions, and other available evidence.
Validation becomes particularly important for application and API security testing. A scanner that can verify whether a suspected vulnerability is actually reachable or exploitable provides more useful results than one that simply reports potential weaknesses.
Reducing false positives also improves remediation efficiency. Security teams spend less time manually validating questionable findings and more time fixing confirmed vulnerabilities. This makes accuracy an important factor when evaluating the practical value of a vulnerability scanning tool.
Authenticated Scanning Support
Authenticated scanning allows a vulnerability scanner to assess an environment using valid credentials or authorized access. This provides deeper visibility than an external scan because the scanner can inspect resources that are not visible from an unauthenticated perspective.
For example, authenticated scans can identify missing patches, insecure configurations, vulnerable software versions, excessive permissions, and other weaknesses that require access to internal system information. This makes them particularly useful for internal infrastructure and systems where external visibility is limited.
For web applications and APIs, authenticated testing can also help assess protected areas of an application. The scanner can access functionality behind login screens and evaluate security controls that anonymous users cannot reach.
A capable scanner should support secure credential handling and appropriate access controls while minimizing operational risk. Combining authenticated and unauthenticated scanning gives security teams broader visibility into both externally exposed weaknesses and vulnerabilities hidden behind access controls.
Continuous Automated Scanning
Security weaknesses can appear between scheduled vulnerability assessments as applications change, new assets are deployed, dependencies are updated, and configuration changes are introduced. Continuous automated scanning helps organizations detect these changes without relying entirely on periodic manual assessments.
A modern scanner should support recurring scans and automated security checks across relevant assets. This allows teams to monitor their attack surface more consistently and identify newly introduced vulnerabilities closer to the time they appear.
Continuous scanning is particularly useful in DevSecOps environments where applications and infrastructure can change frequently. Integrating vulnerability assessments into development and deployment workflows can help teams identify security issues before they become long-standing weaknesses.
Automation also reduces the operational effort required to maintain regular security coverage. Instead of manually initiating every assessment, security teams can define scanning schedules, monitor results, and focus their attention on findings that require investigation or remediation.
See what your attack surface is exposing with an AI-powered vulnerability scan built for deeper coverage. Run AI-Powered Scan
CI/CD Pipeline Integration
A vulnerability scanning tool should integrate with CI/CD pipelines so security checks can become part of the software delivery process. This allows teams to identify vulnerabilities during development instead of waiting for a scheduled security assessment.
Integration with tools such as source control platforms, build systems, and deployment workflows can automate vulnerability checks whenever code or application configurations change. This helps detect security issues in new releases before they reach production environments.
The scanner should also support configurable scan policies, severity thresholds, and automated failure conditions. For example, teams can configure a pipeline to block a deployment when it detects a critical vulnerability that exceeds the defined risk threshold.
CI/CD integration is particularly valuable for DevSecOps teams managing frequent releases. It makes vulnerability management a continuous activity and helps developers receive security feedback closer to the point where vulnerabilities are introduced.
Risk-Based Prioritization
A vulnerability scanner should help security teams determine which findings require attention first. Risk-based prioritization goes beyond assigning a severity level and considers factors such as exploitability, asset importance, exposure, and potential business impact.
A scanner can use CVSS scores, vulnerability priority based on context, known exploitation activity, and asset criticality to provide more meaningful risk assessments. This helps teams distinguish between a critical vulnerability on an internet-facing application and a lower-risk issue on an isolated internal system.
Effective prioritization reduces alert fatigue and helps security teams focus limited remediation resources where they can have the greatest security impact. It also provides developers with clearer guidance about which vulnerabilities should be addressed immediately.
The best approach is to combine vulnerability severity with environmental context. A scanner that understands the relationship between vulnerabilities, affected assets, and potential attack paths can provide more actionable findings than a simple list of CVE identifiers.
Proof-Based Exploit Validation
A vulnerability scanner should provide evidence that supports its findings whenever safe validation is possible. Proof-based exploit validation helps security teams determine whether a reported weakness is actually present rather than relying only on a vulnerability signature or version match.
For example, a scanner may safely validate whether an application is susceptible to a specific injection flaw or whether an exposed component can be reached through a particular attack path. This additional evidence gives analysts greater confidence during vulnerability triage.
Validation should be performed in a controlled manner that avoids unnecessary changes or disruption to the target environment. Production-safe testing is especially important when scanning live applications, APIs, and business-critical infrastructure.
Proof-based findings can also make remediation easier to understand. Security teams can use evidence such as request and response details, affected endpoints, or proof-of-concept results to reproduce the issue, verify the fix, and communicate its impact to developers.
Compliance Reporting Support
A vulnerability scanning tool should provide reporting capabilities that help organizations demonstrate their security assessment and vulnerability management activities. Compliance-focused reports can organize findings according to relevant security requirements and provide evidence for internal or external audits.
Depending on the organization's requirements, reports may support frameworks and standards such as PCI DSS, HIPAA, ISO 27001, and other regulatory or industry-specific controls. The scanner should clearly document affected assets, vulnerabilities, severity levels, remediation status, and supporting evidence.
Customizable reporting is also useful for different stakeholders. Security teams may need technical vulnerability details, while management may require summarized risk information and remediation progress. Exportable reports can simplify communication across these groups.
Security compliance reporting should complement, rather than replace, a broader vulnerability management program. A scanner provides technical evidence about identified weaknesses, while organizations remain responsible for implementing appropriate security controls and maintaining the documentation required by their specific compliance obligations.
Scalability Across Environments
A vulnerability scanning tool should scale with the size and complexity of an organization's attack surface. It should support growing numbers of assets without making scan management, performance, or vulnerability analysis difficult for security teams.
Scalability also means supporting different environments from a single security workflow. Depending on the organization, this may include on-premises infrastructure, cloud workloads, virtual machines, containers, web applications, APIs, databases, and network devices.
The scanner should maintain consistent vulnerability detection and reporting as the environment expands. It should also support features such as asset discovery, scan scheduling, centralized management, and configurable scanning policies to help teams maintain security coverage across large environments.
A scalable vulnerability scanner reduces the need to manage multiple disconnected security tools as infrastructure grows. This becomes particularly important for organizations adopting hybrid and multi-cloud architectures, where visibility across diverse assets is essential for effective vulnerability management.
Actionable Remediation Guidance
Identifying a vulnerability is only the first step. A useful vulnerability scanning tool should provide remediation guidance that helps security teams and developers understand how to address each finding effectively.
Actionable guidance should explain the affected asset, vulnerability type, severity, potential impact, and recommended remediation steps. Where relevant, it can also identify vulnerable software versions, configuration changes, patches, or security controls that can reduce the associated risk.
Clear remediation information helps reduce the time between vulnerability discovery and resolution. Developers can understand what needs to change, while security teams can track whether identified weaknesses have been addressed within established remediation timelines.
Some scanners also provide contextual evidence, references, and technical details that support investigation. These capabilities make findings easier to reproduce and verify after remediation. The goal is to turn vulnerability scan results into practical security actions rather than leaving teams with a long list of unresolved alerts.
Third-Party Tool Integrations
A vulnerability scanning tool should integrate with the security and development tools already used by an organization. Integrations help security teams centralize vulnerability data and incorporate scanning results into existing workflows.
Useful integrations can include SIEM platforms, ticketing systems, security orchestration tools, CI/CD platforms, cloud environments, issue trackers, and vulnerability management platforms. These connections can automatically send findings to the teams responsible for investigation and remediation.
API support is also valuable when organizations need to connect the scanner with custom security workflows or internal applications. Automated data exchange can reduce manual reporting and help maintain consistent vulnerability information across different systems.
Strong third-party integrations make vulnerability management more efficient by connecting detection with investigation and remediation. Instead of operating as an isolated scanning tool, the scanner becomes part of the broader security operations and DevSecOps ecosystem.
Types of Vulnerabilities a Scanner Should Detect
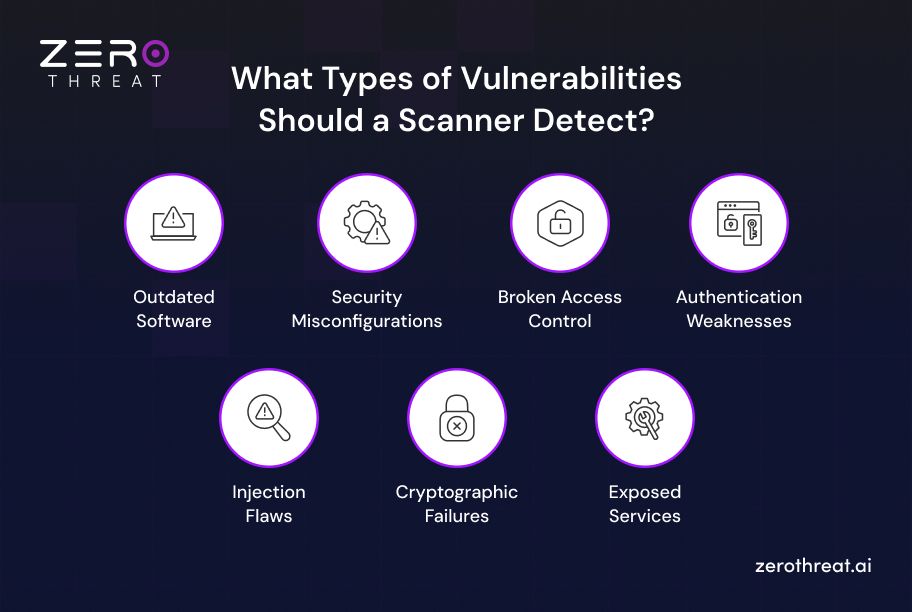
A capable vulnerability scanner should identify common weaknesses across infrastructure, applications, APIs, cloud workloads, and endpoints, including outdated software, misconfigurations, access control issues, and insecure services.
Outdated Software
Scanners should identify outdated operating systems, applications, libraries, and other software components with known security weaknesses. Version detection can help map installed components to known CVEs and identify systems requiring security updates or compensating controls.
Security Misconfigurations
Misconfigured systems can expose unnecessary services, insecure permissions, default accounts, debug features, or sensitive information. A scanner should assess configuration settings and identify weaknesses that violate established security hardening practices across the technology stack.
Broken Access Control
A scanner should detect access control weaknesses that allow users to access resources or perform actions beyond their authorized permissions. Relevant checks can include unauthorized resource access, privilege escalation, insecure direct object references, and missing API authorization controls.
Authentication Weaknesses
Vulnerability scanners should identify weaknesses in authentication and session management, including weak credentials, default passwords, missing authentication controls, insecure sessions, and ineffective protection against automated login attacks. These issues can enable unauthorized account access.
Injection Flaws
Injection vulnerabilities occur when untrusted input reaches an interpreter without appropriate validation or handling. Scanners should test relevant inputs for common injection types, including SQL injection, NoSQL injection, command injection, and cross-site scripting.
Cryptographic Failures
A scanner should identify weaknesses involving the protection of sensitive information, such as insecure encryption configurations, weak cryptographic mechanisms, and improperly protected data. These weaknesses can contribute to data exposure or unauthorized access.
Exposed Services
Unnecessary or improperly secured network services can expand an organization's attack surface. A vulnerability scanner should identify exposed ports, services, administrative interfaces, and other reachable components, then flag known vulnerabilities or insecure configurations associated with them.
Invest in enterprise-grade AppSec protection without unpredictable costs or hidden scanning fees. View Plans
Best Vulnerability Scanning Tools for Organizations
Which vulnerability scanning tool is best for you? Well, the answer to this question is subjective because it depends on the specific requirements of organizations. Nevertheless, the following are the top tools for vulnerability scanning that you can use to identify and remediate security weaknesses. Each of these tools has top-notch security features that help you protect your web apps, APIs, and other digital assets from a wide range of cyberattacks.
- ZeroThreat
- Nmap
- W3af
- ZAP
- Nessus
- Burp Suite
How to Choose the Right Vulnerability Scanner: Decision Making
Choosing a vulnerability scanner may be confusing, given so many options and the variety of tools. Therefore, you need to carefully compare different options to pick the right tool. The following steps will help you make the best choice.
Know Your Requirements
Start by understanding your needs. Find out which asset you want to scan, like a web application, network, database, API, etc. Determine the type of scanning you want – for example, you need a SAST tool to examine source code and a DAST tool to test applications at runtime. Consider other factors like compliance requirements, technologies used, and specific vulnerabilities to be addressed.
Frequency of Scanning
How frequently do you want to perform vulnerability scanning? Many scanners allow scheduled scanning, which enables you to perform scans at regular intervals or on a specific day every month or week. But many don’t have such a feature. Hence, look for options that align with your requirements.
Features vs Ease of Use
Would you prefer features over ease of use or vice versa? It is possible that a vulnerability detection tool has advanced features but is not user-friendly. Similarly, the opposite is also possible. However, you can also find tools that offer a balance between these two characteristics. Depending on your team’s skill, you should invest in the tool that aligns with your requirements.
Budget
Businesses with sufficient budgets can invest in high-end vulnerability scanning tools that offer top-notch features. However, if your business is struggling with funds or has a limited budget, you can invest in free vulnerability scanning tools. These tools have zero costs and offer excellent features to perform vulnerability scans.
Have questions about vulnerability scanning? Talk with our team about your security testing requirements. Get in Touch
Final Thoughts
Vulnerabilities are critical security risks that can be effectively tackled with continuous and real-time security assessments. Choosing the right vulnerability detection tool wins half the battle in this case, which helps you identify critical vulnerabilities with pinpoint accuracy.
From scanning and prioritization to remediation of risks, vulnerability scanners automate tasks and simplify the overall process to secure your web apps, networks, and systems. You can reduce your manual efforts and speed up vulnerability assessment by choosing the modern vulnerability scanner – ZeroThreat.
With its advanced AI-powered DAST capabilities, you can scan web apps and APIs for 130K+ vulnerabilities. It offers a next-gen crawler and actionable AI-powered remediation reports. It is fast, accurate, and user-friendly, which makes vulnerability scanning a breeze. With seamless integration into CI/CD pipelines, developers can catch vulnerabilities in SDLCs.
ZeroThreat goes beyond the OWASP top 10 and discovers out-of-band, zero-day, and other complex vulnerabilities without requiring additional settings or extensions. Give it a try and see all its benefits live.
Frequently Asked Questions
Which are the most popular vulnerability scanners?
There are many popular tools for vulnerability scanning used by organizations; some of them are given below.
- ZeroThreat
- ZAP
- Acunetix
- Burp Suite
- Nessus
What are the different types of vulnerability detection tools?
Why is a vulnerability detection tool important?
Related Articles


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.