 ZeroThreat Wins Top InfoSec Innovators 2026 Award for Penetration Testing Read more


All Blogs

Quick Overview: JavaScript security covers the browser, the server, and every npm package in between. The blog explains why it matters, breaks down the most common risks, including XSS, prototype pollution, and supply chain attacks, and walks through 10 practical best practices. It also lists common mistakes that create vulnerabilities, so teams can fix them early.
JavaScript is a dominating language in the programming world with its versatile nature and beginner-friendly syntax. While developers can build great applications using JavaScript for a wide range of platforms and purposes, they must also take the onus of making them secure.
Although JavaScript is powerful, it is not foolproof when it comes to security. Developers often leave room for mistakes to meet their rapid deployment cycles. This is where vulnerabilities creep in, allowing attackers to fulfill their malicious intentions.
Our security experts have shared some pro-level JavaScript security tips based on their experience that we are going to discuss in this blog. These tips will help you test web application security and prevent JavaScript-driven cybersecurity risks.
Stop dangerous JavaScript exploits with zero-noise automated scanning that validates real attacker paths. Start Free JS Audit
On This Page
- Why JavaScript Security Matters for Modern Applications
- Common JavaScript Security Risks You Should Know
- Best Practices for JavaScript Security: Detailed Overview
- Key Mistakes to Avoid in JavaScript to Prevent Vulnerabilities
- Tips for Developers to Enhance the Security of JavaScript Applications
- To Wrap Up
Why JavaScript Security Matters for Modern Applications
JavaScript security matters because JavaScript now runs at every layer of a modern application: in the browser, on the server through Node.js, and inside third-party packages and scripts. A weakness in any one layer can expose user sessions, sensitive data, or core business logic.
The risk comes from three places:
- Code that runs on the user's device: Anything shipped to the browser can be read, changed, or abused. Attackers can inspect front-end code, find API endpoints, and tamper with requests. That is why client-side checks can never act as a security control on their own.
- Node.js on the backend: The same language now handles authentication, database queries, and file access. A flaw here can lead to server-side compromise, not just browser-level damage.
- Code you did not write: Modern projects pull in large trees of npm packages, and each one is a trust decision. OWASP's 2025 Top 10 expanded its old "vulnerable components" category to cover the full software supply chain, including dependencies, build systems, and distribution infrastructure.
OWASP data also shows how these risks overlap. Broken access control still sits at the top of the 2025 list. Injection, which covers SQL injection, cross-site scripting (XSS), and command injection, remains in the Top 10 at A05. Both map directly to common JavaScript mistakes, such as trusting the front end to enforce permissions or inserting untrusted data into the DOM.
The practical point is that no single fix covers all three layers. Input validation will not stop a compromised package, and a locked-down server will not protect a page that renders unsafe content. JavaScript security needs controls in the browser, on the server, and across dependencies. The most common browser-side threat, XSS, is the right place to start.
Common JavaScript Security Risks You Should Know
Most JavaScript security issues fall into a handful of recurring categories. The nine risks below cover the browser, the server, and the dependencies that connect them.
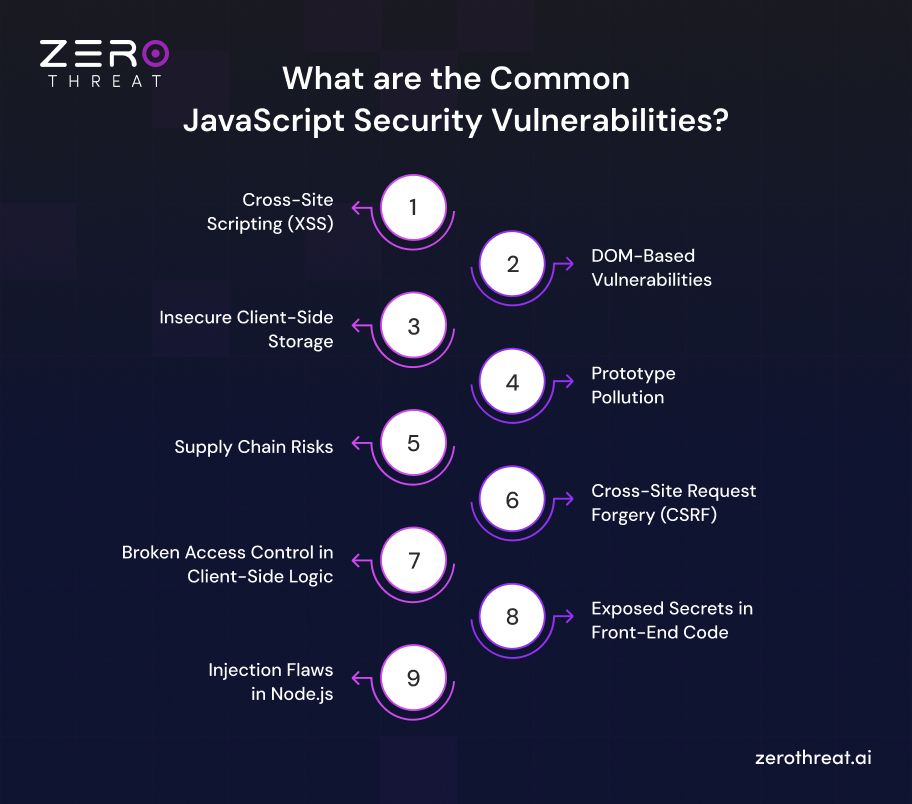
Cross-Site Scripting (XSS)
XSS lets attackers inject malicious JavaScript into a page that other users load. The script runs with the victim's privileges, so it can steal session data, change page content, or perform actions on their behalf. It usually starts with unsanitized user input.
DOM-Based Vulnerabilities
DOM-based vulnerabilities occur when client-side code reads untrusted data, such as a URL fragment or query parameter, and passes it to a dangerous sink like innerHTML, eval(), or document.write(). The payload may never reach the server, so server-side filters often miss it.
Insecure Client-Side Storage
Storing authentication tokens, session identifiers, or personal data in localStorage or sessionStorage exposes them to any script running on the page. If an XSS flaw exists, attackers can read that data instantly. Browser storage is convenient, but it was never designed to hold secrets.
Prototype Pollution
Prototype pollution happens when an attacker modifies Object.prototype through unsafe merge, clone, or assignment operations. Objects across the application then inherit the injected properties. This can change application logic, bypass security checks, or lead to remote code execution in some Node.js applications.
Supply Chain Risks
Modern JavaScript projects often depend on hundreds of npm packages, and any of them can be compromised. Attackers publish malicious packages, hijack maintainer accounts, or use typosquatted names. The malicious code then runs inside your build or application with the same trust as your own.
Cross-Site Request Forgery (CSRF)
CSRF tricks a logged-in user's browser into sending an unwanted request to a trusted application. The browser attaches session cookies automatically, so the server may treat the forged request as legitimate. It can change account settings, move funds, or alter data.
Broken Access Control in Client-Side Logic
Hiding a button or route in the UI does not restrict access. If the server does not verify permissions on every request, users can call the underlying API directly. Client-side role checks only change what the interface shows, not what an attacker can reach.
Exposed Secrets in Front-End Code
Front-end bundles are public. API keys, tokens, and credentials hardcoded in JavaScript files, source maps, or public repositories can be found by anyone. Attackers use them to access backend services, cloud resources, or third-party accounts without ever exploiting a vulnerability.
Injection Flaws in Node.js
Injection flaws occur when untrusted input is treated as code or commands. In Node.js, this includes NoSQL injection, OS command injection through child_process, and code execution through eval() or unsafe deserialization. One unchecked input can expose data or the server itself.
Benchmark your JavaScript architecture against mordern attack vectors using intelligent automated scanning. Test My Web App
Best Practices for JavaScript Security: Detailed Overview
These practices cover the browser, the server, and the build pipeline. Each one comes down to specific actions a development team can add to its workflow, starting with the most common entry point: user input.
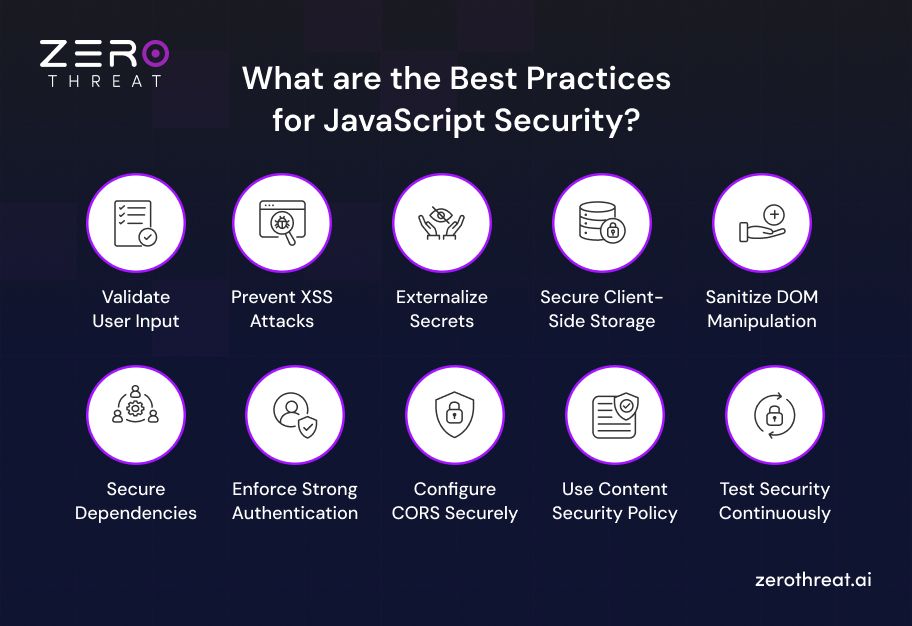
1. Validate User Input
Treat every input as untrusted, including form fields, URL parameters, headers, cookies, and API payloads. Validation must run on the server. Client-side checks improve user experience, but attackers can bypass them easily.
- Use an allowlist. Define the valid type, length, format, and range, and reject everything else.
- Enforce request shapes with a schema library such as Zod, Joi, or Ajv.
- Reject unknown properties so unexpected keys like __proto__ never reach application logic.
- Use parameterized queries instead of building queries with string concatenation.
import { z } from "zod"; const signupSchema = z.object({ email: z.string().email().max(254), displayName: z.string().min(1).max(50), }).strict(); const result = signupSchema.safeParse(req.body); if (!result.success) { return res.status(400).json({ error: "Invalid input" }); }2. Prevent XSS Attacks
The core XSS defense is encoding data for the context where it is rendered. Frameworks like React, Angular, and Vue do this by default, so most XSS bugs appear where developers bypass that protection.
- Avoid framework escape hatches such as dangerouslySetInnerHTML, v-html, and bypassSecurityTrustHtml.
- Sanitize rich text with a maintained library like DOMPurify before rendering it.
- Use context-aware encoding. HTML body, attribute, JavaScript, and URL contexts each need different handling.
- Set HttpOnly on session cookies so injected scripts cannot read them.
3. Externalize Secrets
Everything shipped to the browser is public. API keys, tokens, and credentials in JavaScript bundles, source maps, or public repositories can be found and reused by anyone.
- Keep secrets on the server and load them from environment variables or a secrets manager.
- Check your build tool's naming rules. Variables with prefixes such as NEXT_PUBLIC_ or VITE_ are bundled into client code.
- Route third-party API calls through a backend proxy. If a key must be public, restrict it by domain and scope.
- Run secret scanning (Gitleaks and TruffleHog are common open-source options) in pre-commit hooks and CI.
- Rotate any exposed key immediately. Git history keeps deleted secrets.
4. Secure Client-Side Storage
Browser storage should hold as little as possible. Any script on the page can read localStorage and sessionStorage, so one XSS flaw exposes everything inside them.
- Keep session tokens in cookies with HttpOnly, Secure, and SameSite flags instead of localStorage.
- Do not store passwords, personal data, or long-lived tokens in the browser.
- Use short-lived access tokens and rotate refresh tokens on each use.
- Clear stored data on logout and session expiry.
HttpOnly stops script from reading the token, but injected script can still send requests inside the user's session. Pair this practice with XSS prevention and SameSite cookies.
5. Sanitize DOM Manipulation
DOM-based flaws appear when untrusted data reaches a dangerous sink. The fix is to avoid those sinks or to put a gate in front of them.
// Unsafe: parses the value as HTML element.innerHTML = userComment; // Safer: treats the value as plain text element.textContent = userComment;- Avoid eval(), new Function(), document.write(), and string arguments to setTimeout().
- Validate URLs before using them in href or src. Allow only https: and http: to block javascript: URLs.
- Read location.hash and query parameters as untrusted input, then validate them before use.
- Enable Trusted Types, which reached Baseline across all major browsers in February 2026. With the require-trusted-types-for 'script' CSP directive set, the browser refuses raw strings in sinks like innerHTML unless a defined policy approved them.
6. Secure Dependencies
Every npm package runs with the same trust as your own code. Controlling what enters the project, and how it is installed, reduces supply chain exposure.
- Commit the lockfile and use npm ci in CI so builds match what was reviewed.
- Run npm audit in the pipeline and automate updates with Dependabot or Renovate.
- Check maintainers, release history, and exact package name before adding a new package, since typosquatting is common.
- Add Subresource Integrity (SRI) hashes to scripts loaded from a CDN.
- Remove unused packages. Consider --ignore-scripts where install scripts are not needed.
<script src="https://cdn.example.com/lib.min.js" integrity="sha384-BASE64\_HASH\_HERE" crossorigin="anonymous"></script>7. Enforce Strong Authentication
Authentication proves identity, and weak implementations are a direct path to account takeover. Use proven components instead of custom logic.
- Hash passwords on the server with Argon2id or bcrypt. Never hash or store them in client code.
- Require multi-factor authentication for admin and other sensitive accounts.
- Rate limit login and password reset endpoints to slow credential stuffing.
- Use established libraries or an identity provider (OAuth 2.0 and OpenID Connect) rather than building from scratch.
- Regenerate the session ID after login. For JWTs, verify the signature and algorithm, and validate exp, iss, and aud.
Authentication does not replace authorization. The server must still check permissions on every request.
8. Configure CORS Securely
CORS controls which origins can read responses from your API in a browser. It is not an authentication or access control mechanism, so a permissive policy can expose authenticated data to other sites.
- Allow specific origins only. Never echo the Origin header back without checking it against an allowlist.
- Do not pair Access-Control-Allow-Origin: * with credentials, and do not work around browser blocking by reflecting any origin.
- Limit allowed methods and headers to what the application needs.
- Send Vary: Origin when the response changes by origin.
import cors from "cors"; const allowed = \["[https://app.example.com](https://app.example.com)", "[https://admin.example.com](https://admin.example.com)"\]; app.use(cors({ origin: (origin, callback) => callback(null, !origin || allowed.includes(origin)), methods: \["GET", "POST"\],credentials: true, }));9. Use Content Security Policy
Content Security Policy (CSP) is a response header that tells the browser which script sources to trust. It does not fix vulnerable code, but it limits what an injected script can do.
- Use a strict, nonce-based policy instead of long domain allowlists.
- Generate a fresh nonce on every response.
- Remove inline scripts and avoid unsafe-inline.
- Deploy with Content-Security-Policy-Report-Only first, review the violation reports, then enforce.
Content-Security-Policy: script-src 'nonce-{RANDOM}' 'strict-dynamic'; object-src 'none'; base-uri 'none'; frame-ancestors 'self'10. Test Security Continuously
Security controls drift as code, dependencies, and configurations change. Testing at several stages catches different problems.
- Run static analysis (SAST) on every pull request. ESLint with security rules is a common starting point.
- Run software composition analysis on each build to catch vulnerable dependencies.
- Run dynamic testing (DAST) against a running staging environment with authenticated sessions. DOM-based XSS, CORS misconfigurations, and missing headers often show up only at runtime.
- Set clear thresholds for failing a build on high-severity findings.
- Retest every fix, and schedule periodic manual penetration testing for business logic flaws that automated tools miss.
Fixing flaws after release costs more than catching them early. See what testing costs. Explore Pricing Plans
Key Mistakes to Avoid in JavaScript to Prevent Vulnerabilities
JavaScript vulnerabilities often result from simple development mistakes that can expose applications to unnecessary security risks. Understanding these common mistakes helps developers identify weak coding practices and take preventive measures before attackers can exploit them.
Coding Vulnerabilities
Often, vulnerabilities occur at the coding level due to faster development cycles that leave little time for security testing. Apart from this, developers integrate different external open-source packages and libraries that can have vulnerabilities, making the overall application susceptible to cyberattacks. The use of these packages and libraries also widens the attack surface of an application.
Unsafe Input Processing
Input is vital for any interactive web application. Users can enter data that is processed by such a web app. However, if your JavaScript doesn’t validate user inputs, it is likely to get hit by a cyberattack. An attacker can enter malicious data or scripts in input fields that your web app could inadvertently execute. This vulnerability occurs when your web app fails to check every input for a specific format and structure to avoid unexpected data.
Unintended Script Execution
Commonly, JavaScript is embedded in HTML and executed on the client side. While this enhanced rendering speed, there are security risks in this approach. An attacker can embed a malicious script that can be executed on the client’s computer. The most common attack vector is cross-site scripting. Code sanitization can help prevent this threat.
Using Only Client-Side Validation
This vulnerability occurs when data validation is done only on the client-side and there are no such measures implemented on the server. An attacker can take advantage of this vulnerability to send data to the server and execute it without any restriction. The attacker can execute malicious scripts with this security weakness.
Insecure Third-Party Dependencies
JavaScript applications often rely on third-party packages and libraries to speed up development and add functionality. However, using outdated or vulnerable dependencies can introduce security weaknesses into the application. Failing to regularly review, update, and remove unnecessary dependencies can therefore increase the overall attack surface and make the application more vulnerable to cyberattacks.
Tips for Developers to Enhance the Security of JavaScript Applications
Complex web apps heavily based on JavaScript are more susceptible to cyberattacks, even if there is a single vulnerability. Hence, developers must think beyond fixing common bugs and loopholes. The following tips help you enhance security for such web apps.
Perform Continuous Testing
You can find loopholes in your web application with continuous security testing. It involves using an automated penetration testing tool like ZeroThreat to test and detect JavaScript vulnerabilities. The tool performs simulated attacks on the target application like a hacker to identify loopholes.
Content Security Policy
Apart from adhering to the above JavaScript best practices, CSP provides another layer of protection. Content Security Policy (CSP) is a standard that helps restrict the loading of resources like images, CSS, JavaScript, etc. It helps you minimize potential risks of clickjacking and XSS (Cross-Site Scripting). It is a robust protection against risks that could overcome cross-origin policy.
Quality Coding
Knowing the ins and outs of JavaScript is crucial to writing quality code that helps to build secure web applications. Quality coding is essential to minimize bugs and errors that lead to security loopholes. A good understanding of concepts like hoisting, callbacks, scope declarations, and more can help avoid vulnerabilities that could lead to JavaScript security risks.
Want these practices verified continuously? Run AI-powered pentesting on a web app now. Let's Get Started!
To Wrap Up
JavaScript is among the most popular programming languages out there that is used in both front-end and back-end development. With the widespread use of this programming language, it has become a common target for attackers. Hence, securing your JavaScript application becomes a key challenge.
Implementing JavaScript security best practices mentioned in this article can help you minimize potential risks. You can build secure web apps with these best practices. In addition to following the best practices, penetration testing is also helpful in identifying weaknesses and securing your web app.
You can use ZeroThreat, which is a reliable AI automated pentesting tool, to discover vulnerabilities and secure your web apps. It can help you test single-page applications and web apps with heavy JavaScript code.
Frequently Asked Questions
What are the best ways to protect credentials in JavaScript?
Keep credentials out of client-side code. Store API keys and secrets in server-side environment variables or a secrets manager, route third-party calls through a backend proxy, use HttpOnly cookies for session tokens, run secret scanning in CI, and rotate any exposed key immediately.
How to secure JavaScript?
How does JavaScript security work?
What is the importance of JavaScript security?
What measures should be taken to secure JavaScript at server level?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.