 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs
Cross Site Request Forgery: How it Works and How to Prevent It?

Quick Overview: Cross-Site Request Forgery remains one of the most exploited web vulnerabilities today. This blog breaks down what CSRF is, how attackers forge requests using a victim's own session, and the different types you need to watch for. You'll also learn how to detect CSRF vulnerabilities, the best practices to prevent them, and how ZeroThreat validates your defenses with proof-based testing.
Whether you are a CISO or a security expert, acquiring knowledge of potential web app security risks is critical for creating secure digital solutions. Users engage with a web application and share their data only when they trust it.
Keeping that trust intact requires an understanding of the threat landscape and practices to mitigate security risks. One of the most important threat vectors is Cross-site Request Forgery or CSRF. With a CSRF attack, a bad actor can compel a user to perform an unwanted action.
The resulting action can be to delete some data, change a password, make a financial transaction, or more. Understanding what CSRF is and how it occurs can help you protect your web applications more effectively.
In this article, CSRF is explained in detail providing the information you need to detect the vulnerability using manual testing and automated pentesting tool. Besides, you can also find the best practices to some ways to prevent this threat in the first place. With that said, let's get started.
Your applications CSRF tokens might be weaker than you think. Get proof in minutes. Get Started Now
Table of Contents
- What is Cross-Site Request Forgery (CSRF)?
- How CSRF Works: Step-by-Step Attack Flow
- What are the Common Types of CSRF Attacks?
- What are the Consequences of a CSRF Attack?
- Ways to Detect CSRF Vulnerabilities in Web Applications
- Best Practices to Prevent Cross-Site Request Forgery Attacks
- How ZeroThreat Helps You Detect and Prevent CSRF Vulnerabilities
- To Wrap Up
What is Cross-Site Request Forgery (CSRF)?
Cross-Site Request Forgery (CSRF) is a web security vulnerability that tricks an authenticated user’s browser into sending an unintended request to a trusted application. The application may process it as legitimate.
CSRF primarily affects applications that rely on browser-based authentication, particularly session cookies, to identify users. If the server does not verify the request’s origin or intent, unauthorized state-changing actions may be accepted.
A successful CSRF attack can cause actions such as changing account details, updating passwords, transferring funds, or modifying application settings. The attacker does not need to know the user’s credentials.
CSRF is commonly associated with web applications that perform sensitive actions without adequate request validation. Strong CSRF protection uses controls such as anti-CSRF tokens, SameSite cookies, and origin validation to prevent unauthorized requests.
How CSRF Works: Step-by-Step Attack Flow
A CSRF attack abuses a user’s authenticated session to make a trusted web application accept an unauthorized state-changing request as if it came from the user.
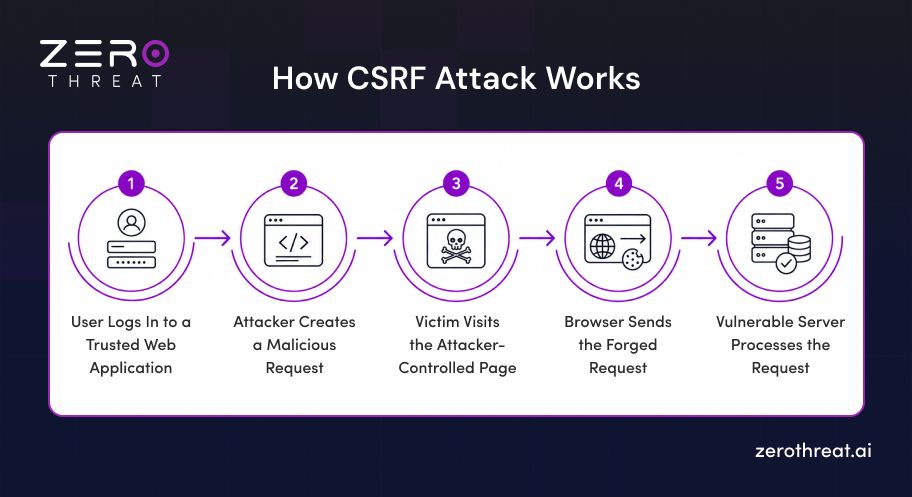
1. User Logs In to a Trusted Web Application
The victim first authenticates with a trusted web application, such as an online banking or e-commerce platform. The application establishes an authenticated session, commonly using a session cookie.
2. Attacker Creates a Malicious Request
The attacker prepares a forged request targeting a state-changing function on the trusted application. This could involve changing an account detail, submitting a transaction, or modifying a user setting.
3. Victim Visits the Attacker-Controlled Page
The attacker needs the victim to visit a malicious website, open a crafted link, or interact with attacker-controlled content. The page contains a request designed to target the trusted application.
4. Browser Sends the Forged Request
When the request is triggered, the victim’s browser may automatically include authentication credentials associated with the trusted application, such as session cookies. This allows the request to appear authenticated.
5. Vulnerable Server Processes the Request
If the application does not verify that the request was intentionally generated by the user, the server may process the forged request using the victim’s existing privileges. Effective CSRF defenses validate request intent before allowing state-changing actions.
Manual reviews miss what continuous testing catches. See what your app is hiding. Test My Web App
What are the Common Types of CSRF Attacks?
CSRF attacks can take different forms depending on where the malicious request originates and how it reaches the vulnerable application. Here are the five types you need to know.
Reflected (Classic) CSRF
This is the most common form of CSRF. The attacker crafts a malicious link, image tag, or auto-submitting form that fires a forged request the moment the victim visits the page. No stored payload is needed. The request executes instantly using the victim's active session cookie, often through a simple GET or POST call.
Stored CSRF
Here, the attacker plants the malicious payload directly on the trusted site itself, inside a comment, forum post, or user profile field. When another logged-in user views that content, the forged request fires automatically. This makes stored CSRF harder to trace, since the trigger sits inside content the victim's own browser trusts.
Login CSRF
Instead of targeting an authenticated session, login CSRF tricks the victim into unknowingly logging into the attacker's account. Any data the victim enters afterward, searches, saved preferences, or payment details, gets tied to the attacker's account instead of their own. This variant exploit login forms that don't validate the request's origin before processing it.
Client-Side CSRF
Client-side CSRF happens when forged requests get triggered through JavaScript, DOM manipulation, or client-side routing instead of a direct HTML form submission. Attackers exploit weak origin checks in fetch or XHR calls, often bypassing traditional server-side CSRF tokens entirely. Modern single-page applications are especially exposed to this variant.
Multi-Step CSRF
Multi-step CSRF chains several forged requests together to complete a multi-stage action, like a wizard-style checkout or a multi-page settings update. The attacker automates each step using hidden, auto-submitting forms that fire in sequence. This lets the attack complete complex, multi-part transactions the victim never intended to authorize.
What are the Consequences of a CSRF Attack?
Any kind of cyberattack is always a risk to an organization that affects its business, users, and digital assets. Hence, understanding the impact of CSRF is no rocket science. It is as bad as an SQL injection or any other type of attack.
The following are the consequences of a successful cross-site request forgery attack.
Data Manipulation
A bad actor can exploit the trust a web application has in authenticated users to carry out CSRF attacks. In this case, web apps cannot distinguish between legitimate users and users with crafted requests. As a result, bad actors can force users to send state-changing requests. This request could be related to modifying data, like deleting or adding new information.
Server Control
A bad actor can take over a server control by sending a state-changing request that could modify configuration settings. It can happen when the targeted user has administrative privileges. This will allow the bad actor to access unauthorized data and resources.
Malware Installation
Another critical security concern is the installation of malware on the target server. A bad actor may exploit web application vulnerabilities to install ransomware on the host server. It will lock your essential data and resources until a certain amount is paid to the bad actor. The data will be encrypted with a strong key, which will make it hard to recover the data.
Reputational Damage
A cross-site request forgery attack can also cause reputational damage due to an incident of data breach. It will impact your business. Consequently, it will be hard for you to acquire new customers and retain existing ones.
Ways to Detect CSRF Vulnerabilities in Web Applications
You can detect CSRF vulnerabilities through manual testing or automated scanning. Both approaches check whether an application validates request origin, uses proper tokens, and rejects forged requests reliably. Combining manual testing with automated detection tool ensures comprehensive coverage across complex web application workflows.
Manual Testing
Start by mapping authenticated workflows and identifying state-changing requests, such as profile updates, password changes, or financial transactions. Inspect requests for CSRF tokens and determine whether sensitive actions depend only on browser-managed session credentials.
Next, replay a relevant request without its CSRF protection mechanism or with an invalid token. A successful state change indicates that the server may not adequately validate the request. Test different HTTP methods and verify whether protections are consistently enforced across sensitive endpoints.
Automated Detection Tool
Automated web vulnerability scanners can analyze application requests and identify potential CSRF weaknesses across multiple endpoints. These tools can help security teams discover missing or ineffective CSRF tokens and prioritize requests that require further validation.
Automated findings should still be validated manually because scanners may identify potential issues rather than confirmed exploitable vulnerabilities. Combining automated scanning with authenticated testing and proof-of-concept validation provides broader coverage and helps reduce false positives.
Best Practices to Prevent Cross-Site Request Forgery Attacks
Preventing CSRF attacks requires multiple layers of protection that verify request legitimacy, restrict cross-origin behavior, and protect sensitive state-changing operations from unauthorized browser requests. Here are seven proven security controls that stop forged requests before they reach your server.
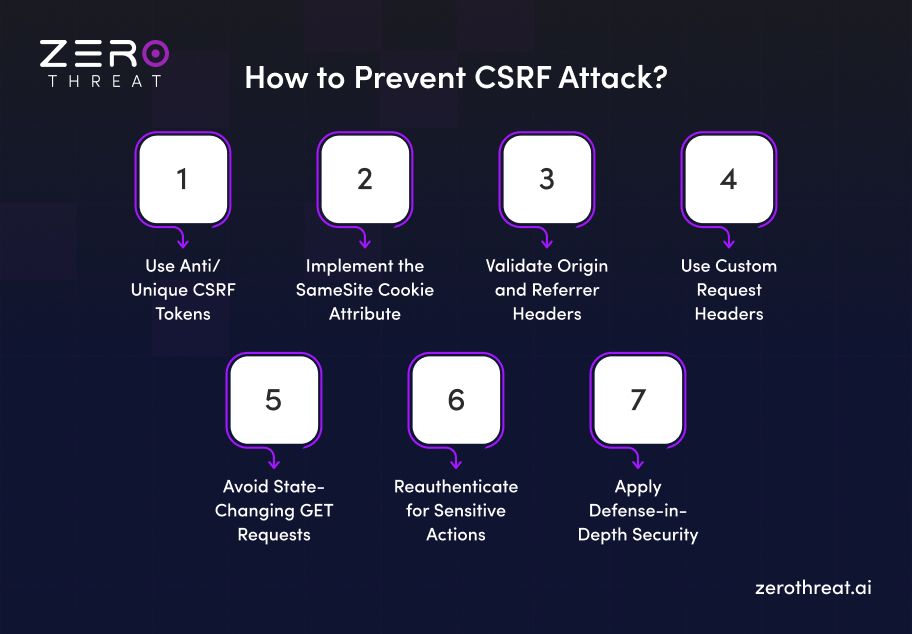
Use Anti/Unique CSRF Tokens
Generate a unique, unpredictable CSRF token for authenticated sessions or sensitive requests and validate it server-side. The token should be difficult for attackers to obtain or guess, preventing forged requests from being accepted even when authentication cookies are automatically included.
Implement the SameSite Cookie Attribute
Set the SameSite attribute on authentication cookies to control when browsers send them with cross-site requests. Using SameSite=Lax or SameSite=Strict where appropriate can significantly reduce CSRF exposure by restricting cross-site cookie transmission.
Validate Origin and Referrer Headers
Validate the Origin header and, when appropriate, the Referrer header for sensitive state-changing requests. These headers can help determine whether a request originated from an approved website and provide an additional layer of CSRF protection.
Use Custom Request Headers
For APIs and AJAX-based applications, require a custom HTTP header that a cross-origin attacker cannot freely send without satisfying browser CORS restrictions. Validate this header server-side before processing sensitive requests to strengthen cross-origin request protection.
Avoid State-Changing GET Requests
Do not use GET requests for actions that modify application state, such as changing account settings or deleting resources. Reserve GET for safe, read-only operations and use appropriate methods such as POST, PUT, PATCH, or DELETE for state changes.
Reauthenticate for Sensitive Actions
Require users to reauthenticate before performing highly sensitive operations, such as changing passwords, updating payment information, or modifying security settings. This adds another verification layer and limits the impact of unauthorized requests reaching protected application functions.
Apply Defense-in-Depth Security
Do not rely on a single CSRF defense. Combine anti-CSRF tokens, SameSite cookies, origin validation, secure session management, appropriate HTTP methods, and reauthentication to create multiple protection layers against forged requests.
How ZeroThreat Helps You Detect CSRF Vulnerabilities
ZeroThreat helps security teams identify CSRF vulnerabilities by testing state-changing requests across authenticated web application workflows. Its web app pentesting capabilities analyze CSRF protection mechanisms, including token enforcement and request validation.
The platform can test authenticated areas and user journeys, making it possible to assess security controls beyond public pages. This is important because CSRF risks often involve actions available only after authentication, such as account or profile changes.
ZeroThreat validates whether a suspected weakness can lead to a real security impact instead of relying only on theoretical findings. Its exploit validation approach provides reproducible evidence that helps teams understand and prioritize confirmed vulnerabilities.
By continuously testing modern web applications, ZeroThreat helps teams detect CSRF and other application security weaknesses as workflows and endpoints change. This supports a proactive DevSecOps approach where security testing becomes part of ongoing application protection.
Not sure where your app stands against CSRF and other attacks? Get a live walkthrough Connect With Us
To Wrap Up
Cross-Site Request Forgery remains a critical threat to web applications by exploiting trusted user sessions. Attackers bypass authentication controls to execute unauthorized state-changing actions without the user's knowledge.
Securing applications requires a multi-layered defense strategy. Implementing anti-CSRF tokens, configuring SameSite cookie attributes, and validating origin headers effectively block unauthorized cross-site traffic from reaching vulnerable endpoints.
Continuous automated testing ensures your applications remain resilient against emerging threats. Validate your security posture today and secure your endpoints against CSRF vulnerabilities by signing up with ZeroThreat.
Frequently Asked Questions
How are cross-site request forgery and cross-site scripting different?
Often CSRF and XSS are confused with each other. While there are some similarities, there are two different types of cyber threats. CSRF attacks exploit the trust that a web application has in an authenticated user. On the other hand, an XSS attack exploit the trust that a user has in a web application.
Is cross-site request forgery a cyberattack?
CSRF tokens: what are they?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.