 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs
What is the NIST Cybersecurity Framework? A Complete Guide to CSF 2.0
Quick Overview: NIST CSF 2.0 gives organizations a practical way to manage cybersecurity risk with a clear, flexible framework. This guide explains what the NIST Cybersecurity Framework is, what changed from CSF 1.1 to 2.0, and how its six Core Functions work together. It also covers implementation steps, key benefits, ZeroThreat's role, and common questions about CSF 2.0.
A strong cybersecurity program needs more than security tools. It needs a clear way to understand risk, prioritize action, and keep security aligned with business goals.
That is where the NIST Cybersecurity Framework (CSF) 2.0 becomes valuable.
Released in 2024, CSF 2.0 gives organizations a flexible approach to manage cybersecurity risk, regardless of their size or industry. Its six Functions, including the new Govern Function, provide a practical structure for improving security posture.
This guide explains what NIST CSF 2.0 is, how it differs from CSF 1.1, what each Function covers, and how organizations can implement it effectively. Plus, it covers the organizational benefits of applying NIST framework and how ZeroThreat's AI-driven pentesting tool can help you meet the requirements.
See where your applications actually stand against CSF 2.0 outcomes in minutes, not months. Start Testing Free
Table of Contents
- What is the NIST Cybersecurity Framework?
- What is NIST CSF 2.0 and What Changed From CSF 1.1 to CSF 2.0?
- NIST CSF 1.1 vs. 2.0: A Side-by-Side Comparison
- Core Functions of the NIST Cybersecurity Framework 2.0
- How do the Six NIST CSF 2.0 Functions Work Together?
- How to Implement NIST Cybersecurity Framework 2.0?
- Benefits of the NIST Cybersecurity Framework
- How ZeroThreat Can Help with NIST CSF Mapping?
- To Wrap Up
What is the NIST Cybersecurity Framework?
The NIST Cybersecurity Framework (CSF) is a voluntary set of guidelines developed by the National Institute of Standards and Technology to help organizations manage and reduce cybersecurity risk. It gives you a structured, common language for security decisions.
Originally built for critical infrastructure, the framework now applies to any organization, regardless of size, sector, or existing security maturity. It works alongside standards like ISO 27001 and NIST SP 800-53, not in place of them.
NIST released CSF 2.0 in February 2024, adding a sixth function called Govern. This addition puts cybersecurity risk management directly into leadership and business strategy conversations, not just IT.
At its core, CSF 2.0 organizes cybersecurity outcomes into functions, categories, and subcategories. This structure lets you assess your current posture, set target goals, and track progress over time.
What is NIST CSF 2.0 and What Changed from CSF 1.1 to CSF 2.0?
NIST CSF 2.0 is an updated cybersecurity risk management framework released by NIST in February 2024. It helps organizations of any size or sector assess, prioritize, communicate, and manage cybersecurity risks through a flexible, outcome-based approach.
Govern Became a New Core Function
CSF 1.1 addressed governance across other areas of the framework. CSF 2.0 gives it a dedicated Govern Function, making cybersecurity strategy, risk appetite, policies, roles, responsibilities, and oversight explicit parts of the security program.
The Framework Now Applies to All Organizations
CSF 2.0 expands beyond its original critical infrastructure focus. It is designed for organizations across industries, sizes, and maturity levels, making the framework more relevant to businesses that need a flexible approach to cybersecurity risk management.
Implementation Guidance Became More Actionable
CSF 2.0 adds Implementation Examples that show practical actions for achieving specific cybersecurity outcomes. It also expands guidance around Profiles and action planning, helping organizations translate framework outcomes into concrete security activities.
Supply Chain Risk Management Gets Greater Emphasis
CSF 2.0 strengthens cybersecurity supply chain risk management by addressing third-party relationships, suppliers, and dependencies more directly. This helps organizations account for risks that can be entered through vendors, software providers, service partners, and other external dependencies.
Existing CSF Functions and Categories Were Restructured
CSF 2.0 also reorganizes several Categories and Subcategories across the framework. Some content from CSF 1.1 was moved into different Functions, while new areas such as Platform Security, Technology Infrastructure Resilience, and Improvement were introduced.
NIST CSF 1.1 vs. 2.0: A Side-by-Side Comparison
| Aspect | CSF 1.1 (2018) | CSF 2.0 (2024) |
|---|---|---|
| Core Functions | 5: Identify, Protect, Detect, Respond, Recover | 6: adds Govern as a standalone function |
| Governance | Covered lightly under Identify | Dedicated function with executive and board oversight |
| Scope | Focused on critical infrastructure | Applies to any organization, regardless of size or sector |
| Supply Chain Risk | General third-party guidance | Expanded, dedicated vendor and supply chain risk guidance |
| Implementation Support | High-level recommendations only | Adds concrete Implementation Examples per subcategory |
| Compliance Alignment | Loosely tied to ISO 27001, NIST SP 800-53 | Stronger mapping to current compliance frameworks |
Continuous NIST CSF compliance requires continuous defense. Automate your API and web pentesting. Automate Pentesting Now
Core Functions of the NIST Cybersecurity Framework 2.0
The NIST CSF 2.0 Core Functions provide a structured approach to cybersecurity risk management, helping organizations govern, identify, protect, detect, respond to, and recover from cybersecurity threats. Here is a dive into each of them:
Govern (GV)
The Govern function establishes how an organization directs and manages cybersecurity risk. Introduced as a dedicated Function in NIST CSF 2.0, it connects cybersecurity decisions with business objectives, legal requirements, risk tolerance, and enterprise risk management.
It defines the expectations that guide how security should operate across the organization. This includes establishing policies, assigning responsibilities, setting risk management strategies, and ensuring that leadership has visibility into cybersecurity performance.
Key areas covered under Govern include:
- Organizational context: Understand business objectives, dependencies, and cybersecurity priorities.
- Risk management strategy: Define risk appetite, tolerance, and priorities.
- Roles and responsibilities: Establish clear accountability for cybersecurity decisions.
- Policy and oversight: Create, communicate, and monitor cybersecurity policies.
- Supply chain risk management: Address cybersecurity risks involving suppliers and third parties.
- Enterprise risk alignment: Connect cybersecurity risk decisions with broader organizational risk management.
The Govern function provides the direction that shapes the remaining CSF Functions. It ensures cybersecurity is treated as an ongoing business responsibility rather than only a technical security function.
Identify (ID)
The Identify function helps organizations understand their cybersecurity risk by developing a clear view of their assets, systems, data, services, suppliers, and business environment. This visibility allows security teams to determine where risks exist and which areas require attention.
Organizations use this Function to establish the context needed for effective risk assessment and prioritization. The focus is on understanding what needs protection and how potential risks could affect business operations.
Key areas covered under Identify include:
- Asset management: Identify and manage hardware, software, systems, data, and services.
- Business environment: Understand the organization's mission, objectives, stakeholders, and dependencies.
- Risk assessment: Identify, analyze, and prioritize cybersecurity risks.
- Technology and systems: Maintain visibility into systems and resources that support business operations.
- Suppliers: Understand cybersecurity risks associated with third-party relationships.
- Improvement: Use risk information and lessons learned to improve cybersecurity activities.
Identify provides the foundation for informed security decisions. By understanding the organization's assets, dependencies, and risk exposure, teams can determine where protective controls and other security measures are most necessary.
Protect (PR)
The Protect function focuses on implementing safeguards that reduce cybersecurity risk and limit the impact of potential threats. It turns the organization's understanding of risk into practical security measures that protect systems, data, users, and technology infrastructure.
Protection extends beyond traditional security controls. NIST CSF 2.0 covers access management, security awareness, data protection, platform security, infrastructure resilience, and processes that support consistent cybersecurity operations.
Key areas covered under Protect include:
- Identity and access management: Control access to systems, applications, data, and resources.
- Awareness and training: Equip employees and relevant stakeholders with cybersecurity knowledge.
- Data security: Protect data through appropriate safeguards and data management practices.
- Platform security: Secure applications, operating systems, devices, and technology platforms.
- Technology infrastructure resilience: Maintain systems that can withstand and recover from disruptive events.
- Protective processes: Establish and maintain processes that support reliable security controls.
The Protect function helps organizations reduce the likelihood and impact of security incidents. Its effectiveness depends on how well protective measures address the risks identified through the Identify Function.
Detect (DE)
The Detect function focuses on identifying potential cybersecurity events as early as possible. It helps organizations continuously monitor systems, networks, applications, and user activity so that suspicious behavior can be investigated before it develops into a larger security incident.
Detection is not limited to finding known threats. It also involves analyzing security events and recognizing anomalies that may indicate unauthorized access, malicious activity, or emerging attacks.
Key areas covered under Detect include:
- Continuous monitoring: Monitor networks, systems, applications, and security controls for unusual activity.
- Adverse event analysis: Examine security events to determine their potential impact and significance.
- Anomaly detection: Identify unusual patterns that may indicate a cybersecurity threat.
- Event discovery: Establish processes for detecting cybersecurity events promptly.
- Detection improvement: Use monitoring results and lessons learned to strengthen detection capabilities.
A strong Detect function reduces the time between an attacker gaining access and the organization recognizing the activity. This visibility gives security teams the information they need to initiate an appropriate response.
Respond (RS)
The Respond function defines how an organization takes action after detecting a confirmed or suspected cybersecurity incident. It helps security teams contain threats, understand their impact, communicate effectively, and reduce further damage.
Effective response requires more than reacting when an incident occurs. Organizations should establish documented incident response procedures, assign responsibilities, and ensure teams can coordinate their actions during a security event.
Key areas covered under Respond include:
- Incident response planning: Establish procedures, roles, and resources for handling cybersecurity incidents.
- Incident analysis: Investigate events to understand their scope, cause, and potential impact.
- Incident management: Coordinate technical and organizational actions throughout the response.
- Communications: Share relevant information with internal and external stakeholders when appropriate.
- Mitigation: Contain threats and reduce their immediate and ongoing impact.
- Improvements: Capture lessons from incidents and use them to strengthen response capabilities.
The Respond function connects detection with practical incident response workflows. A well-defined response process helps organizations act quickly while maintaining clear communication and decision-making.
Recover (RC)
The Recover function focuses on restoring systems, services, and operational capabilities after a cybersecurity incident. Its goal is to help the organization return to normal operations while incorporating lessons from the incident into future security improvements.
Recovery should consider both technical restoration and business continuity. Organizations need clear recovery priorities, defined responsibilities, communication processes, and plans for restoring affected resources.
Key areas covered under Recover include:
- Recovery planning: Define strategies and procedures for restoring affected systems and services.
- Restoration: Recover technology, data, applications, and business capabilities based on established priorities.
- Communications: Keep relevant stakeholders informed about recovery progress and service restoration.
- Recovery improvements: Use incident findings and lessons learned to strengthen future recovery efforts.
- Operational resilience: Improve the organization's ability to maintain or restore critical services after disruptions.
The Recover function completes the cybersecurity incident lifecycle. It helps organizations move beyond restoring affected systems by using each incident to improve resilience, recovery processes, and overall cybersecurity risk management.
How do the Six NIST CSF 2.0 Functions Work Together?
The six NIST CSF 2.0 functions operate as a continuous, interconnected ecosystem where enterprise governance guides every technical decision, asset management effort, defensive safeguard, threat detection, incident response, and business recovery action.
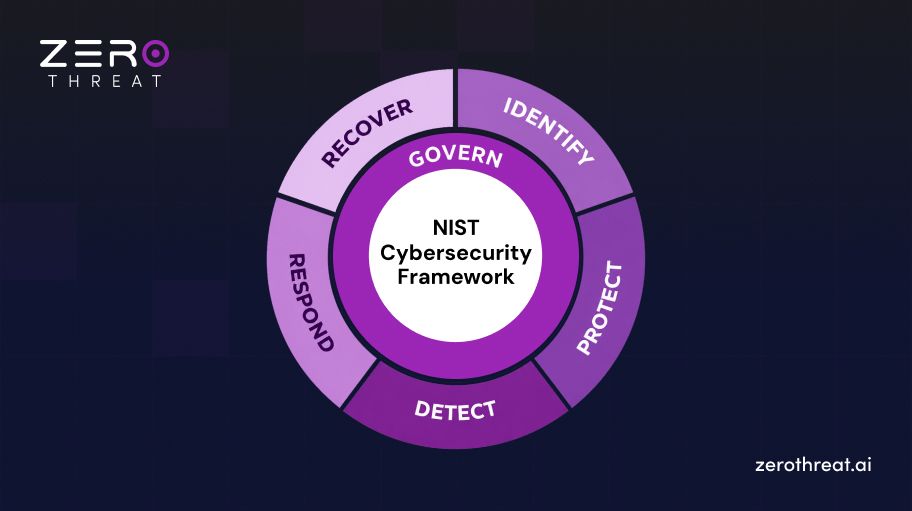
Here is how it works all together:
- Govern sets the risk strategy and policy that shape every decision the other five functions make and enforce daily.
- Identify turns that strategy into an accurate inventory of assets, suppliers, and risks the organization actually needs to manage.
- Protect applies safeguards directly to the assets and risks that Identify surfaced, reducing the chance of a successful attack.
- Detect monitors those protected systems continuously, catching the events that slip past preventive controls before they escalate further.
- Respond activates the moment Detect confirms an incident, containing damage using the plan Govern required teams to prepare.
- Recover restores operations after Respond contains the incident, then feeds lessons learned back into Govern's ongoing risk strategy.
Scale application security testing around your organization's evolving NIST CSF 2.0 requirements. Explore Plans
How to Implement NIST Cybersecurity Framework 2.0?
Implementing NIST CSF 2.0 involves understanding organizational risk, establishing governance, assessing the current cybersecurity posture, and defining the outcomes needed to reach the target state.
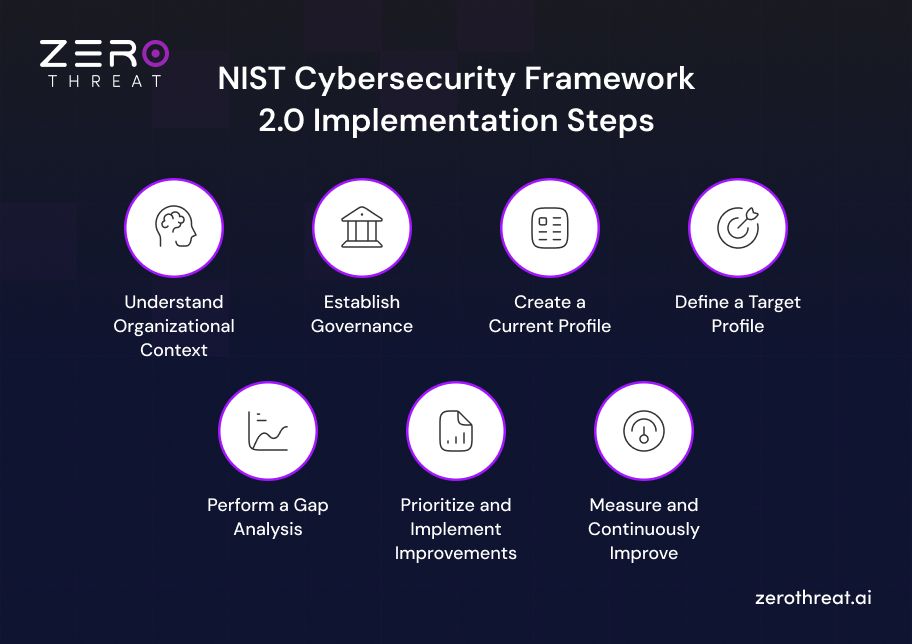
1. Understand Organizational Context
Start by defining the business context that will shape your cybersecurity risk management approach. Identify your organization's mission, business objectives, critical services, stakeholders, regulatory requirements, technology dependencies, and threat landscape.
Also consider:
- Critical business processes and supporting assets
- Internal and external dependencies
- Legal, regulatory, and contractual requirements
- Relevant cybersecurity threats and risks
This context helps determine which CSF 2.0 outcomes matter most to the organization and provides the foundation for creating a risk-informed implementation strategy.
2. Establish Governance
Establish how cybersecurity decisions will be directed, managed, and monitored across the organization. Define cybersecurity roles and responsibilities, risk tolerance, policies, accountability, and oversight mechanisms.
Strong governance should establish:
- Who owns cybersecurity risk decisions
- How risks are evaluated and prioritized
- How cybersecurity aligns with enterprise risk management
- How third-party and supply chain risks are managed
This step gives the implementation clear direction and ensures cybersecurity priorities remain connected to business objectives and leadership expectations.
3. Create a Current Profile
Create a Current Organizational Profile to document the cybersecurity outcomes the organization is achieving today. Assess existing security practices, controls, processes, and capabilities against relevant CSF 2.0 Core outcomes.
Review areas such as:
- Asset and data visibility
- Identity and access controls
- Vulnerability and security monitoring
- Incident response capabilities
- Recovery processes
Document how and to what extent each relevant outcome is currently achieved. This provides a realistic view of the organization's cybersecurity posture and highlights areas requiring improvement.
4. Define a Target Profile
Create a Target Organizational Profile that describes the cybersecurity outcomes the organization wants to achieve. Prioritize outcomes based on business objectives, risk exposure, stakeholder expectations, compliance requirements, and the evolving threat landscape.
The Target Profile should account for expected changes, such as:
- New technologies or business services
- Emerging cybersecurity threats
- New regulatory requirements
- Changes in organizational risk tolerance
Comparing the Current and Target Profiles reveals cybersecurity gaps and helps security teams prioritize actions needed to reach the desired security posture.
5. Perform a Gap Analysis
Compare the Current Profile with the Target Profile to identify gaps between existing cybersecurity capabilities and desired outcomes. Assess where controls, processes, technologies, or resources are insufficient.
Focus on gaps involving:
- Risk management and governance
- Asset and data protection
- Vulnerability and threat detection
- Incident response and recovery
- Third-party and supply chain security
Document each gap, its associated risk, business impact, and current control effectiveness. This creates a practical basis for deciding which cybersecurity improvements require immediate attention.
6. Prioritize and Implement Improvements
Turn identified gaps into a prioritized action plan. Rank improvements according to factors such as cybersecurity risk, business impact, regulatory requirements, available resources, and implementation effort.
Start with actions that address significant risks or critical business dependencies. Assign clear ownership, timelines, required resources, and success criteria to each action.
Implementation may involve strengthening security controls, improving vulnerability management, updating policies, enhancing security monitoring, or improving incident response capabilities. Track progress against the Target Profile to maintain alignment with organizational objectives.
7. Measure and Continuously Improve
NIST CSF 2.0 implementation should be treated as an ongoing process rather than a one-time assessment. Regularly evaluate cybersecurity outcomes, control effectiveness, emerging threats, and changes to business requirements.
Use security metrics and performance indicators to measure progress. Review incidents, assessments, audit findings, and lessons learned to identify areas for improvement.
Update the Current and Target Profiles as the organization's technology, risk environment, and business objectives change. Continuous evaluation helps maintain an effective cybersecurity posture and keeps risk management aligned with evolving threats. (csrc.nist.gov)
Benefits of the NIST Cybersecurity Framework
Adopting the NIST Cybersecurity Framework 2.0 provides organizations with a flexible, risk-informed foundation to strengthen enterprise security posture, streamline regulatory compliance, elevate executive governance, and build long-term operational resilience.
- Unified Security Taxonomy: Establishes a common, non-technical language that bridges the gap between executive boards, technical security teams, and external auditors to streamline risk communication.
- Flexible and Scalable Adaptation: Offers an outcome-driven, vendor-neutral structure that scales seamlessly across organizations of any size, industry sector, or cybersecurity maturity level without imposing rigid controls.
- Simplified Regulatory Mapping: Aligns directly with major compliance frameworks like ISO 27001, SOC 2, HIPAA, and PCI-DSS, drastically reducing redundant audit efforts and control mapping overhead.
- Proactive Enterprise Cyber Resilience: Shifts security operations from reactive firefighting to continuous risk management, ensuring rapid containment, effective incident response, and minimal operational downtime during breaches.
- Enhanced Supply Chain Focus: Strengthens vendor risk governance by providing structured guidelines to identify, monitor, and mitigate third-party software vulnerabilities and external ecosystem threats.
- Optimized Resource Allocation: Enables security leaders to prioritize capital investments and remediation efforts based on measurable business impact, target profile gaps, and validated threat exposure.
How ZeroThreat Can Help with NIST CSF Mapping?
Mapping your security program to NIST CSF 2.0 gets easier when you have continuous, evidence-backed testing behind every function. ZeroThreat provides mapping across your web applications and APIs.
- Identify. ZeroThreat scans your entire application surface automatically, uncovering shadow APIs and forgotten endpoints. This builds an accurate asset inventory that maps directly to CSF's identify function.
- Protect. Authenticated scans test login flows, session handling, and access controls for weaknesses. Findings here map straight to Identify and Access Management, a core category under protect function.
- Detect. Scans run continuously and on every code push, catching new vulnerabilities as they appear. This supports the continuous monitoring outcomes CSF expects under detect function.
- Respond. Each finding comes with proof of exploit, exact request and response data, and clear remediation steps. That evidence maps to the analysis and mitigation outcomes under respond function.
- Recover. Once a fix ships, ZeroThreat automatically retests to confirm the issue is closed. This maps to the restoration and improvement outcomes CSF expects under recover function.
Have questions about mapping ZeroThreat to your CSF profile? Our team is ready to help. Get in Touch
To Wrap Up
NIST CSF 2.0 provides a practical structure for managing cybersecurity risk through Govern, Identify, Protect, Detect, Respond, and Recover. It helps organizations build stronger security practices.
Effective implementation starts with understanding organizational context, assessing the current posture, defining target outcomes, addressing security gaps, and continuously measuring improvement against evolving risks and business needs.
Security testing can strengthen this process by validating application security controls and identifying weaknesses. With ZeroThreat, teams can continuously test web applications and APIs, prioritize vulnerabilities, and strengthen their security posture.
Frequently Asked Questions
Why was Govern added in NIST CSF 2.0?
NIST added Govern to make cybersecurity governance more visible and explicit. CSF 1.1 embedded governance within Identify, while CSF 2.0 gives it a dedicated Function covering risk tolerance, policies, responsibilities, oversight, and enterprise risk alignment.
Is NIST Cybersecurity Framework mandatory?
Who can use NIST CSF 2.0?
How is NIST CSF different from ISO 27001?
What are implementation tiers in NIST Cybersecurity Framework?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.