 ZeroThreat Wins Top InfoSec Innovators 2026 Award for Penetration Testing Read more


All Blogs
What Is Broken Access Control? Common Attacks and Prevention Methods

Quick Overview: Broken access control lets attackers reach data and functions they should never touch. The guide explains what it is, why it happens, and how it affects businesses. It then covers five types with practical examples and eight prevention best practices, from deny-by-default and least privilege to server-side checks, secure tokens, and continuous testing.
Change one number in a URL, and you might be reading someone else’s account.
That’s not a clever hack. It’s broken access control, and it’s what happens when an application checks who you are but forgets to check what you’re allowed to do.
The scale of such vulnerabilities are hard to ignore because, according to OWASP’s 2025 Top 10, broken access control is in the #1 position, and reports that almost 100% of the applications tested had some form of it.
It hides in plain sight, and even the requests appear legitimate. The user is logged in, and nothing seems suspicious until an attack happens. Therefore, using an advanced AI pentesting tool to identify broken access control vulnerabilities, or working with a security testing expert to detect and fix issues is critical for ensuring best security practices.
This guide breaks down the types of broken access control, shows how each plays out, and covers the prevention steps that work. We’ll learn in detail about best practices such as enforcing least privilege, centralizing authorization, and continuous application security testing with monitoring. With that said, let’s get started!
Changing one ID shouldn’t open someone else’s account. Test whether your application holds up. Test My App
On This Page
- What is Broken Access Control?
- What are the Causes Behind Broken Access Control Vulnerabilities?
- Types of Broken Access Control Vulnerabilities
- Broken Access Control Attack Techniques Used by Attackers
- How Does Broken Access Control Impact Businesses?
- How to Prevent Broken Access Control Vulnerabilities: 8 Best Practices
- Wrapping Up
What is Broken Access Control?
Broken Access Control is a security vulnerability that occurs when an application fails to properly enforce what authenticated or unauthenticated users are allowed to see or do. It lets attackers view data, perform actions, or reach functions that were meant for other users or higher-privileged roles.
Access control is the set of rules that decide who can access which resource and what they can do with it. A regular customer should not open an admin panel. One user should not read another user’s invoices. When these rules are missing, incomplete, or enforced in the wrong place, the control is “broken.”
The key distinction is between two ideas that are often confused. Authentication verifies who the user is. Authorization (access control) determines what that verified identity is permitted to access. An application can authenticate users perfectly and still expose everything if its authorization checks are weak.
Here is a simple scenario. A user logs in and opens /api/orders/1042 to view their order. If the server returns order 1043, which belongs to someone else, when the user changes the number in the request, the server never checked ownership. That missing check is broken access control.
These flaws usually trace back to a few causes:
- Authorization checks missing on some endpoints or functions
- Permissions enforced only in the front end, where users can bypass them
- Trust placed in user-controlled values such as IDs, cookies, tokens, or hidden fields
- Inconsistent rules applied across pages, APIs, and roles
Depending on what is exposed, the impact ranges from unauthorized data access to privilege escalation, data modification or deletion, and full account or system takeover. OWASP ranks Broken Access Control as the number one risk in the OWASP Top 10:2025, holding the top position from the 2021 edition. The 2025 list also merged Server-Side Request Forgery (SSRF) into this category.
What are the Causes Behind Broken Access Control Vulnerabilities?
Broken access control vulnerability can occur due to many reasons. Knowing these reasons is helpful in understanding how this vulnerability manifests in your system to take appropriate measures to eliminate the potential risks.
Broken Authorization
An authorization mechanism helps restrict users from accessing what they are not permitted to. What if this mechanism is not properly implemented? In that case, an unauthorized user can access data or functionality that only users with higher privileges are entitled to.
For example, a user is able to access a dashboard functionality that is intended for admins by manipulating the URL. As a result, the user is able to modify, delete, or add data. This kind of authorization flaw causes broken access control vulnerability.
An attacker can take advantage of this flaw to manipulate or exfiltrate sensitive data. The attacker can act as a legitimate user when accessing unauthorized functionality or data.
Broken Session Management
Session management is a crucial function of web applications that manage a user’s data and state across multiple requests. When it is implemented improperly, it leads to broken access control causing serious security risks for your data and assets.
Broken session management can allow an attacker to take over a user’s session. It is known as session hijacking, it enables the attacker to perform unauthorized actions and pose as a legitimate user. There can be various reasons for improper session management like predictable session IDs, lack of session termination, session IDs, or tokens visible in URLs.
This security flaw welcomes various risks like privilege escalation, data breaches, and unauthorized access to sensitive data.
Broken Authentication
When a web application fails to validate users accessing protected resources or data properly, it is referred to as broken authentication. An attacker can exploit this type of security flaw to access protected data and resources.
Authentication is an important security layer in an access control mechanism that ensures that only users with valid credentials are able to access data and resources. As a result, it prevents the possibility of an attacker trying to access protected data and resources.
An example of this security flaw is related to JWT (JSON Web Tokens), which is used in web applications to authenticate users. The attacker can alter the signed algorithm of the token in case of a weak mechanism to bypass authentication and access protected information.
Manual pentests happen occasionally. Your roles and permissions change constantly. Use AI pentesting to test them continuously. Run AI Pentesting
Types of Broken Access Control Vulnerabilities
Broken access control vulnerabilities fall into five main types: vertical privilege escalation, horizontal privilege escalation, missing function-level access control, context-dependent access flaws, and token or metadata manipulation. The first two describe what an attacker gains. The other three describe how the access check fails.
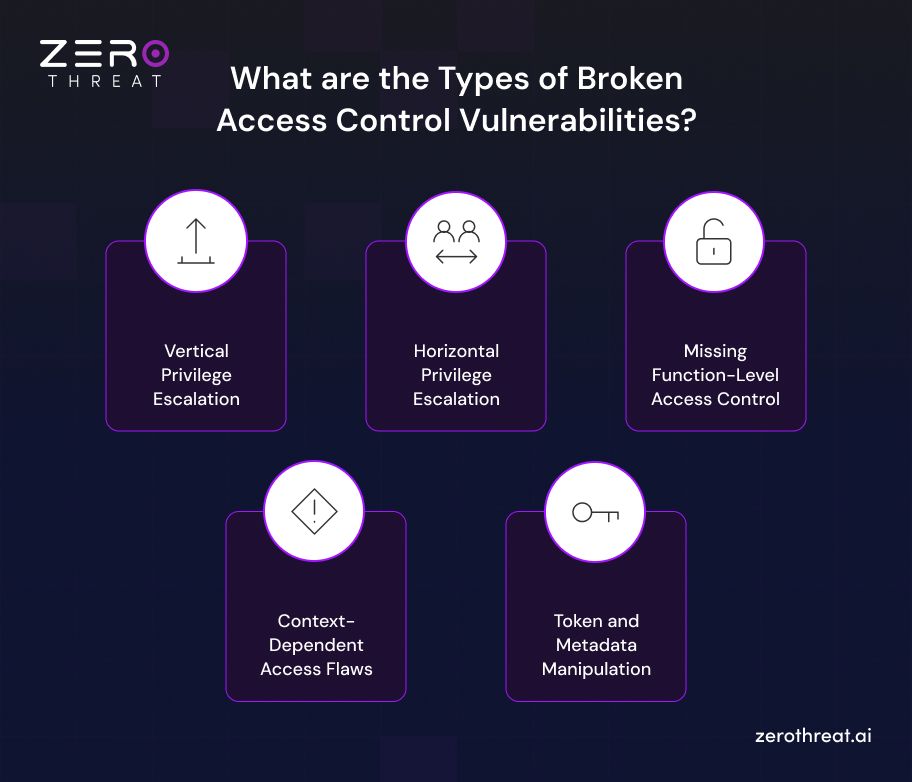
Vertical Privilege Escalation
Vertical privilege escalation occurs when a user gains access to functions or data reserved for a higher role, such as a standard user performing administrator actions. It usually results from weak or missing role checks. The impact tends to be broad because elevated roles typically manage users, settings, and data across the application.
Horizontal Privilege Escalation
Horizontal privilege escalation occurs when a user accesses resources that belong to another user at the same privilege level, such as viewing someone else’s invoice by changing an ID in the request. In web applications, this is known as Insecure Direct Object Reference (IDOR). In APIs, the same pattern is called Broken Object Level Authorization (BOLA). The cause is a missing ownership check on the requested object.
Missing Function-Level Access Control
This type occurs when an application protects data but not the functions that act on it. Administrative endpoints, unlinked URLs, and methods such as POST, PUT, or DELETE stay reachable by users who should not call them. Attackers find them through forced browsing or path guessing. In APIs, this is called Broken Function Level Authorization (BFLA). Vertical escalation describes the outcome, and a missing function-level check is one of the most common ways it happens.
Context-Dependent Access Flaws
Some access rules depend on the state of a workflow, not just the user’s role. Context-dependent flaws let users skip steps or act out of sequence, such as reaching an order confirmation page without completing payment or editing a record after it should be locked. Each request may look valid on its own, so checks tied only to roles miss these flaws.
Token and Metadata Manipulation
Here, attackers alter the data an application uses to make access decisions, such as a JSON Web Token (JWT), a cookie, or a hidden form field. Changing a role value from user to admin, replaying an old token, or exploiting weak token validation can raise privileges. It works when the server trusts client-held data without verifying it.
Broken Access Control Attack Techniques Used by Attackers
There are many techniques that attackers can use to exploit broken access control vulnerabilities and steal data. Understanding these techniques is vital to build stronger defenses and prevent potential attacks. So, let’s check these techniques below.
Privilege Escalation
Attackers can use the privilege escalation technique to exploit weak access controls. It can be divided into two – horizontal escalation and vertical escalation. In the case of a horizontal privilege escalation, an attacker exploits authorization and session vulnerabilities to take access privileges to the same level as another user.
On the other hand, vertical privilege is a technique in which the attacker tries to access resources or data that are accessed by users with higher privileges.
Manipulate Parameters
Attackers can sometimes trick an application into granting access by tweaking URL parameters and form field values. With this technique, they can bypass the access control mechanism to obtain data. For example, a vulnerable website uses an ID parameter in its URL structure to provide information about a specific user. The attacker can manipulate this parameter to reveal information about other users.
Exploit API Endpoints
Another technique to exploit broken access control is abusing APIs. When APIs are not properly secured, they become an easy target for attackers. They can tamper with the inputs or API endpoints to perform unauthorized actions or gain access to data.
Misconfigurations
Attackers can also take advantage of misconfigurations that inadvertently expose sensitive data in public URLs. Misconfigurations can reveal sensitive information that can allow an attacker to obtain access to sensitive data.
Catching access flaws early beats cleaning up after a breach. Compare plans for continuous testing. Explore Pricing Plans
How Does Broken Access Control Impact Businesses?
Broken access control hurts a business by exposing sensitive data, allowing unauthorized actions, and creating financial, legal, and reputational fallout. The flaw lets attackers act like legitimate users, so their requests often look like normal activity. That means damage can build quietly before anyone notices. The impact usually shows up in five ways.
Data Exposure and Privacy Breaches
The most direct impact is unauthorized access to information. Customer records, employee files, financial data, and internal documents can all be exposed when ownership checks are missing. A single IDOR flaw can also be automated, so an attacker who finds it can often pull every record, not just one.
Data Tampering and Disruption
Access control failures are not only about reading data. Attackers who reach write or admin functions can change or delete records, alter account settings, or lock real users out. Tampering is harder to spot than theft, and it can leave teams unsure which data they can still trust.
Financial Loss and Fraud
Money is lost in more than one place. Attackers can manipulate prices, refunds, or transfers, or take over accounts. Then come the costs of investigation, remediation, legal support, and customer notification, plus any downtime. Those response costs add up quickly and can continue long after the vulnerability is fixed.
Regulatory and Compliance Penalties
Regulations expect organizations to restrict access to sensitive data. GDPR covers personal data, HIPAA covers health information, and PCI DSS covers cardholder data. A breach caused by missing authorization checks invites regulatory scrutiny, and GDPR fines can reach €20 million or 4% of global annual turnover, whichever is higher, for the most serious violations.
Loss of Customer Trust
Breach notification rules mean affected customers usually hear about it. Some leave. Business customers may pause deals or ask for security reviews before renewing. Because access control flaws are preventable, they are hard to explain away, and that makes the reputational damage harder to contain.
How to Prevent Broken Access Control Vulnerabilities: 8 Best Practices
Preventing broken access control comes down to enforcing authorization on the server for every request, denying access unless it is explicitly granted, and verifying those rules through testing and monitoring. The eight practices below move from design principles to implementation, configuration, and ongoing verification.
1. Deny Access by Default
Start with a policy where every resource is off limit unless a rule explicitly allows it. New endpoints, roles, and features then inherit protection automatically, instead of depending on a developer remembering to add a check at the right moment.
Treat public resources as deliberate exceptions and review that list regularly. Under allow-by-default, a missed rule leaves a door open. Under deny-by-default, a missed rule produces an error that someone notices and fixes during development or testing.
2. Enforce Least Privilege
Give every user, role, and service account only the permissions needed for its job, and nothing more. Broad roles such as a catch-all admin make it easy to ship quickly, but they turn any single flaw into a much larger problem.
Map permissions to real business functions, using role-based access control (RBAC) or attribute-based access control (ABAC) where rules depend on context such as ownership or department. Review roles periodically, because permissions tend to accumulate as people change teams.
3. Enforce Checks Server-Side
Run every access decision in trusted server-side code, where attackers cannot alter the logic or the data it relies on. Hiding buttons or menu items improves usability, but it does not stop anyone from sending the underlying request directly.
Make sure the check runs on every request, including API calls, background jobs, and requests that arrive through alternate HTTP methods. Derive the user’s identity and permissions from the server-side session or verified token, never from a value the client supplies.
4. Centralize Authorization Logic
Build access control once and reuse it across the application, ideally through middleware, a policy engine, or a shared authorization service. Scattered checks in individual handlers drift apart over time, and the one that gets skipped becomes the vulnerability.
A central layer also makes rules easier to audit and change. When a permission model shifts, one update applies everywhere, and reviewers can read the policy in one place instead of tracing logic through dozens of controllers and services.
5. Verify Object and Function Access
Check that the requesting user is allowed to access the specific record, not just the type of record. Object-level checks stop IDOR and BOLA flaws, where changing an ID in a request returns another user’s data.
Query data in the context of the authenticated user, for example by filtering on the owner ID, and check permissions on sensitive actions such as delete or export. Unpredictable identifiers such as UUIDs add friction, but they are a supplement to ownership checks, never a replacement.
6. Secure Tokens and Sessions
Validate every token on the server: check the signature, expiry, issuer, and audience, and never accept role or permission claims the server has not verified. Reject unsigned tokens and unexpected signing algorithms, which are common routes to JWT tampering.
Keep access tokens short-lived and invalidate sessions on logout, password change, and role change. OWASP calls out JWT invalidation as a weak spot, since a stolen or outdated token can otherwise keep working after access should have ended.
7. Harden Access-Related Configuration
Scope CORS to the specific origins that need access, and never reflect arbitrary origins on credentialed requests. Disable directory listing, keep backup and metadata files out of web roots, and make sure admin interfaces are not reachable from the public internet.
Apply rate limits to APIs and sensitive endpoints, which slows automated attempts to enumerate IDs or probe for unprotected routes. Review configuration across environments, since a setting that is locked down in staging can quietly be left open in production.
8. Test and Monitor Continuously
Include access control in unit and integration tests, and test what should fail as carefully as what should work. Try each role against each sensitive endpoint, attempt cross-user and cross-tenant access, and confirm the application returns the right denial.
Add AI penetration testing to CI/CD, supported by manual review for context-dependent logic that automated tools can miss. Log access control failures and alert on patterns, such as one account hitting many forbidden endpoints, so attacks surface early.
Prevention checklist done? Put it to the test with ZeroThreat and see what still slips through. Test My Defenses
Wrapping Up
Broken access control can potentially make the path clear for attackers to manipulate sensitive data. One of the prime examples is OWASP broken access control vulnerability that causes unauthorized access to restricted data. We hope you can overcome these significant security threats with the defensive security measures we have curated for you in this article.
Apart from following these security practices, you can operate reliable security tools like ZeroThreat if you want to experience hands-on the best security scanning for your web apps and APIs in minutes. Try it out for free to experience how fast and accurately it helps you optimize vulnerability detection.
Frequently Asked Questions
Is broken access control a serious threat?
Yes. OWASP ranks broken access control #1 in its 2025 Top 10. A single flaw can expose sensitive data, let attackers modify or delete records, or grant admin privileges. Because requests often look like normal user activity, these attacks can go unnoticed for long periods.
How can I protect myself from broken access control attacks?
How to determine broken access control vulnerabilities?
What are common broken access control vulnerabilities?
Can broken access control be exploited offline?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.