 ZeroThreat Wins Top InfoSec Innovators 2026 Award for Penetration Testing Read more


All Blogs
Quick Overview: This blog explains how to secure Node.js applications. It covers why Node.js needs dedicated security practices, the key risks developers face, and 11 practical best practices, from input validation and injection prevention to authentication, access control, secure headers, secrets management, and continuous testing. It also highlights common mistakes to avoid and answers frequently asked questions.
Node.js is a shining star in backend development since it's a favorite choice for many developers. It is used by many global giant companies like Netflix, LinkedIn, and PayPal. According to Statista’s developer survey, it is the most used web framework, securing the first position.
But being popular also means it is on the hit list of attackers. While Node.js is secure by design, the additional packages used through NPM can introduce vulnerabilities. These vulnerabilities can allow an attacker to compromise the security of Node.js applications.
You can protect your Node.js applications by following below best practices. These practices will help you prevent security loopholes that could put your applications at risk. Keep reading to know these best practices and elevate your security posture.
Don't let attackers find your injection flaws first. Scan your Node.js app with ZeroThreat today. Automate My Pen Tests
Table of Contents
- Why Node.js Applications Need Dedicated Security Practices?
- Key Security Risks in Node.js Applications
- Best Practices to Secure Your Node.js Applications
- Common Node.js Security Mistakes to Avoid
- Wrapping Up
Why Node.js Applications Need Dedicated Security Practices?
Node.js applications need dedicated security practices because the runtime combines a single-threaded event loop, a deep npm dependency chain, and server-side JavaScript with direct access to the host system. General web security advice still applies, but it does not account for how these traits change what an attacker can reach and how far one flaw can spread.
Four characteristics set Node.js apart:
- A single-threaded event loop: One thread handles incoming requests. A slow operation, such as an expensive regular expression or a large synchronous task, can stall the entire process. A single crafted request can then degrade the service for every user.
- Heavy reliance on npm: Even a simple Express app can pull in dozens or hundreds of transitive packages that nobody on the team has reviewed. Each one runs with the application's privileges, and install scripts can execute code on developer and build machines at install time.
- Dynamic typing and flexible objects: JavaScript does not enforce the shape of incoming data. An API that expects a string can receive an object instead. Without strict validation, that opens the door to NoSQL operator for injection and prototype pollution.
- Broad access to the host: Server-side JavaScript can read files, spawn processes, and access environment variables that often hold secrets. Passing unsafe input to eval() or child_process.exec() can turn a coding mistake into full server compromise.
Frameworks widen the gap. Express and other minimal frameworks leave security headers, input validation, authentication, and rate limiting to the developer. Protection exists only if the team builds it in.
The practical point is that Node.js security depends on decisions made across code, dependencies, and runtime configuration, not on a single control. The next section breaks down the specific risks that follow from these traits.
Key Security Risks in Node.js Applications
Most security risks in Node.js applications come from unvalidated input, untrusted dependencies, weak access controls, and a single thread that is easy to overload. The key risks are:
- Injection attacks: Unsanitized input can reach SQL queries, NoSQL operators, or shell commands. Attackers use this to steal data, bypass logins, or run arbitrary commands on the host server.
- Vulnerable and malicious dependencies: Third-party npm packages can carry known flaws, hijacked code, or typosquatted names. One compromised package, direct or transitive, can expose the entire application and its build pipeline.
- Prototype pollution: Unsafe merges of user-controlled objects let attackers modify Object.prototype. Injected properties spread to every object in the process, enabling denial of service, logic bypass, or privilege escalation.
- ReDoS and event loop blocking: Poorly written regular expressions or heavy synchronous tasks block the single-threaded event loop. One crafted request can freeze the application and make it unavailable to every user.
- Broken authentication: Weak password handling, insecure JWT configuration, and poor session management let attackers impersonate users. Causes include missing token expiry, unverified tokens, and predictable or long-lived session identifiers.
- Broken access control: Routes that check login but not permissions let users reach other accounts' data or admin functions. Missing server-side object-level and role checks are a frequent root cause.
- Security misconfiguration and exposed secrets: Missing security headers, permissive CORS, and verbose errors leak details to attackers. Hardcoded credentials in code or repositories can give direct access to databases and cloud services.
Harness the power of automated scanning to uncover Node.js vulnerabilities. Hunt Them Now
Best Practices to Secure Your Node.js Applications
The security practices below focus on controls that Node.js teams can implement directly in code and configuration.
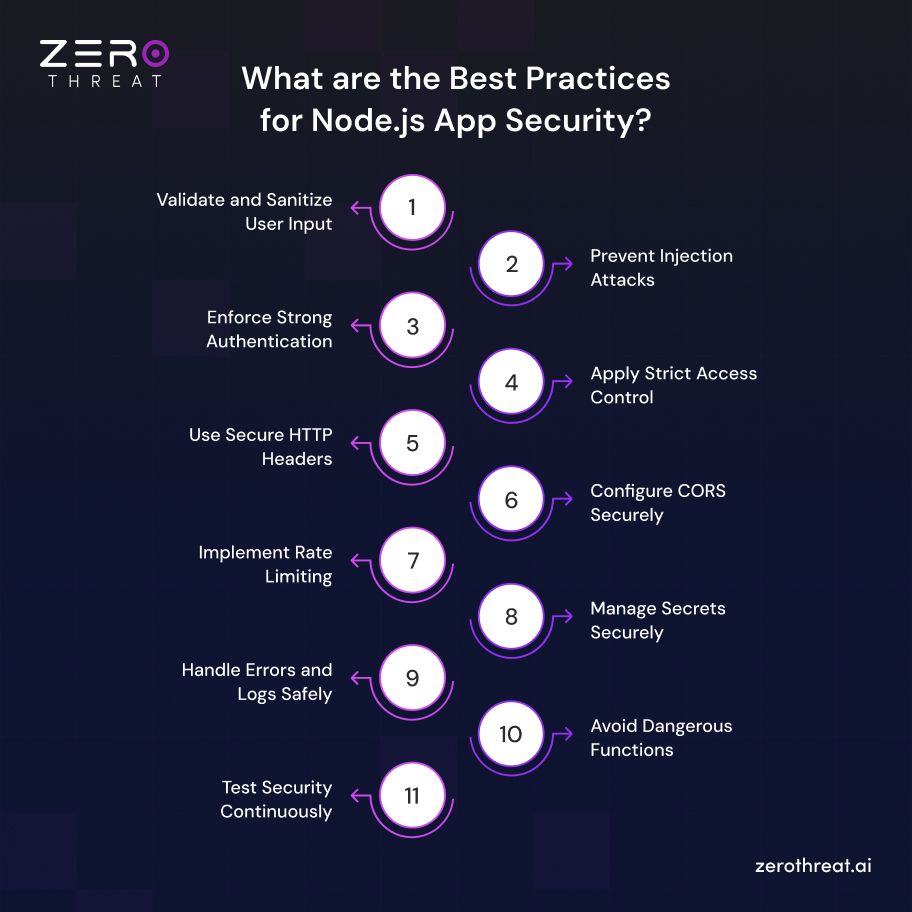
1. Validate and Sanitize User Input
Treat every value in a request, including body, query, params, headers, and cookies, as untrusted. Validate it against a strict schema at the route entry and reject anything that does not match.
- Use a schema library such as Zod, Joi, or Ajv to enforce type, length, and format.
- Allowlist expected fields and drop unknown ones.
- Escape output for its context, such as HTML or URLs.
Tip: Cap request size with express.json({ limit: '100kb' }), and confirm fields are strings before use, since attackers can send objects where strings are expected.
2. Prevent Injection Attacks
Never build queries or commands by joining strings with user input. Pass input as data, separate from the instruction, so the interpreter cannot treat it as code.
- SQL: Use parameterized queries or an ORM's bound parameters, for example WHERE id = $1.
- MongoDB: Validate types and strip keys starting with $ to block operator injection such as {"$ne": null}.
- OS commands: Prefer execFile() with an argument array over exec(), and avoid eval() entirely.
Tip: Add eslint-plugin-security to the lint step so unsafe eval and child_process usage fails the build before code review.
3. Enforce Strong Authentication
Authentication usually breaks through weak password storage and loosely configured tokens. Use a vetted library or identity provider instead of building login logic from scratch.
- Hash passwords with Argon2id or bcrypt, never plain SHA-256.
- Issue short-lived access tokens and rotate refresh tokens.
- Verify JWT signature, algorithm, issuer, audience, and expiry on every request.
- Store session tokens in HttpOnly, Secure, and SameSite cookies.
- Require MFA for admin accounts.
Tip: Return the same generic error for a wrong username and a wrong password, and rate limit login attempts to slow credential stuffing.
4. Apply Strict Access Control
Authentication proves who the user is. Access control decides what that user can do. Enforce it on the server for every request, because hiding buttons in the UI protects nothing.
- Deny by default and grant permissions explicitly.
- Check ownership on every object ID, not just the user's role.
- Centralize checks in middleware or policy layer.
- Give database accounts and service tokens with the least privilege.
Tip: A route like GET /orders/:id must confirm the order belongs to the caller. Write tests that request user B's IDs as user A and run them in CI.
5. Use Secure HTTP Headers
Security headers instruct browsers to block attacks such as XSS, clickjacking, and protocol downgrades. The Helmet middleware sets a solid baseline with app.use(helmet()) and removes the X-Powered-By header that reveals Express. Tune the CSP to your frontend, since defaults can break inline scripts.
- Strict-Transport-Security forces HTTPS.
- Content-Security-Policy restricts script sources and limits XSS impact.
- X-Content-Type-Options: nosniff stops MIME sniffing.
- frame-ancestors in the CSP blocks clickjacking.
Tip: Roll out CSP with Content-Security-Policy-Report-Only first to catch broken scripts, then switch to enforcement. Verify the final headers with curl -I.
6. Configure CORS Securely
CORS decides which browser origins can read responses from your API. Calling cors() with defaults, or setting origin: '*', lets any website talk to your backend.
- Allowlist exact origins, such as
https://app.example.com. - Never reflect the request's Origin header back without checking it.
- Do not combine credentials: true with a wildcard origin.
- Limit allowed methods and headers to what the frontend uses.
Tip: Load the allowlist from environment config so staging origins never reach production. CORS only governs browsers, so it does not replace authentication.
7. Implement Rate Limiting
Without request limits, attackers can brute-force logins, scrape data, or flood endpoints to exhaust the event loop. Add limits to the app layer, even if a gateway or WAF sits in front.
- Use express-rate-limit or @fastify/rate-limit globally.
- Apply stricter limits to login, password reset, and OTP routes.
- Set trust proxy correctly, or every user behind a load balancer shares one IP.
- Use a Redis store when running multiple instances.
Tip: Return 429 with a Retry-After header and set request timeouts and body size limits to stop slow-request attacks.
8. Manage Secrets Securely
API keys, database credentials, and JWT signing keys should never live in source code. A secret pushed to a repository should be treated as compromised, even if the repo is private.
- Add .env files to .gitignore.
- Load secrets at runtime from a secrets manager such as HashiCorp Vault or AWS Secrets Manager.
- Use separate secrets for each environment and rotate them regularly.
- Scan commits with Gitleaks in a pre-commit hook and in CI.
Tip: If a secret is committed, rotate it immediately. Removing it from Git history does not undo the exposure.
9. Handle Errors and Logs Safely
Detailed errors help attackers map your stack, database, and file paths. Show users a generic message and keep the details in your logs.
- Set NODE_ENV=production so Express stops returning stack traces.
- Use one central error-handling middleware for consistent responses.
- Use a structured logger such as Pino or Winston, and redact fields like authorization, passwords, and tokens.
- Log security events: failed logins, access denials, and validation failures.
Tip: Return a request ID in error responses. Support teams can then find the exact log entry without exposing internals to the user.
10. Avoid Dangerous Functions
Some Node.js features turn untrusted input into code execution or file access. Remove them from request-handling paths or wrap them in strict control.
- Avoid eval() and new Function() on any external data.
- Do not treat the vm module as a security sandbox.
- Use execFile() with an argument array instead of exec().
- Resolve user-supplied file paths and confirm they stay inside an allowed base directory to prevent path traversal.
Tip: Enable ESLint rules such as no-eval, no-new-func, and security/detect-child-process so risky code fails in CI.
11. Test Security Continuously
One-time audits go stale as soon as new code ships. Build testing into the development cycle, so each release is checked against both known vulnerabilities and real attack behavior.
- Run npm audit or an SCA tool on every pull request.
- Add SAST to catch insecure code patterns early.
- Run dynamic tests against a staging build, not just source code.
- Retest after every fix to confirm the issue is closed.
Tip: Use ZeroThreat to run AI-powered automated penetration tests against your Node.js web app and APIs after major releases, then verify fixes with a follow-up scan.
Common Node.js Security Mistakes to Avoid
Most Node.js breaches trace back to a handful of avoidable habits. These are the five that show up most often in real applications.
1. Trusting User Input Blindly
Passing request data straight into queries, commands, or file paths is the fastest route to injection. Client-side checks are easy to bypass. Validate every field on the server against a strict schema before the data touches any logic.
2. Installing Dependencies Without Checking
Adding npm packages without checking maintainers, downloads, or known vulnerabilities invites supply chain attacks. Skipping lockfiles and updates makes it worse. Commit your lockfile, use npm ci in builds, update packages regularly, and run audits on every pull request.
3. Hardcoding Secrets in Code
API keys and database passwords pushed to Git stay exposed, even after deletion, because history and forks keep copies. Store secrets in a secrets manager or environment variables, and immediately rotate any key that was ever committed.
4. Leaking Detailed Error Messages
Stack traces and raw database errors reveal frameworks, file paths, and query structure to attackers. Return a generic message with a request ID to the client, and keep full details in protected server logs. Set NODE_ENV to production as well.
5. Running with Excess Privileges
Running Node.js as root, or with broad cloud and database permissions, turns any exploit into full compromise. Use a non-root user in containers, grant least-privilege access, and limit what the process can reach on the network.
Curious how AI-powered pentesting fits your Node.js workflow? Sign up and explore now! Start Your Free Trial
Wrapping Up
Companies have suffered significant losses due to cybersecurity incidents over the years. Mostly, these incidents occur due to vulnerabilities like ticking bombs that can burst at any time. Therefore, a proactive approach to identifying and resolving these vulnerabilities can help you defend against these threats.
Similarly, you can protect your Node.js applications by uncovering hidden vulnerabilities. You can use ZeroThreat’s advanced Node.js vulnerability scanner to discover even hard-to-detect vulnerabilities. It can help you scan your Node.js applications deeply and detect vulnerabilities.
Frequently Asked Questions
Does Node.js have vulnerabilities?
Yes. Like any runtime, Node.js has had CVEs, and the Node.js project publishes regular security releases to patch them. Most real-world risk comes from application code and npm dependencies, so keep Node.js on a supported LTS version and update packages.
Is Node.js hackable?
How to improve Node.js security?
What are the top tools to enhance Node.js security?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.