 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs
Cryptographic Failures: Understanding Impact and Tips to Prevent

Quick Summary: Cryptographic failures can put sensitive data at risk when encryption and other security controls are poorly implemented. This blog explains what cryptographic failures are, their common causes, and their impact on applications and users. It also covers practical best practices to prevent them and how ZeroThreat helps identify and fix cryptographic weaknesses through security testing.
In this tech-first world, organizations highly depend on digital systems. This excessive dependence makes them susceptible to cyberattacks. In most cases, cyberattacks occur due to poor security practices and vulnerabilities that make your systems prone to such risks.
Thus, identifying and fixing vulnerabilities is vital in securing your digital landscape. One of the most critical vulnerabilities is cryptographic failure. It is listed as a critical vulnerability in OWASP Top 10 security risks.
It is a security weakness that arises due to improper use of cryptography - a technique used to protect data by coding it in an unreadable format. Cryptography eliminates the risks associated with transferring and storing data in plain text.
Like other vulnerabilities, identifying and resolving cryptographic failure vulnerabilities is crucial to ensure the security of your web app. Failing to resolve this vulnerability leads to various security issues. Most importantly, it will leave your data unprotected and could be easily stolen or compromised.
In this article you can learn more about cryptographic failures, their impact, best practices to tackle them and how ZeroThreat's AI-driven automated pentesting tool can help you detect and fix cryptographic failures and other vulnerabilities.
Stop cryptographic flaws before attackers exploit them. Start scanning your apps for free. Test Your App Free
Table of Contents
- What Are Cryptographic Failures?
- What are the Causes of Cryptographic Failures?
- Real-World Examples of Cryptographic Failures
- What are the Impacts of Cryptographic Failures?
- Best Practices to Prevent Cryptographic Failures
- How ZeroThreat Helps You Identify and Fix Cryptographic Failures
- To Wrap Up
What are Cryptographic Failures?
A cryptographic failure occurs when an application does not properly use cryptography to protect sensitive information. It can happen when encryption is missing, weak algorithms are used, or security controls are implemented incorrectly, leaving protected data exposed to unauthorized access.
The problem can affect data both at rest and in transit. For example, an application may store sensitive records securely but transmit them without adequate encryption, or use outdated protocols that attackers can exploit. Passwords, payment details, personal information, and business data are common targets.
Cryptographic failures are also closely linked to how keys and other cryptographic material are managed. Exposed keys, hardcoded secrets, weak key generation, key reuse, and poor rotation practices can undermine otherwise strong encryption. NIST emphasizes protecting keys throughout their lifecycle, from generation and storage to use and destruction.
In practice, cryptographic security is not simply about choosing a strong encryption algorithm. Developers must also select secure protocols, generate unpredictable values, protect cryptographic keys, and apply encryption where it is required. When these safeguards fail, attackers may gain access to sensitive information that the application was designed to protect.
What are the Causes of Cryptographic Failures?
Cryptographic failures often result from weak algorithms, poor key management, insecure protocols, or incorrect implementation. Understanding these common causes helps security teams identify weaknesses before attackers can exploit exposed or poorly protected data.
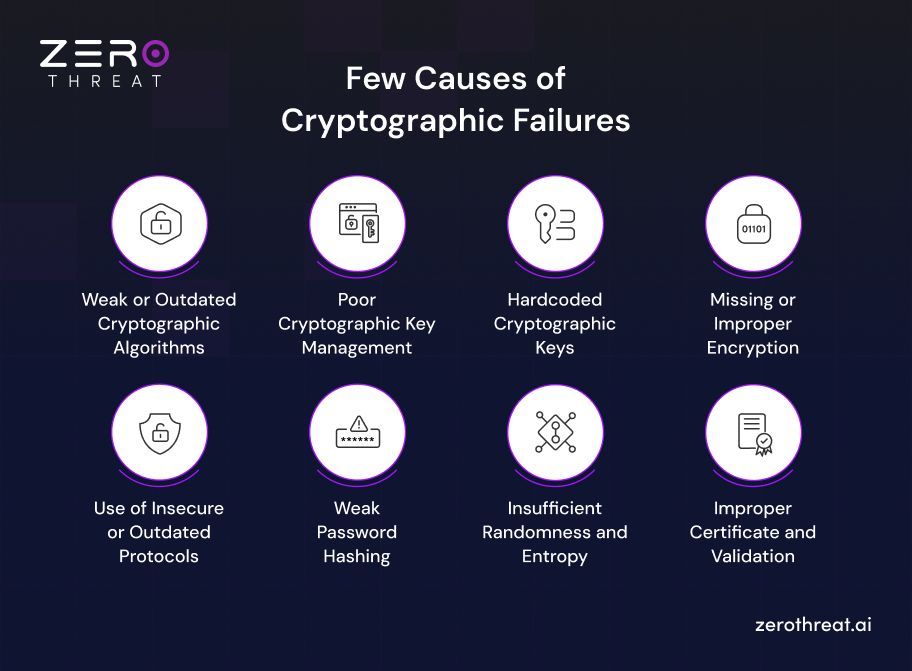
Weak or Outdated Cryptographic Algorithms
Using broken, deprecated, or insufficiently strong algorithms can make protected data easier to compromise. Legacy algorithms and weak cryptographic parameters may no longer provide adequate resistance against modern attacks, especially when stronger standards are available.
Poor Cryptographic Key Management
Encryption becomes ineffective when cryptographic keys are generated, stored, distributed, or rotated improperly. Exposed keys, excessive access permissions, reused keys, or missing key rotation can allow attackers to bypass otherwise strong encryption controls.
Hardcoded Cryptographic Keys
Embedding encryption keys directly in source code, configuration files, or application binaries creates a serious security risk. Attackers who gain access to the codebase can extract these keys and potentially decrypt sensitive information or impersonate trusted systems.
Missing or Improper Encryption
Sensitive information that is stored or transmitted without appropriate encryption can be exposed to unauthorized parties. This includes credentials, payment information, personal data, and business records that require protection both at rest and in transit.
Use of Insecure or Outdated Protocols
Legacy communication protocols or improperly configured TLS can expose data to interception, downgrade attacks, and tampering. Applications should enforce modern, secure transport protocols rather than relying on outdated configurations that no longer provide adequate protection.
Weak Password Hashing
Storing passwords with fast, unsalted, or outdated hashing methods makes them easier to crack after a database compromise. Secure password storage requires adaptive, salted password-hashing algorithms designed to make offline brute-force attacks significantly more difficult.
Insufficient Randomness and Entropy
Cryptographic operations depend on unpredictable values for keys, tokens, nonces, and initialization vectors. Using predictable random number generators, weak seeds, or insufficient entropy can make these values guessable and weaken the security of otherwise sound cryptographic mechanisms.
Improper Certificate and Validation
Failing to properly validate certificates, certificate chains, digital signatures, or other cryptographic operations can allow attackers to impersonate trusted services or tamper with data. Security controls must verify cryptographic trust rather than simply assuming a connection or signature is valid.
Uncover weak encryption and authentication flaws hiding inside your web application with 99.99% accuracy. Test Application Risk
Real-World Examples of Cryptographic Failures
There are many organizations that have gone through a security breach due to failed cryptographic measures. The following are cases for two of those companies.
Yes, you read it correctly. Facebook is among the companies that have faced cryptographic failure. In pre-Covid-19 time, it was reported that over 540 million records of Facebook users were revealed. These records included IDs, photos, location information, passwords, and other information related to Facebook users. This incident occurred because of an accidental leak of data by two third-party apps. These applications stored the data of Facebook users on Amazon cloud services without any encryption. Consequently, the data of Facebook users was revealed unintentionally.
Exactis
In another case, a small data aggregation and marketing firm, Exactis, accidentally revealed data of more than 340 million individuals. The database was put on a public server that could be easily accessed by a non-authorized party. However, this incident could have been prevented, had they used encryption and avoided using a public server. The data exposed in this data breach incident included phone numbers, names, emails, and other information of US citizens.
What are the Impacts of Cryptographic Failures?
Cryptographic failures can expose sensitive data, weaken authentication, and allow attackers to intercept or manipulate protected information, creating serious security, privacy, financial, and compliance risks.
- Sensitive Data Exposure: Weak or missing encryption can expose credentials, financial records, personal information, health data, and confidential business information to unauthorized users.
- Credential and Session Theft: Poor encryption during transmission can allow attackers to intercept passwords, session cookies, or authentication tokens and use them to access legitimate user accounts.
- Data Tampering: Cryptographic weaknesses can affect data integrity, allowing attackers to modify information in transit or manipulate protected data without proper detection.
- Account Takeover: Compromised credentials, session tokens, or authentication keys can help attackers bypass security controls and gain unauthorized access to user or administrative accounts.
- Financial Loss: Exposed payment information, business secrets, or compromised transactions can result in fraud, financial losses, incident response costs, and operational disruption.
- Compliance and Privacy Violations: Exposure of regulated or personally identifiable information can trigger privacy concerns, regulatory penalties, contractual consequences, and additional requirements for breach response.
- Loss of Trust: A cryptographic failure that exposes customer or business data can damage an organization's reputation and reduce customer confidence in its security practices.
- Broader Security Compromise: A compromised cryptographic key can affect the confidentiality, integrity, authentication, or non-repudiation of information protected with that key, potentially expanding the scope of an attack.
Best Practices to Prevent Cryptographic Failures
Preventing cryptographic failures requires more than choosing a strong encryption algorithm. Organizations should protect sensitive data, manage cryptographic keys securely, use modern protocols, and regularly verify cryptographic configurations.
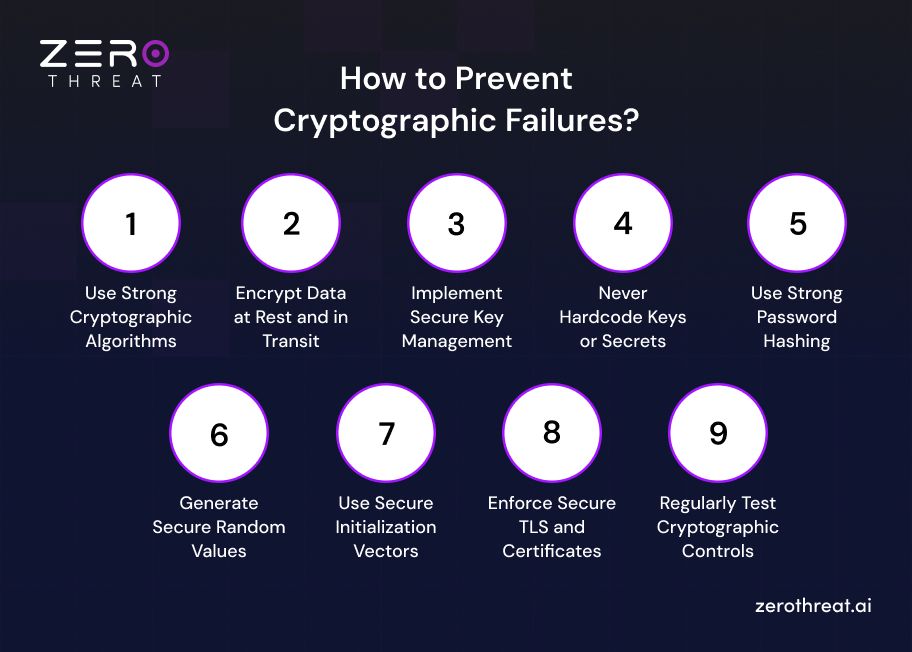
Use Strong Cryptographic Algorithms
Choose well-established cryptographic algorithms, appropriate key lengths, and secure modes of operation instead of outdated or deprecated options. Regularly review cryptographic standards and replace algorithms that no longer provide sufficient security against current attack capabilities.
Encrypt Data at Rest and in Transit
Identify sensitive information and apply encryption wherever protection is required. Use secure transport protocols such as TLS for data in transit and strong encryption mechanisms for stored information, while avoiding unnecessary retention of sensitive data.
Implement Secure Key Management
Protect encryption keys throughout their entire lifecycle, including generation, storage, distribution, use, rotation, and destruction. Restrict access to authorized systems and users, and avoid storing cryptographic keys directly in source code or application repositories.
Never Hardcode Keys or Secrets
Do not embed encryption keys, passwords, API secrets, or other sensitive credentials inside application code, configuration files, or publicly accessible repositories. Use dedicated secrets management or key management solutions with appropriate access controls and rotation capabilities.
Use Strong Password Hashing
Never store passwords using reversible encryption or fast, outdated hashing algorithms. Use adaptive, salted password-hashing functions such as Argon2, scrypt, bcrypt, or PBKDF2 with an appropriate work factor to make offline password cracking more difficult.
Generate Secure Random Values
Use a cryptographically secure pseudorandom number generator for keys, tokens, initialization vectors, and other security-sensitive values. Avoid predictable seeds or general-purpose random functions because insufficient entropy can make cryptographic values easier for attackers to predict.
Use Secure Initialization Vectors
Generate initialization vectors and nonces according to the requirements of the selected cryptographic mode, and never reuse values when the mode prohibits reuse. Where appropriate, use authenticated encryption to provide confidentiality and integrity together.
Enforce Secure TLS and Certificates
Protect application traffic with properly configured TLS and validate server certificates and trust chains correctly. Disable legacy protocols and insecure configurations, and consider controls such as HSTS to prevent browsers from falling back to unencrypted connections.
Regularly Test Cryptographic Controls
Cryptographic configurations should be reviewed and tested as applications evolve. Security teams should verify algorithms, protocols, certificates, key storage, secrets, and data flows through code reviews, security testing, configuration assessments, and vulnerability testing.
How ZeroThreat Helps You Identify and Fix Cryptographic Failures
Cryptographic weaknesses can appear across web applications, APIs, authentication flows, and data handling processes. ZeroThreat helps security teams uncover exploitable security issues by testing applications from an attacker’s perspective.
ZeroThreat continuously maps application attack surfaces and evaluates exposed endpoints, authenticated workflows, and API interactions. Its AI-driven testing can identify weaknesses that may contribute to sensitive data exposure and other cryptographic security risks.
The platform goes beyond simply flagging potential vulnerabilities. ZeroThreat uses controlled exploit validation to determine whether a detected weakness can actually be exploited, providing reproducible evidence and impact context while reducing false positives.
Once a vulnerability is confirmed, ZeroThreat provides proof-based findings and actionable remediation guidance to help teams prioritize fixes. Continuous testing and revalidation can then verify whether the identified security issues have been properly resolved.
Want better protection against cryptographic failure and other vulnerabilities? Let our experts help you get started. Connect With Us
To Wrap Up
Cryptographic failures are no joke, as they are one of the most critical security risks. Failing to secure your web application against this vulnerability can leave your data unprotected and could result in data theft, sensitive data exposure, data manipulation, and other risks.
While best practices to prevent cryptographic failures can help to mitigate this risk, you should also focus on continuous security testing. It will enable you to test your web application to identify security vulnerabilities that could result in security breaches.
ZeroThreat is a powerful tool for security testing. It can help discover vulnerabilities with the highest accuracy. Plus, it can provide scan results in minutes, with reports having almost zero false positives. If you want to make sure your application is secure before a hacker exploits it, sign up with ZeroThreat now!
Frequently Asked Questions
What is an example of a cryptographic failure?
A common example is storing passwords with weak or unsalted hashing algorithms, making them easier to recover through brute-force or dictionary attacks. Other examples include using outdated encryption algorithms, exposing cryptographic keys, or transmitting sensitive data without adequate TLS protection.
What is OWASP A04:2025?
Why are cryptographic failures dangerous?
How do you detect cryptographic vulnerabilities?
What are common cryptographic weaknesses?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.