 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs

Quick Overview: API gateways sit at the center of modern application security, and getting them wrong exposes everything behind them. This guide covers what an API gateway is, how it differs from API security, the biggest risks it faces, proven best practices for locking it down, and practical ways to test whether your gateway actually holds up.
APIs are now a critical path to application data and business functions, making the gateway a high-value security boundary. OWASP notes that APIs expose application logic and sensitive data, which makes them attractive targets.
The numbers make the risk harder to ignore. OWASP’s 2025 data found broken access control in 100% of the tested applications, with an average incidence rate of 3.74% for the category.
One weak control can open the door.
An API gateway can centralize authentication, authorization, traffic controls, request validation, and monitoring, but it must be configured and tested correctly. This guide breaks down API gateway architecture, security risks, practical best practices, and testing approaches to help build stronger API defenses.
A secure gateway doesn't guarantee secure APIs. Find out what's still vulnerable, free. Claim Free Scan
Table of Contents
- TL;DR: API Gateway Security at a Glance
- What is an API Gateway?
- Types of API Gateway (Based on Gateway Category)
- What is API Gateway Security?
- What is the Role of API Gateway in API Security?
- API Gateway Security vs API Security: What's the Difference
- Common API Gateway Security Risks
- Top API Gateway Security Best Practices
- Wrapping Up
TL;DR: API Gateway Security at a Glance
- An API gateway protects backend services by acting as the single, centralized entry point for all incoming API traffic.
- It defends against broken authentication, broken object-level authorization, excessive data exposure, and rate limit abuse.
- Security misconfigurations remain the most exploited API gateway risk, ahead of authentication and authorization flaws.
- Core controls include strong authentication, fine-grained authorization, TLS encryption, and rate limiting.
- Input validation and WAF integration block injection attempts before they reach backend systems.
- Mutual TLS adds a stronger trust layer for service-to-service and high-security traffic.
- Centralized logging and monitoring give teams visibility into anomalies and potential threats in real time.
- Test gateway security through penetration testing, automated vulnerability scanning, and authorization flow reviews.
- Rate limiting and payload size checks should be validated under real traffic load conditions.
- Regularly audit for deprecated APIs, loose CORS policies, and configuration drift to stay protected.
What is an API Gateway?
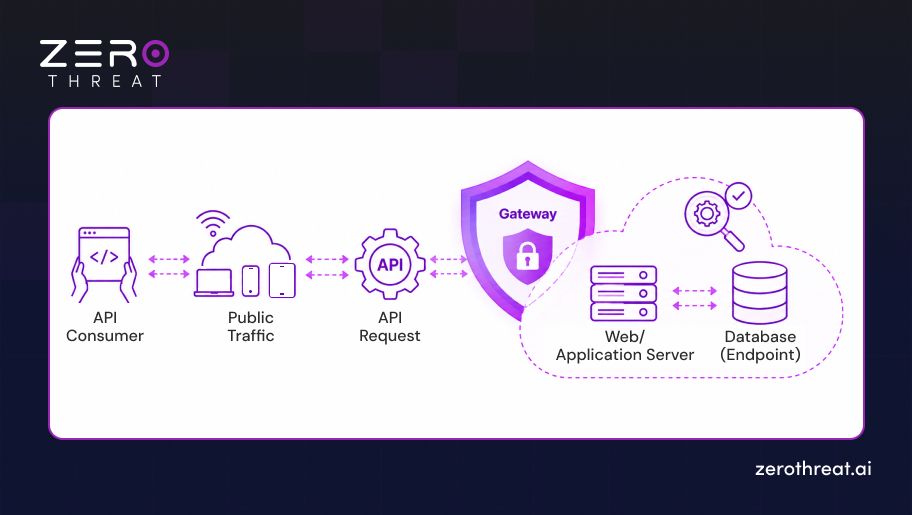
An API gateway is a server that acts as a single-entry point for all incoming traffic before it reaches your backend services. It accepts client requests, routes them to the correct internal microservice, and returns the appropriate response.
In modern application design, microservices communicate through numerous endpoints. Managing these routes individually creates unnecessary complexity. An API gateway handles traffic management, protocol translation, and request aggregation, which simplifies your entire system design.
Beyond basic routing, the gateway processes critical management functions. It monitors performance metrics, tracks active connections, and manages rate limits. This prevents backend servers from becoming overloaded during heavy traffic spikes or unexpected user activity.
By centralizing these functions at the edge, development teams can focus on writing core business logic. Backend services remain isolated from direct external contact, creating an organized and controlled environment for your digital infrastructure.
Types of API Gateway (Based on Gateway Category)
API gateways can be categorized by where they sit in the architecture and the type of traffic they manage. The following categories provide a simple view of their primary purpose, use case, and common technologies.
| Gateway Category | Primary Target | Key Benefit | Popular Tech Examples |
|---|---|---|---|
| External / Edge | Public Internet Users | Centralized security, caching, and traffic control at the network edge | AWS API Gateway, Kong, Apigee, Cloudflare |
| Internal / Mesh | Microservices | Consistent policy enforcement and observability across internal calls | Istio, Linkerd, Consul, Envoy |
| WebSocket / Real-time | Chat, Gaming, Live Streaming | Low-latency, stateful communication for live data exchange | AWS API Gateway WebSocket API, Ably, Azure SignalR |
Misconfigurations slip past gateways every day. Pentest your APIs and close the real gaps. Pentest My APIs
What is API Gateway Security?
API gateway security refers to the controls used to protect an API gateway from unauthorized access, malicious requests, abuse, and other threats. It creates a security layer between clients and the backend APIs or services they access.
These controls can include authentication, authorization, TLS encryption, request validation, rate limiting, and access policies. Together, they help ensure that only legitimate requests reach protected backend resources.
API gateway security also helps manage API traffic before it reaches application services. Rate limiting and throttling can restrict excessive requests, while request validation can reduce malformed or potentially harmful input reaching backend systems.
The gateway can also enforce secure communication through HTTPS and modern TLS configurations. This helps protect API traffic against threats such as eavesdropping and tampering while data moves between clients and services.
What is the Role of API Gateway in API Security?
The API gateway plays a central role in API security by sitting at the front line of every request, enforcing authentication, filtering threats, and applying consistent protection before traffic ever reaches backend services.
- Centralized Authentication and Authorization: The gateway verifies every client's identity using OAuth2, JWT, API keys, or mutual TLS, then checks permissions before granting access to any backend resource or service.
- Traffic Encryption in Transit: It enforces HTTPS and TLS across incoming and outgoing traffic, protecting sensitive data like tokens and credentials from interception during transmission between clients and internal services.
- Rate Limiting and Abuse Prevention: By capping how many requests a client can send within a set window, the gateway blocks brute-force attempts, credential stuffing, and denial-of-service style traffic spikes.
- Input Validation and Threat Filtering: The gateway checks incoming payloads against defined schemas and integrates with WAF rules, catching malformed requests and injection attempts before they reach any backend system.
- Consistent Policy Enforcement Across Services: Instead of every microservice handling its own security logic, the gateway applies uniform authentication, authorization, and validation rules across the entire API surface in one place.
- Centralized Logging and Monitoring: Every request passing through the gateway gets logged with details like source IP, method, and response time, giving security teams visibility for audits and threat detection.
- Reducing Backend Attack Surface: By filtering malicious or invalid traffic before it reaches internal services, the gateway shields backend systems from direct exposure and limits what attackers can probe or exploit.
- Faster Incident Response: Centralized logs and monitoring let security teams detect suspicious activity quickly, correlate events across services, and isolate compromised clients or tokens before damage spreads further.
- Scalable Security Management: As organizations add new APIs and services, the gateway lets teams apply existing security policies instantly, avoiding the need to reconfigure authentication and validation for every new integration.
API Gateway Security vs API Security: What's the Difference
People often use these terms interchangeably, but they cover different ground. API Gateway Security focuses on the entry point where requests first land, while API Security spans the entire lifecycle of an API, from design to deployment and beyond.
| Aspect | API Gateway Security | API Security |
|---|---|---|
| Primary Focus | Protects the API gateway and the traffic passing through it | Protects APIs, endpoints, data, and related components |
| Scope | Concentrated at the gateway or API entry point | Covers the complete API environment and lifecycle |
| Main Purpose | Control and filter API traffic before it reaches backend services | Prevent unauthorized access, data exposure, abuse, and API-specific attacks |
| Key Controls | Authentication, rate limiting, throttling, request filtering, TLS, access policies | Authentication, authorization, input validation, encryption, vulnerability testing, runtime protection |
| Where It Operates | Primarily at the gateway layer | Across development, deployment, and runtime environments |
| Threat Coverage | Helps address excessive traffic, unauthorized requests, and malicious API traffic | Addresses broader risks such as BOLA, broken authentication, injection, data exposure, and business logic abuse |
| Testing Approach | Tests gateway configurations, policies, routing, authentication, and traffic controls | Tests API endpoints, business logic, authorization, data handling, and vulnerabilities |
| Relationship | Forms one security layer within an API architecture | Represents the broader security strategy for APIs |
Common API Gateway Security Risks
API gateways centralize API traffic, but that also makes them an important security boundary. Weak authentication, excessive traffic, misconfiguration, and poor request validation can expose APIs and the backend services behind them.
Broken Authentication
Weak token validation, poor credential handling, or flawed authentication flows can allow attackers to bypass identity checks. Compromised API keys, JWTs, or OAuth credentials may then provide unauthorized access to protected resources.
Broken Authorization
Authentication does not confirm what a user can access. Weak authorization controls can allow attackers to access other users' objects or privileged functions by manipulating identifiers, roles, or request parameters.
Excessive Data Exposure
APIs may return more information than a client actually needs. If sensitive fields are not filtered or properly authorized, responses can expose personal data, internal identifiers, configuration details, or other information that attackers can exploit.
Resource Exhaustion
APIs can consume significant CPU, memory, bandwidth, storage, or third-party resources when processing requests. Without suitable rate limits, quotas, payload restrictions, and timeouts, attackers can trigger denial-of-service conditions or increase operating costs.
Injection Attacks
Malicious input can pass through a gateway and reach vulnerable backend components when request validation is weak. SQL injection, command injection, and script injection can compromise data or application behavior if inputs are not properly validated.
Security Misconfiguration
Incorrect gateway settings can expose APIs through overly permissive access policies, weak TLS configurations, unnecessary endpoints, or disabled security controls. Configuration drift between environments can also create gaps that attackers may exploit.
API Inventory Gaps
Unknown, outdated, or undocumented API endpoints make it difficult to apply consistent security controls. Deprecated versions, forgotten hosts, and exposed debug endpoints can remain accessible and create additional attack paths.
SSRF Through APIs
An API that accepts user-controlled URLs may allow attackers to make the backend request unintended resources. Server-side request forgery can potentially reach internal services or protected infrastructure that is not directly accessible from the internet.
Unlock enterprise-grade API penetration testing tools at a fraction of manual pentest costs. Explore Pricing
Top API Gateway Security Best Practices
Securing an API gateway requires layered controls that work together, from identity verification to traffic filtering. Here are a few best practices that help teams close common gaps and build a resilient, well-protected gateway architecture.
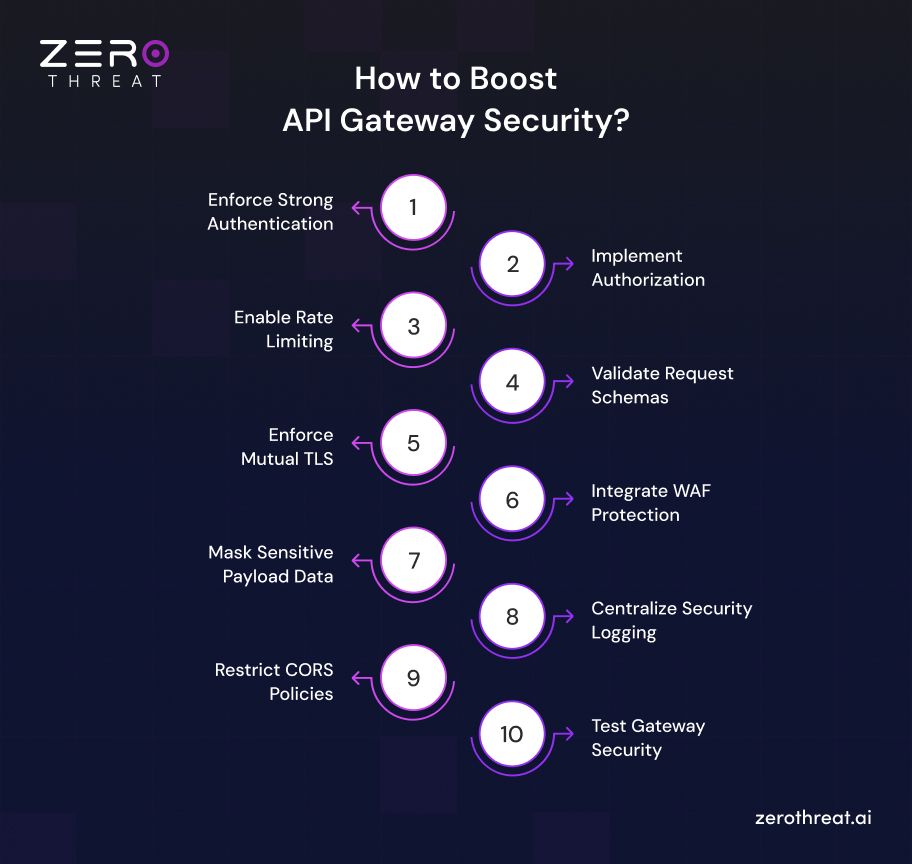
Enforce Strong Authentication
Every request reaching the gateway needs verified identity before it proceeds further. Use proven standards like OAuth2, OpenID Connect, or JWT to confirm who is calling your APIs. Weak or missing authentication opens the door to impersonation and unauthorized access across every connected service.
Avoid relying on basic API keys alone for sensitive operations. Combine authentication methods where needed, and rotate credentials regularly. A centralized identity provider keeps token issuance consistent and reduces the risk of fragmented, inconsistent authentication logic across different services.
Implement Authorization
Authentication confirms identity, but authorization determines what that identity can actually access. Apply role-based access control or attribute-based access control at the gateway to restrict actions based on defined permissions. This prevents authenticated users from reaching resources beyond their intended scope.
Granular authorization policies reduce the blast radius of a compromised account. Map permissions closely to business needs rather than granting broad access by default. Regularly review and update authorization rules as roles, services, and API endpoints evolve within your architecture.
Enable Rate Limiting
Rate limiting controls how many requests a client can send within a given timeframe. This protects backend services from being overwhelmed by traffic spikes, whether from legitimate usage surges or deliberate denial-of-service attempts targeting your infrastructure.
Configure limits based on client type, endpoint sensitivity, and expected usage patterns. Pair rate limiting with throttling and payload size restrictions for stronger coverage. This layered approach keeps services responsive while blocking abusive or automated traffic from degrading performance.
Validate Request Schemas
Every incoming request should match a predefined schema before reaching backend logic. Schema validation checks data types, required fields, and formatting rules, catching malformed or unexpected payloads that could indicate an attack attempt or integration error.
This practice also blocks injection attempts that rely on unexpected input structures. Define strict schemas for each endpoint and reject anything that deviates. Consistent validation at the gateway reduces the burden on individual services to handle malformed data safely.
Enforce Mutual TLS
Mutual TLS requires both the client and the gateway to verify each other's identity using certificates. This creates a stronger trust boundary than standard TLS, which only verifies the server, making it harder for attackers to intercept or spoof connections.
Mutual TLS works especially well for service-to-service communication and high-security environments handling sensitive data. Manage certificate lifecycles carefully, including rotation and revocation. Proper certificate management prevents expired or compromised credentials from creating unexpected security gaps.
Integrate WAF Protection
A web application firewall adds another inspection layer at the gateway, filtering traffic based on known attack signatures. It catches common threats like SQL injection, cross-site scripting, and other OWASP-recognized attack patterns before they reach backend services.
Pair WAF rules with regular updates to stay ahead of emerging threats. Custom rulesets tailored to your specific API traffic patterns improve detection accuracy. A well-tuned WAF reduces false positives while still blocking genuinely malicious requests targeting your gateway.
Mask Sensitive Payload Data
Not every field in a response needs to reach the client unfiltered. Masking or redacting sensitive data like personal identifiers, tokens, or internal system details prevents unnecessary exposure, even when a request is technically legitimate and authorized.
This practice limits damage if a response is intercepted or logged improperly. Apply data masking rules based on field sensitivity and regulatory requirements. Combining this with proper access control keeps sensitive information visible only to parties who genuinely need it.
Centralize Security Logging
Every request and response passing through the gateway should generate a log entry capturing source IP, timestamp, method, and status code. Centralized logging gives security teams a single source of truth for investigating incidents and tracking traffic patterns.
Feed these logs into a SIEM or analytics platform for real-time alerting and correlation across services. Consistent log formatting and retention policies make audits faster and help teams spot anomalous behavior before it escalates into a larger security incident.
Restrict CORS Policies
Cross-origin resource sharing policies define which domains can interact with your APIs from a browser. Overly permissive CORS settings, like allowing all origins, expose your APIs to unauthorized cross-site requests and potential data leakage.
Configure CORS to allow only trusted, specific domains rather than wildcard values. Review these policies regularly as your application's frontend origins change. Tight CORS configuration closes a commonly overlooked gap that attackers actively scan for.
Test Gateway Security
Regular security testing validates that your gateway configurations actually hold up against real attack techniques. This includes penetration testing, automated vulnerability scanning, and reviewing authentication and authorization flows for weaknesses attackers could exploit.
Testing should cover both the gateway layer and the policies it enforces, not just the backend services behind it. Continuous, automated testing catches configuration drift early, keeping your gateway security posture aligned with evolving threats and API changes.
See how ZeroThreat can uncover API vulnerabilities and bring automated security testing into your workflow. Book a Demo
Wrapping Up
API gateway security starts with controlling how clients access APIs and how requests move toward backend services. Strong authentication, authorization, encryption, and request validation establish essential controls around exposed API endpoints.
Traffic controls also matter. Rate limiting can reduce excessive requests, while WAF protection can filter malicious traffic. Secure CORS policies, sensitive data masking, and centralized logging add further layers that improve visibility and reduce unnecessary exposure.
Security teams should also treat the gateway as part of a broader API security strategy. Gateway controls cannot independently prevent issues such as BOLA or vulnerable business logic. Backend authorization and application-level protections remain essential.
Regular security testing helps verify that these controls work as intended. Testing authentication, access policies, configurations, traffic controls, and gateway-to-backend communication can uncover weaknesses before they become exploitable attack paths.
Frequently Asked Questions
Is an API gateway a WAF?
No, an API gateway is not a WAF. A gateway manages routing, authentication, and rate limiting, while a WAF specializes in filtering malicious payloads like SQL injection and cross-site scripting. Many gateways integrate WAF capabilities, but the two serve distinct, complementary security functions.
Does an API gateway replace authentication?
Does API gateway prevent BOLA?
How do you test an API gateway?
Can API gateways stop DDoS attacks?
What is the main security policy in the API gateway?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.