 ZeroThreat Wins Bronze Stevie® Award in Tech Startup of the Year Read more


All Blogs

Quick Overview: WordPress user enumeration may seem like a small security concern, but exposed usernames can provide useful information for targeted attacks. This guide explains what WordPress user enumeration is, how author archives, login responses, and the REST API can expose users, how to test for enumeration, and practical ways to reduce exposure and strengthen account security.
Every WordPress login page sits under constant watch. Not from people, but from bots.
In 2026, 94% of all login attempts across Cloudflare's network came from bots rather than real people. Many of these bots aren't guessing blindly. They're working from a list of known usernames, pulled through a technique called user enumeration.
Account takeover attacks rose 40% year over year in 2026, and username exposure plays a quiet role in that rise. A discovered username doesn't hand over access, but it removes the first obstacle standing between an attacker and your login page.
This guide breaks down how WordPress user enumeration actually works, how to test your own site for it, and the practical steps toward making your WordPress websites vulnerability-free.
Put your WordPress security to the test and uncover vulnerabilities before they become entry points. Secure My Site Now
Table of Contents
- What is WordPress User Enumeration?
- Is WordPress User Enumeration a Vulnerability?
- How WordPress User Enumeration Attack Works?
- What is the Impact of WordPress User Enumeration?
- How to Test for WordPress User Enumeration
- Best Prevention Practices for WordPress User Enumeration
- To Wrap Up
What is WordPress User Enumeration?
WordPress user enumeration is the process of identifying valid usernames or user identifiers associated with a WordPress website. It is generally considered a form of information disclosure or reconnaissance.
The goal is to determine which user accounts exist on a site. This information can be useful to attackers during later stages of an attack, especially when targeting specific accounts through credential attacks or phishing.
User enumeration does not mean that an account has been compromised. Discovering a valid username alone does not provide access to the account or its protected data. The actual risk depends on the security controls protecting those accounts.
For site owners, the focus should be on minimizing unnecessary username exposure while strengthening authentication. Controls such as strong passwords, MFA, rate limiting, and appropriate access controls can reduce the impact if account identifiers become known.
Is WordPress User Enumeration a Vulnerability?
WordPress user enumeration can be considered a security weakness or information disclosure issue when a site unnecessarily reveals valid usernames or user identifiers. Its severity depends on the exposure and the security controls protecting those accounts.
Enumeration itself does not compromise an account. It can, however, give attackers useful reconnaissance data for brute-force attacks, credential stuffing, or targeted phishing. Strong authentication, MFA, rate limiting, and access controls can reduce the associated risk.
How WordPress User Enumeration Attack Works?
Understanding how WordPress user enumeration works helps security teams audit exposure. Attackers exploit default query parameters, exposed REST API endpoints, and distinct authentication responses to harvest valid handles for targeted login attacks. Here is dive into each of the technique:
1. Author Archives
URL Format: https://example.com/?author=1
How it Works: WordPress creates a public archive page for every user who has published content on the site. When someone visits a URL containing an author ID number, WordPress often redirects to that user's archive page, and the resulting URL slug reveals their username.
Enumeration: An attacker sends sequential requests using different author ID numbers, like ?author=1, ?author=2, and so on, then records where each request redirects. The username exposed in the resulting slug confirms a valid account. This behavior depends on the site's theme and permalink settings, so it doesn't appear identically across every WordPress install.
2. Login Response Differences
URL Format: https://example.com/wp-login.php
How it Works: The WordPress login page can behave differently depending on the site's configuration, active plugins, and version. Some setups return distinguishable error messages, different response bodies, or measurable timing differences between a valid and an invalid username.
Enumeration: An attacker submits a list of possible usernames through the login form and studies the pattern of responses, error text, redirects, status codes, or response timing, to work out which ones exist. This method isn't guaranteed to work everywhere. Sites using generic error messages and consistent response handling limit this significantly.
3. WordPress REST API
URL Format: https://example.com/wp-json/wp/v2/users/
How it Works: WordPress exposes certain user information through its REST API, as documented in the official WordPress REST API handbook. Depending on site settings and permissions, publicly available details like display names and author slugs can appear in the response.
Enumeration: An attacker can query this endpoint to pull a list of public author information, including usernames tied to published posts. Private data, such as email addresses or user roles, stays protected behind authentication and permission checks. What actually gets exposed depends on how the site owner has configured REST API permissions.
Find WordPress vulnerabilities hiding beneath the surface before they cost you millions. Run a WordPress Scan
What is the Impact of WordPress User Enumeration?
Let's understand how WordPress user enumeration attacks impact websites and web applications and cause organizations to bear unpleasant results.

1. Increased Risk of Brute Force Attacks
Brute force attacks are about trying different passwords until the correct password is discovered. Once the attacker gets to know about a registered username, it becomes easier for them to attempt numerous password combinations.
If users' passwords are easily guessable, then the chances of a successful brute-force attack increase. This promotes unauthorized access, which can even lead attackers to gain complete control over the website.
2. Potential for Credential Stuffing
Credential stuffing is an attack when attackers misuse the credentials that were leaked earlier due to other data breaches to attempt logins. If users have used the same password across multiple websites, then it may increase the likelihood of credential-stuffing attacks.
3. Risks of Data Breach
Once the attacker obtains access to an account, especially an admin account, they become eligible to access, modify, remove the website's content, manage user accounts, or inject malicious code.
User enumeration attacks can cause breaches of data that lead to the exposure of confidential data and the defacement of the website where it's altered or damaged.
4. Increased Targeting of Privileged Account
Attackers primarily focus on high-level privilege accounts like administrator's accounts, as administrators' accounts generally have complete control over the website.
If attackers' attempts are successful in obtaining access to the admins' accounts, they can lead to severe repercussions such as site-wide malware installation, complete data loss, or control over user interactions.
5. Social Engineering Opportunities
With valid usernames, attackers can create more persuasive phishing emails or social engineering schemes. For instance, they might imitate someone who belongs to the organization or use information extracted from the website to dupe users into divulging passwords or performing malicious actions.
It can cause further credential compromises, unauthorized transactions, or other security breaches.
6. Adverse Effect on Website Performance
As WordPress user enumeration attacks are all about repetitive attempts to access registered users' credentials, these nasty attempts cause a significant load on the server.
The repercussions of such attempts are decreased performance, slower response times, or downtime.
How to Test for WordPress User Enumeration
WordPress user enumeration testing checks whether a website unintentionally reveals valid user identifiers through author pages, login behavior, REST API responses, or public metadata.
1. Test Author Archives
Step 1: Identify a published post and check whether it displays an author name or links to an author archive.
Step 2: Open the author link and review the URL. A format such as https://example.com/author/username/ may expose a public author identifier.
Step 3: Also check whether numeric author queries such as https://example.com/?author=1 redirect to an author page or another URL that identifies the associated user.
Step 4: Compare the results for different valid and invalid author identifiers. Consistent redirects or identifiable author pages can indicate that user discovery is possible.
WordPress author archives and author-related URLs can expose information depending on the site's configuration, theme, and content structure.
2. Test Login Response Differences
Step 1: Open the site's normal login page and submit a test username that you know exists with an intentionally incorrect password.
Step 2: Repeat the test with a username that you know does not exist.
Step 3: Compare the responses. Look for differences in error messages, response bodies, redirects, HTTP status codes, or other observable behavior.
Step 4: Check whether response timing is noticeably different between the two cases. Timing differences can sometimes provide an additional enumeration signal.
The goal is to determine whether the application provides a reliable distinction between existing and nonexistent accounts. OWASP recommends generic authentication responses to avoid creating such discrepancies.
3. Test the WordPress REST API
Step 1: Check whether the site's REST API is publicly accessible by requesting:
https://example.com/wp-json/wp/v2/users/
Step 2: Review the response to determine whether it returns public user or author information. The WordPress REST API user endpoint supports fields such as user IDs, display names, author URLs, and slugs in appropriate public contexts.
Step 3: Determine whether the returned information is sufficient to identify valid users or author accounts.
Step 4: Do not assume that every field in the user schema is publicly exposed. WordPress applies different contexts and permissions to user data, so verify what the specific site actually returns.
Testing Note: Perform these checks only on WordPress websites you own or are explicitly authorized to assess. The objective is to identify unnecessary information disclosure so it can be reduced without disrupting legitimate site functionality.
Best Prevention Practices for WordPress User Enumeration
Preventing WordPress user enumeration requires a mix of configuration changes and stronger authentication controls. The following practices reduce unnecessary username disclosure while limiting the damage a discovered username can cause.
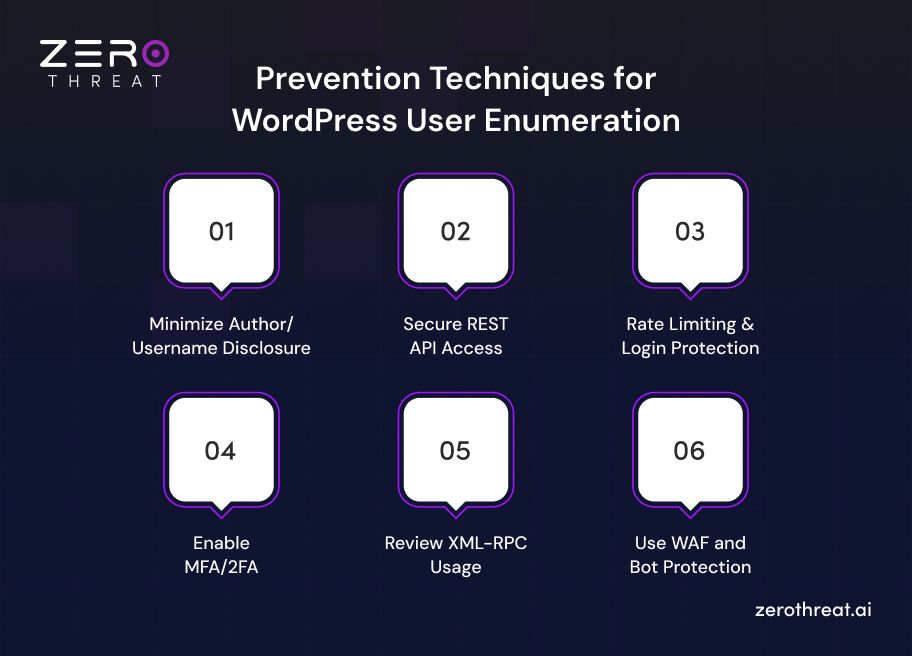
Minimize Author/Username Disclosure
Consider whether public author archives serve your site's purpose. Blogs with multiple contributors may need them for attribution, but single-author sites can disable or redirect these pages. Weigh this against SEO impact, since author pages sometimes support content discoverability and internal linking.
Secure REST API Access
Apply least-privilege principles to REST API permissions instead of disabling the API entirely. Restrict only the specific endpoints or fields exposing unnecessary user data. A blanket shutdown can break plugins, themes, and integrations that depend on REST API functionality to operate correctly.
Rate Limiting & Login Protection
Add rate limiting to your login page to slow down automated username and password attempts. This control primarily reduces brute force and credential stuffing risk rather than blocking enumeration itself, but it significantly raises the cost and time required for an attacker to succeed.
Enable MFA/2FA
Multi-factor authentication doesn't hide usernames, but it adds a second layer of verification after a password is entered. Even if an attacker discovers a valid username and guesses the correct password, MFA can still stop unauthorized access before it happens.
Review XML-RPC Usage
XML-RPC is a separate attack surface that can support authentication-related abuse in some configurations. If your site doesn't rely on XML-RPC-dependent features like remote publishing or certain mobile apps, disabling it removes one more avenue attackers can use to test credentials.
Use WAF and Bot Protection
A web application firewall combined with bot detection can catch repeated enumeration probes before they succeed. Configure it to monitor for rapid sequential requests, unusual login patterns, and known scanning signatures, then set alerts for suspicious activity so your team can respond quickly.
Not sure where your WordPress security gaps begin? Let our experts help you identify them. Connect With Us
To Wrap Up
WordPress user enumeration is primarily an information disclosure concern that can reveal valid usernames or user identifiers. While it does not compromise accounts by itself, it can provide useful reconnaissance data for targeted credential and phishing attacks.
Reducing unnecessary username exposure starts with reviewing author archives, REST API responses, login behavior, and public user metadata. Strong authentication, MFA, rate limiting, appropriate API permissions, and continuous monitoring further reduce the risk of account compromise.
A proactive security approach helps identify enumeration exposure before attackers can use it. ZeroThreat can help security teams continuously test WordPress applications for vulnerabilities and security gaps. Sign up with ZeroThreat to strengthen your application security posture.
Frequently Asked Questions
What are the risks of WordPress user enumeration?
WordPress user enumeration can reveal valid usernames or user identifiers that attackers can use for reconnaissance. This information can make brute-force attacks, credential stuffing, and targeted phishing more effective. Enumeration does not compromise an account by itself. The primary risk comes from the attacks that may follow successful account discovery.
What does enumeration mean in cybersecurity?
What are the types of WordPress user enumeration?
How do I test WordPress user enumeration?
How do I stop WordPress user enumeration?


Explore ZeroThreat
Automate security testing, save time, and avoid the pitfalls of manual work with ZeroThreat.